CVE-2024-52291 (GCVE-0-2024-52291)
Vulnerability from cvelistv5 – Published: 2024-11-13 16:12 – Updated: 2024-11-13 18:52- CWE-22 - Improper Limitation of a Pathname to a Restricted Directory ('Path Traversal')
| URL | Tags |
|---|---|
| https://github.com/craftcms/cms/security/advisori… | x_refsource_CONFIRM |
| Vendor | Product | Version | CPE status | |
|---|---|---|---|---|
| craftcms | cms |
Affected:
>= 5.0.0-RC1, < 5.4.6
Affected: >= 4.0.0-RC1, < 4.12.5 |
guessed | |
| craftcms | craft_cms |
Affected:
0 , ≤ 5.0.0-RC1
(custom)
Affected: 0 , < 5.4.6 (custom) Affected: 0 , ≤ 4.0.0-RC1 (custom) Affected: 0 , < 4.12.5 (custom) cpe:2.3:a:craftcms:craft_cms:*:*:*:*:*:*:*:* |
{
"containers": {
"adp": [
{
"affected": [
{
"cpes": [
"cpe:2.3:a:craftcms:craft_cms:*:*:*:*:*:*:*:*"
],
"defaultStatus": "unknown",
"product": "craft_cms",
"vendor": "craftcms",
"versions": [
{
"lessThanOrEqual": "5.0.0-RC1",
"status": "affected",
"version": "0",
"versionType": "custom"
},
{
"lessThan": "5.4.6",
"status": "affected",
"version": "0",
"versionType": "custom"
},
{
"lessThanOrEqual": "4.0.0-RC1",
"status": "affected",
"version": "0",
"versionType": "custom"
},
{
"lessThan": "4.12.5",
"status": "affected",
"version": "0",
"versionType": "custom"
}
]
}
],
"metrics": [
{
"other": {
"content": {
"id": "CVE-2024-52291",
"options": [
{
"Exploitation": "poc"
},
{
"Automatable": "no"
},
{
"Technical Impact": "total"
}
],
"role": "CISA Coordinator",
"timestamp": "2024-11-13T18:50:50.793331Z",
"version": "2.0.3"
},
"type": "ssvc"
}
}
],
"providerMetadata": {
"dateUpdated": "2024-11-13T18:52:15.774Z",
"orgId": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
"shortName": "CISA-ADP"
},
"title": "CISA ADP Vulnrichment"
}
],
"cna": {
"affected": [
{
"product": "cms",
"vendor": "craftcms",
"versions": [
{
"status": "affected",
"version": "\u003e= 5.0.0-RC1, \u003c 5.4.6"
},
{
"status": "affected",
"version": "\u003e= 4.0.0-RC1, \u003c 4.12.5"
}
]
}
],
"descriptions": [
{
"lang": "en",
"value": "Craft is a content management system (CMS). A vulnerability in CraftCMS allows an attacker to bypass local file system validation by utilizing a double file:// scheme (e.g., file://file:////). This enables the attacker to specify sensitive folders as the file system, leading to potential file overwriting through malicious uploads, unauthorized access to sensitive files, and, under certain conditions, remote code execution (RCE) via Server-Side Template Injection (SSTI) payloads. Note that this will only work if you have an authenticated administrator account with allowAdminChanges enabled. This is fixed in 5.4.6 and 4.12.5."
}
],
"metrics": [
{
"cvssV3_1": {
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "HIGH",
"baseScore": 8.5,
"baseSeverity": "HIGH",
"confidentialityImpact": "HIGH",
"integrityImpact": "HIGH",
"privilegesRequired": "HIGH",
"scope": "CHANGED",
"userInteraction": "REQUIRED",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:H/UI:R/S:C/C:H/I:H/A:H",
"version": "3.1"
}
}
],
"problemTypes": [
{
"descriptions": [
{
"cweId": "CWE-22",
"description": "CWE-22: Improper Limitation of a Pathname to a Restricted Directory (\u0027Path Traversal\u0027)",
"lang": "en",
"type": "CWE"
}
]
}
],
"providerMetadata": {
"dateUpdated": "2024-11-13T16:12:14.803Z",
"orgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
"shortName": "GitHub_M"
},
"references": [
{
"name": "https://github.com/craftcms/cms/security/advisories/GHSA-jrh5-vhr9-qh7q",
"tags": [
"x_refsource_CONFIRM"
],
"url": "https://github.com/craftcms/cms/security/advisories/GHSA-jrh5-vhr9-qh7q"
}
],
"source": {
"advisory": "GHSA-jrh5-vhr9-qh7q",
"discovery": "UNKNOWN"
},
"title": "Craft has a Local File System Validation Bypass Leading to File Overwrite, Sensitive File Access, and Potential Code Execution"
}
},
"cveMetadata": {
"assignerOrgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
"assignerShortName": "GitHub_M",
"cveId": "CVE-2024-52291",
"datePublished": "2024-11-13T16:12:14.803Z",
"dateReserved": "2024-11-06T19:00:26.394Z",
"dateUpdated": "2024-11-13T18:52:15.774Z",
"state": "PUBLISHED"
},
"dataType": "CVE_RECORD",
"dataVersion": "5.1",
"vulnerability-lookup:meta": {
"epss": {
"cve": "CVE-2024-52291",
"date": "2026-11-14",
"epss": "0.01253",
"percentile": "0.69928"
},
"nvd": {
"cve": {
"affected": [
{
"affectedData": [
{
"product": "cms",
"vendor": "craftcms",
"versions": [
{
"status": "affected",
"version": "\u003e= 5.0.0-RC1, \u003c 5.4.6"
},
{
"status": "affected",
"version": "\u003e= 4.0.0-RC1, \u003c 4.12.5"
}
]
}
],
"source": "security-advisories@github.com"
},
{
"affectedData": [
{
"cpes": [
"cpe:2.3:a:craftcms:craft_cms:*:*:*:*:*:*:*:*"
],
"defaultStatus": "unknown",
"product": "craft_cms",
"vendor": "craftcms",
"versions": [
{
"lessThanOrEqual": "5.0.0-RC1",
"status": "affected",
"version": "0",
"versionType": "custom"
},
{
"lessThan": "5.4.6",
"status": "affected",
"version": "0",
"versionType": "custom"
},
{
"lessThanOrEqual": "4.0.0-RC1",
"status": "affected",
"version": "0",
"versionType": "custom"
},
{
"lessThan": "4.12.5",
"status": "affected",
"version": "0",
"versionType": "custom"
}
]
}
],
"source": "134c704f-9b21-4f2e-91b3-4a467353bcc0"
}
],
"configurations": [
{
"nodes": [
{
"cpeMatch": [
{
"criteria": "cpe:2.3:a:craftcms:craft_cms:*:*:*:*:*:*:*:*",
"matchCriteriaId": "D75081F6-DA85-4F2D-B57B-5F4E8864B8F8",
"versionEndExcluding": "4.12.5",
"versionStartExcluding": "4.0.0",
"vulnerable": true
},
{
"criteria": "cpe:2.3:a:craftcms:craft_cms:*:*:*:*:*:*:*:*",
"matchCriteriaId": "E8C229F2-C3B1-4715-97FD-53AD88FB124F",
"versionEndExcluding": "5.4.6",
"versionStartExcluding": "5.0.0",
"vulnerable": true
},
{
"criteria": "cpe:2.3:a:craftcms:craft_cms:4.0.0:rc1:*:*:*:*:*:*",
"matchCriteriaId": "CC2F40FC-7C27-456A-B16D-679410D1D5CF",
"vulnerable": true
},
{
"criteria": "cpe:2.3:a:craftcms:craft_cms:4.0.0:rc2:*:*:*:*:*:*",
"matchCriteriaId": "FBAA8227-04F8-404C-907B-B0162B325F5A",
"vulnerable": true
},
{
"criteria": "cpe:2.3:a:craftcms:craft_cms:4.0.0:rc3:*:*:*:*:*:*",
"matchCriteriaId": "21B28E2C-327A-4CE6-ACAD-97E459712A55",
"vulnerable": true
},
{
"criteria": "cpe:2.3:a:craftcms:craft_cms:5.0.0:rc1:*:*:*:*:*:*",
"matchCriteriaId": "8D8E02D1-601A-4E2B-B619-4775BFDB72D0",
"vulnerable": true
}
],
"negate": false,
"operator": "OR"
}
]
}
],
"cveTags": [],
"descriptions": [
{
"lang": "en",
"value": "Craft is a content management system (CMS). A vulnerability in CraftCMS allows an attacker to bypass local file system validation by utilizing a double file:// scheme (e.g., file://file:////). This enables the attacker to specify sensitive folders as the file system, leading to potential file overwriting through malicious uploads, unauthorized access to sensitive files, and, under certain conditions, remote code execution (RCE) via Server-Side Template Injection (SSTI) payloads. Note that this will only work if you have an authenticated administrator account with allowAdminChanges enabled. This is fixed in 5.4.6 and 4.12.5."
},
{
"lang": "es",
"value": "Craft es un sistema de gesti\u00f3n de contenido (CMS). Una vulnerabilidad en CraftCMS permite a un atacante eludir la validaci\u00f3n del sistema de archivos local mediante un esquema file:// doble (por ejemplo, file://file:////). Esto permite al atacante especificar carpetas confidenciales como sistema de archivos, lo que lleva a una posible sobrescritura de archivos mediante cargas maliciosas, acceso no autorizado a archivos confidenciales y, en determinadas condiciones, ejecuci\u00f3n remota de c\u00f3digo (RCE) mediante payloads de Server-Side Template Injection (SSTI). Tenga en cuenta que esto solo funcionar\u00e1 si tiene una cuenta de administrador autenticada con allowAdminChanges habilitado. Esto se solucion\u00f3 en 5.4.6 y 4.12.5."
}
],
"id": "CVE-2024-52291",
"lastModified": "2026-06-17T08:06:57.110",
"metrics": {
"cvssMetricV31": [
{
"cvssData": {
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "HIGH",
"baseScore": 8.4,
"baseSeverity": "HIGH",
"confidentialityImpact": "HIGH",
"integrityImpact": "HIGH",
"privilegesRequired": "HIGH",
"scope": "CHANGED",
"userInteraction": "REQUIRED",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:H/UI:R/S:C/C:H/I:H/A:H",
"version": "3.1"
},
"exploitabilityScore": 1.7,
"impactScore": 6.0,
"source": "security-advisories@github.com",
"type": "Secondary"
},
{
"cvssData": {
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "HIGH",
"baseScore": 7.2,
"baseSeverity": "HIGH",
"confidentialityImpact": "HIGH",
"integrityImpact": "HIGH",
"privilegesRequired": "HIGH",
"scope": "UNCHANGED",
"userInteraction": "NONE",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H",
"version": "3.1"
},
"exploitabilityScore": 1.2,
"impactScore": 5.9,
"source": "nvd@nist.gov",
"type": "Primary"
}
],
"ssvcV203": [
{
"source": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
"ssvcData": {
"id": "CVE-2024-52291",
"options": [
{
"exploitation": "poc"
},
{
"automatable": "no"
},
{
"technicalImpact": "total"
}
],
"role": "CISA Coordinator",
"timestamp": "2024-11-13T18:50:50.793331Z",
"version": "2.0.3"
}
}
]
},
"published": "2024-11-13T17:15:12.087",
"references": [
{
"source": "security-advisories@github.com",
"tags": [
"Exploit",
"Vendor Advisory"
],
"url": "https://github.com/craftcms/cms/security/advisories/GHSA-jrh5-vhr9-qh7q"
}
],
"sourceIdentifier": "security-advisories@github.com",
"vulnStatus": "Analyzed",
"weaknesses": [
{
"description": [
{
"lang": "en",
"value": "CWE-22"
}
],
"source": "security-advisories@github.com",
"type": "Secondary"
}
]
}
},
"redhat_vex": {
"current_release_date": "2025-05-28T22:04:21+00:00",
"cve": "CVE-2024-52291",
"id": "CVE-2024-52291",
"initial_release_date": "2024-01-01T00:00:00+00:00",
"product_status:known_not_affected": "1",
"source": "Red Hat CSAF VEX",
"status": "final",
"title": "Craft has a Local File System Validation Bypass Leading to File Overwrite, Sensitive File Access, and Potential Code Execution",
"url": "https://security.access.redhat.com/data/csaf/v2/vex/2024/cve-2024-52291.json",
"version": "3"
},
"vulnrichment": {
"containers": {
"adp": [
{
"affected": [
{
"cpes": [
"cpe:2.3:a:craftcms:craft_cms:*:*:*:*:*:*:*:*"
],
"defaultStatus": "unknown",
"product": "craft_cms",
"vendor": "craftcms",
"versions": [
{
"lessThanOrEqual": "5.0.0-RC1",
"status": "affected",
"version": "0",
"versionType": "custom"
},
{
"lessThan": "5.4.6",
"status": "affected",
"version": "0",
"versionType": "custom"
},
{
"lessThanOrEqual": "4.0.0-RC1",
"status": "affected",
"version": "0",
"versionType": "custom"
},
{
"lessThan": "4.12.5",
"status": "affected",
"version": "0",
"versionType": "custom"
}
]
}
],
"metrics": [
{
"other": {
"content": {
"id": "CVE-2024-52291",
"options": [
{
"Exploitation": "poc"
},
{
"Automatable": "no"
},
{
"Technical Impact": "total"
}
],
"role": "CISA Coordinator",
"timestamp": "2024-11-13T18:50:50.793331Z",
"version": "2.0.3"
},
"type": "ssvc"
}
}
],
"providerMetadata": {
"dateUpdated": "2024-11-13T18:52:03.472Z",
"orgId": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
"shortName": "CISA-ADP"
},
"title": "CISA ADP Vulnrichment"
}
],
"cna": {
"affected": [
{
"product": "cms",
"vendor": "craftcms",
"versions": [
{
"status": "affected",
"version": "\u003e= 5.0.0-RC1, \u003c 5.4.6"
},
{
"status": "affected",
"version": "\u003e= 4.0.0-RC1, \u003c 4.12.5"
}
]
}
],
"descriptions": [
{
"lang": "en",
"value": "Craft is a content management system (CMS). A vulnerability in CraftCMS allows an attacker to bypass local file system validation by utilizing a double file:// scheme (e.g., file://file:////). This enables the attacker to specify sensitive folders as the file system, leading to potential file overwriting through malicious uploads, unauthorized access to sensitive files, and, under certain conditions, remote code execution (RCE) via Server-Side Template Injection (SSTI) payloads. Note that this will only work if you have an authenticated administrator account with allowAdminChanges enabled. This is fixed in 5.4.6 and 4.12.5."
}
],
"metrics": [
{
"cvssV3_1": {
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "HIGH",
"baseScore": 8.5,
"baseSeverity": "HIGH",
"confidentialityImpact": "HIGH",
"integrityImpact": "HIGH",
"privilegesRequired": "HIGH",
"scope": "CHANGED",
"userInteraction": "REQUIRED",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:H/UI:R/S:C/C:H/I:H/A:H",
"version": "3.1"
}
}
],
"problemTypes": [
{
"descriptions": [
{
"cweId": "CWE-22",
"description": "CWE-22: Improper Limitation of a Pathname to a Restricted Directory (\u0027Path Traversal\u0027)",
"lang": "en",
"type": "CWE"
}
]
}
],
"providerMetadata": {
"dateUpdated": "2024-11-13T16:12:14.803Z",
"orgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
"shortName": "GitHub_M"
},
"references": [
{
"name": "https://github.com/craftcms/cms/security/advisories/GHSA-jrh5-vhr9-qh7q",
"tags": [
"x_refsource_CONFIRM"
],
"url": "https://github.com/craftcms/cms/security/advisories/GHSA-jrh5-vhr9-qh7q"
}
],
"source": {
"advisory": "GHSA-jrh5-vhr9-qh7q",
"discovery": "UNKNOWN"
},
"title": "Craft has a Local File System Validation Bypass Leading to File Overwrite, Sensitive File Access, and Potential Code Execution"
}
},
"cveMetadata": {
"assignerOrgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
"assignerShortName": "GitHub_M",
"cveId": "CVE-2024-52291",
"datePublished": "2024-11-13T16:12:14.803Z",
"dateReserved": "2024-11-06T19:00:26.394Z",
"dateUpdated": "2024-11-13T18:52:15.774Z",
"state": "PUBLISHED"
},
"dataType": "CVE_RECORD",
"dataVersion": "5.1"
}
}
}
BDU:2025-01099 (CVE-2024-52291)
Vulnerability from fstec – Published: 2025-02-04 – Updated: 2025-02-04 – View on bdu.fstec.ru Exploit publicly available Fixed- CWE-22 - Неверное ограничение имени пути к каталогу с ограниченным доступом («Обход пути»)
{
  "CVSS 2.0": "AV:N/AC:L/Au:S/C:C/I:C/A:C",
  "CVSS 3.0": "AV:N/AC:L/PR:H/UI:R/S:C/C:H/I:H/A:H",
  "CVSS 4.0": null,
  "remediation_\u0418\u0434\u0435\u043d\u0442\u0438\u0444\u0438\u043a\u0430\u0442\u043e\u0440": null,
  "remediation_\u041d\u0430\u0438\u043c\u0435\u043d\u043e\u0432\u0430\u043d\u0438\u0435": null,
  "\u0412\u0435\u043d\u0434\u043e\u0440 \u041f\u041e": "Crafter Software Corporation",
  "\u0412\u0435\u0440\u0441\u0438\u044f \u041f\u041e": "\u043e\u0442 5.0.0-RC1 \u0434\u043e 5.4.6 (Crafter CMS), \u043e\u0442 4.0.0-RC1 \u0434\u043e 4.12.5 (Crafter CMS)",
  "\u0412\u043e\u0437\u043c\u043e\u0436\u043d\u044b\u0435 \u043c\u0435\u0440\u044b \u043f\u043e \u0443\u0441\u0442\u0440\u0430\u043d\u0435\u043d\u0438\u044e": "\u0418\u0441\u043f\u043e\u043b\u044c\u0437\u043e\u0432\u0430\u043d\u0438\u0435 \u0440\u0435\u043a\u043e\u043c\u0435\u043d\u0434\u0430\u0446\u0438\u0439:\nhttps://github.com/craftcms/cms/security/advisories/GHSA-jrh5-vhr9-qh7q",
  "\u0414\u0430\u0442\u0430 \u0432\u044b\u044f\u0432\u043b\u0435\u043d\u0438\u044f": "13.11.2024",
  "\u0414\u0430\u0442\u0430 \u043f\u043e\u0441\u043b\u0435\u0434\u043d\u0435\u0433\u043e \u043e\u0431\u043d\u043e\u0432\u043b\u0435\u043d\u0438\u044f": "04.02.2025",
  "\u0414\u0430\u0442\u0430 \u043f\u0443\u0431\u043b\u0438\u043a\u0430\u0446\u0438\u0438": "04.02.2025",
  "\u0418\u0434\u0435\u043d\u0442\u0438\u0444\u0438\u043a\u0430\u0442\u043e\u0440": "BDU:2025-01099",
  "\u0418\u0434\u0435\u043d\u0442\u0438\u0444\u0438\u043a\u0430\u0442\u043e\u0440\u044b \u0434\u0440\u0443\u0433\u0438\u0445 \u0441\u0438\u0441\u0442\u0435\u043c \u043e\u043f\u0438\u0441\u0430\u043d\u0438\u0439 \u0443\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u0438": "CVE-2024-52291",
  "\u0418\u043d\u0444\u043e\u0440\u043c\u0430\u0446\u0438\u044f \u043e\u0431 \u0443\u0441\u0442\u0440\u0430\u043d\u0435\u043d\u0438\u0438": "\u0423\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u044c \u0443\u0441\u0442\u0440\u0430\u043d\u0435\u043d\u0430",
  "\u041a\u043b\u0430\u0441\u0441 \u0443\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u0438": "\u0423\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u044c \u043a\u043e\u0434\u0430",
  "\u041d\u0430\u0437\u0432\u0430\u043d\u0438\u0435 \u041f\u041e": "Crafter CMS",
  "\u041d\u0430\u0438\u043c\u0435\u043d\u043e\u0432\u0430\u043d\u0438\u0435 \u041e\u0421 \u0438 \u0442\u0438\u043f \u0430\u043f\u043f\u0430\u0440\u0430\u0442\u043d\u043e\u0439 \u043f\u043b\u0430\u0442\u0444\u043e\u0440\u043c\u044b": null,
  "\u041d\u0430\u0438\u043c\u0435\u043d\u043e\u0432\u0430\u043d\u0438\u0435 \u0443\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u0438": "\u0423\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u044c \u0441\u0438\u0441\u0442\u0435\u043c\u044b \u0443\u043f\u0440\u0430\u0432\u043b\u0435\u043d\u0438\u044f \u043a\u043e\u043d\u0442\u0435\u043d\u0442\u043e\u043c Craft CMS, \u0441\u0432\u044f\u0437\u0430\u043d\u043d\u0430\u044f \u0441 \u043d\u0435\u0432\u0435\u0440\u043d\u044b\u043c \u043e\u0433\u0440\u0430\u043d\u0438\u0447\u0435\u043d\u0438\u0435\u043c \u0438\u043c\u0435\u043d\u0438 \u043f\u0443\u0442\u0438 \u043a \u043a\u0430\u0442\u0430\u043b\u043e\u0433\u0443 \u0441 \u043e\u0433\u0440\u0430\u043d\u0438\u0447\u0435\u043d\u043d\u044b\u043c \u0434\u043e\u0441\u0442\u0443\u043f\u043e\u043c, \u043f\u043e\u0437\u0432\u043e\u043b\u044f\u044e\u0449\u0430\u044f \u043d\u0430\u0440\u0443\u0448\u0438\u0442\u0435\u043b\u044e \u0432\u044b\u043f\u043e\u043b\u043d\u0438\u0442\u044c \u043f\u0440\u043e\u0438\u0437\u0432\u043e\u043b\u044c\u043d\u044b\u0439 \u043a\u043e\u0434 \u0438\u043b\u0438 \u0440\u0435\u0430\u043b\u0438\u0437\u043e\u0432\u0430\u0442\u044c \u0430\u0442\u0430\u043a\u0443 \u0432\u043d\u0435\u0434\u0440\u0435\u043d\u0438\u044f \u0448\u0430\u0431\u043b\u043e\u043d\u043e\u0432 \u043d\u0430 \u0441\u0442\u043e\u0440\u043e\u043d\u0435 \u0441\u0435\u0440\u0432\u0435\u0440\u0430 (Server Side Template Injection (SSTI))",
  "\u041d\u0430\u043b\u0438\u0447\u0438\u0435 \u044d\u043a\u0441\u043f\u043b\u043e\u0439\u0442\u0430": "\u0421\u0443\u0449\u0435\u0441\u0442\u0432\u0443\u0435\u0442 \u0432 \u043e\u0442\u043a\u0440\u044b\u0442\u043e\u043c \u0434\u043e\u0441\u0442\u0443\u043f\u0435",
  "\u041e\u043f\u0438\u0441\u0430\u043d\u0438\u0435 \u043e\u0448\u0438\u0431\u043a\u0438 CWE": "\u041d\u0435\u0432\u0435\u0440\u043d\u043e\u0435 \u043e\u0433\u0440\u0430\u043d\u0438\u0447\u0435\u043d\u0438\u0435 \u0438\u043c\u0435\u043d\u0438 \u043f\u0443\u0442\u0438 \u043a \u043a\u0430\u0442\u0430\u043b\u043e\u0433\u0443 \u0441 \u043e\u0433\u0440\u0430\u043d\u0438\u0447\u0435\u043d\u043d\u044b\u043c \u0434\u043e\u0441\u0442\u0443\u043f\u043e\u043c (\u00ab\u041e\u0431\u0445\u043e\u0434 \u043f\u0443\u0442\u0438\u00bb) (CWE-22)",
  "\u041e\u043f\u0438\u0441\u0430\u043d\u0438\u0435 \u0443\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u0438": "\u0423\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u044c \u0441\u0438\u0441\u0442\u0435\u043c\u044b \u0443\u043f\u0440\u0430\u0432\u043b\u0435\u043d\u0438\u044f \u043a\u043e\u043d\u0442\u0435\u043d\u0442\u043e\u043c Craft CMS \u0441\u0432\u044f\u0437\u0430\u043d\u0430 \u0441 \u043d\u0435\u0432\u0435\u0440\u043d\u044b\u043c \u043e\u0433\u0440\u0430\u043d\u0438\u0447\u0435\u043d\u0438\u0435\u043c \u0438\u043c\u0435\u043d\u0438 \u043f\u0443\u0442\u0438 \u043a \u043a\u0430\u0442\u0430\u043b\u043e\u0433\u0443 \u0441 \u043e\u0433\u0440\u0430\u043d\u0438\u0447\u0435\u043d\u043d\u044b\u043c \u0434\u043e\u0441\u0442\u0443\u043f\u043e\u043c. \u042d\u043a\u0441\u043f\u043b\u0443\u0430\u0442\u0430\u0446\u0438\u044f \u0443\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u0438 \u043c\u043e\u0436\u0435\u0442 \u043f\u043e\u0437\u0432\u043e\u043b\u0438\u0442\u044c \u043d\u0430\u0440\u0443\u0448\u0438\u0442\u0435\u043b\u044e, \u0434\u0435\u0439\u0441\u0442\u0432\u0443\u044e\u0449\u0435\u043c\u0443 \u0443\u0434\u0430\u043b\u0435\u043d\u043d\u043e, \u0432\u044b\u043f\u043e\u043b\u043d\u0438\u0442\u044c \u043f\u0440\u043e\u0438\u0437\u0432\u043e\u043b\u044c\u043d\u044b\u0439 \u043a\u043e\u0434 \u0438\u043b\u0438 \u0440\u0435\u0430\u043b\u0438\u0437\u043e\u0432\u0430\u0442\u044c \u0430\u0442\u0430\u043a\u0443 \u0432\u043d\u0435\u0434\u0440\u0435\u043d\u0438\u044f \u0448\u0430\u0431\u043b\u043e\u043d\u043e\u0432 \u043d\u0430 \u0441\u0442\u043e\u0440\u043e\u043d\u0435 \u0441\u0435\u0440\u0432\u0435\u0440\u0430 (Server Side Template Injection (SSTI))",
  "\u041f\u043e\u0441\u043b\u0435\u0434\u0441\u0442\u0432\u0438\u044f \u044d\u043a\u0441\u043f\u043b\u0443\u0430\u0442\u0430\u0446\u0438\u0438 \u0443\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u0438": null,
  "\u041f\u0440\u043e\u0447\u0430\u044f \u0438\u043d\u0444\u043e\u0440\u043c\u0430\u0446\u0438\u044f": null,
  "\u0421\u0432\u044f\u0437\u044c \u0441 \u0438\u043d\u0446\u0438\u0434\u0435\u043d\u0442\u0430\u043c\u0438 \u0418\u0411": "\u0414\u0430\u043d\u043d\u044b\u0435 \u0443\u0442\u043e\u0447\u043d\u044f\u044e\u0442\u0441\u044f",
  "\u0421\u043e\u0441\u0442\u043e\u044f\u043d\u0438\u0435 \u0443\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u0438": "\u041e\u043f\u0443\u0431\u043b\u0438\u043a\u043e\u0432\u0430\u043d\u0430",
  "\u0421\u043f\u043e\u0441\u043e\u0431 \u0443\u0441\u0442\u0440\u0430\u043d\u0435\u043d\u0438\u044f": "\u041e\u0431\u043d\u043e\u0432\u043b\u0435\u043d\u0438\u0435 \u043f\u0440\u043e\u0433\u0440\u0430\u043c\u043c\u043d\u043e\u0433\u043e \u043e\u0431\u0435\u0441\u043f\u0435\u0447\u0435\u043d\u0438\u044f",
  "\u0421\u043f\u043e\u0441\u043e\u0431 \u044d\u043a\u0441\u043f\u043b\u0443\u0430\u0442\u0430\u0446\u0438\u0438": "\u041c\u0430\u043d\u0438\u043f\u0443\u043b\u0438\u0440\u043e\u0432\u0430\u043d\u0438\u0435 \u0440\u0435\u0441\u0443\u0440\u0441\u0430\u043c\u0438",
  "\u0421\u0441\u044b\u043b\u043a\u0438 \u043d\u0430 \u0438\u0441\u0442\u043e\u0447\u043d\u0438\u043a\u0438": "https://github.com/craftcms/cms/security/advisories/GHSA-jrh5-vhr9-qh7q",
  "\u0421\u0442\u0430\u0442\u0443\u0441 \u0443\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u0438": "\u041f\u043e\u0434\u0442\u0432\u0435\u0440\u0436\u0434\u0435\u043d\u0430 \u043f\u0440\u043e\u0438\u0437\u0432\u043e\u0434\u0438\u0442\u0435\u043b\u0435\u043c",
  "\u0422\u0438\u043f \u041f\u041e": "\u041f\u0440\u0438\u043a\u043b\u0430\u0434\u043d\u043e\u0435 \u041f\u041e \u0438\u043d\u0444\u043e\u0440\u043c\u0430\u0446\u0438\u043e\u043d\u043d\u044b\u0445 \u0441\u0438\u0441\u0442\u0435\u043c",
  "\u0422\u0438\u043f \u043e\u0448\u0438\u0431\u043a\u0438 CWE": "CWE-22",
  "\u0423\u0440\u043e\u0432\u0435\u043d\u044c \u043e\u043f\u0430\u0441\u043d\u043e\u0441\u0442\u0438 \u0443\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u0438": "\u0412\u044b\u0441\u043e\u043a\u0438\u0439 \u0443\u0440\u043e\u0432\u0435\u043d\u044c \u043e\u043f\u0430\u0441\u043d\u043e\u0441\u0442\u0438 (\u0431\u0430\u0437\u043e\u0432\u0430\u044f \u043e\u0446\u0435\u043d\u043a\u0430 CVSS 2.0 \u0441\u043e\u0441\u0442\u0430\u0432\u043b\u044f\u0435\u0442 9)\n\u0412\u044b\u0441\u043e\u043a\u0438\u0439 \u0443\u0440\u043e\u0432\u0435\u043d\u044c \u043e\u043f\u0430\u0441\u043d\u043e\u0441\u0442\u0438 (\u0431\u0430\u0437\u043e\u0432\u0430\u044f \u043e\u0446\u0435\u043d\u043a\u0430 CVSS 3.0 \u0441\u043e\u0441\u0442\u0430\u0432\u043b\u044f\u0435\u0442 8,4)"
}
FKIE_CVE-2024-52291
Vulnerability from fkie_nvd - Published: 2024-11-13 17:15 - Updated: 2026-06-17 08:067.2 (High) - CVSS:3.1/
| URL | Tags | ||
|---|---|---|---|
| security-advisories@github.com | https://github.com/craftcms/cms/security/advisories/GHSA-jrh5-vhr9-qh7q | Exploit, Vendor Advisory |
{
  "affected": [
    {
      "affectedData": [
        {
          "product": "cms",
          "vendor": "craftcms",
          "versions": [
            {
              "status": "affected",
              "version": "\u003e= 5.0.0-RC1, \u003c 5.4.6"
            },
            {
              "status": "affected",
              "version": "\u003e= 4.0.0-RC1, \u003c 4.12.5"
            }
          ]
        }
      ],
      "source": "security-advisories@github.com"
    },
    {
      "affectedData": [
        {
          "cpes": [
            "cpe:2.3:a:craftcms:craft_cms:*:*:*:*:*:*:*:*"
          ],
          "defaultStatus": "unknown",
          "product": "craft_cms",
          "vendor": "craftcms",
          "versions": [
            {
              "lessThanOrEqual": "5.0.0-RC1",
              "status": "affected",
              "version": "0",
              "versionType": "custom"
            },
            {
              "lessThan": "5.4.6",
              "status": "affected",
              "version": "0",
              "versionType": "custom"
            },
            {
              "lessThanOrEqual": "4.0.0-RC1",
              "status": "affected",
              "version": "0",
              "versionType": "custom"
            },
            {
              "lessThan": "4.12.5",
              "status": "affected",
              "version": "0",
              "versionType": "custom"
            }
          ]
        }
      ],
      "source": "134c704f-9b21-4f2e-91b3-4a467353bcc0"
    }
  ],
  "configurations": [
    {
      "nodes": [
        {
          "cpeMatch": [
            {
              "criteria": "cpe:2.3:a:craftcms:craft_cms:*:*:*:*:*:*:*:*",
              "matchCriteriaId": "D75081F6-DA85-4F2D-B57B-5F4E8864B8F8",
              "versionEndExcluding": "4.12.5",
              "versionStartExcluding": "4.0.0",
              "vulnerable": true
            },
            {
              "criteria": "cpe:2.3:a:craftcms:craft_cms:*:*:*:*:*:*:*:*",
              "matchCriteriaId": "E8C229F2-C3B1-4715-97FD-53AD88FB124F",
              "versionEndExcluding": "5.4.6",
              "versionStartExcluding": "5.0.0",
              "vulnerable": true
            },
            {
              "criteria": "cpe:2.3:a:craftcms:craft_cms:4.0.0:rc1:*:*:*:*:*:*",
              "matchCriteriaId": "CC2F40FC-7C27-456A-B16D-679410D1D5CF",
              "vulnerable": true
            },
            {
              "criteria": "cpe:2.3:a:craftcms:craft_cms:4.0.0:rc2:*:*:*:*:*:*",
              "matchCriteriaId": "FBAA8227-04F8-404C-907B-B0162B325F5A",
              "vulnerable": true
            },
            {
              "criteria": "cpe:2.3:a:craftcms:craft_cms:4.0.0:rc3:*:*:*:*:*:*",
              "matchCriteriaId": "21B28E2C-327A-4CE6-ACAD-97E459712A55",
              "vulnerable": true
            },
            {
              "criteria": "cpe:2.3:a:craftcms:craft_cms:5.0.0:rc1:*:*:*:*:*:*",
              "matchCriteriaId": "8D8E02D1-601A-4E2B-B619-4775BFDB72D0",
              "vulnerable": true
            }
          ],
          "negate": false,
          "operator": "OR"
        }
      ]
    }
  ],
  "cveTags": [],
  "descriptions": [
    {
      "lang": "en",
      "value": "Craft is a content management system (CMS). A vulnerability in CraftCMS allows an attacker to bypass local file system validation by utilizing a double file:// scheme (e.g., file://file:////). This enables the attacker to specify sensitive folders as the file system, leading to potential file overwriting through malicious uploads, unauthorized access to sensitive files, and, under certain conditions, remote code execution (RCE) via Server-Side Template Injection (SSTI) payloads. Note that this will only work if you have an authenticated administrator account with allowAdminChanges enabled. This is fixed in 5.4.6 and 4.12.5."
    },
    {
      "lang": "es",
      "value": "Craft es un sistema de gesti\u00f3n de contenido (CMS). Una vulnerabilidad en CraftCMS permite a un atacante eludir la validaci\u00f3n del sistema de archivos local mediante un esquema file:// doble (por ejemplo, file://file:////). Esto permite al atacante especificar carpetas confidenciales como sistema de archivos, lo que lleva a una posible sobrescritura de archivos mediante cargas maliciosas, acceso no autorizado a archivos confidenciales y, en determinadas condiciones, ejecuci\u00f3n remota de c\u00f3digo (RCE) mediante payloads de Server-Side Template Injection (SSTI). Tenga en cuenta que esto solo funcionar\u00e1 si tiene una cuenta de administrador autenticada con allowAdminChanges habilitado. Esto se solucion\u00f3 en 5.4.6 y 4.12.5."
    }
  ],
  "id": "CVE-2024-52291",
  "lastModified": "2026-06-17T08:06:57.110",
  "metrics": {
    "cvssMetricV31": [
      {
        "cvssData": {
          "attackComplexity": "LOW",
          "attackVector": "NETWORK",
          "availabilityImpact": "HIGH",
          "baseScore": 8.4,
          "baseSeverity": "HIGH",
          "confidentialityImpact": "HIGH",
          "integrityImpact": "HIGH",
          "privilegesRequired": "HIGH",
          "scope": "CHANGED",
          "userInteraction": "REQUIRED",
          "vectorString": "CVSS:3.1/AV:N/AC:L/PR:H/UI:R/S:C/C:H/I:H/A:H",
          "version": "3.1"
        },
        "exploitabilityScore": 1.7,
        "impactScore": 6.0,
        "source": "security-advisories@github.com",
        "type": "Secondary"
      },
      {
        "cvssData": {
          "attackComplexity": "LOW",
          "attackVector": "NETWORK",
          "availabilityImpact": "HIGH",
          "baseScore": 7.2,
          "baseSeverity": "HIGH",
          "confidentialityImpact": "HIGH",
          "integrityImpact": "HIGH",
          "privilegesRequired": "HIGH",
          "scope": "UNCHANGED",
          "userInteraction": "NONE",
          "vectorString": "CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H",
          "version": "3.1"
        },
        "exploitabilityScore": 1.2,
        "impactScore": 5.9,
        "source": "nvd@nist.gov",
        "type": "Primary"
      }
    ],
    "ssvcV203": [
      {
        "source": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
        "ssvcData": {
          "id": "CVE-2024-52291",
          "options": [
            {
              "exploitation": "poc"
            },
            {
              "automatable": "no"
            },
            {
              "technicalImpact": "total"
            }
          ],
          "role": "CISA Coordinator",
          "timestamp": "2024-11-13T18:50:50.793331Z",
          "version": "2.0.3"
        }
      }
    ]
  },
  "published": "2024-11-13T17:15:12.087",
  "references": [
    {
      "source": "security-advisories@github.com",
      "tags": [
        "Exploit",
        "Vendor Advisory"
      ],
      "url": "https://github.com/craftcms/cms/security/advisories/GHSA-jrh5-vhr9-qh7q"
    }
  ],
  "sourceIdentifier": "security-advisories@github.com",
  "vulnStatus": "Analyzed",
  "weaknesses": [
    {
      "description": [
        {
          "lang": "en",
          "value": "CWE-22"
        }
      ],
      "source": "security-advisories@github.com",
      "type": "Secondary"
    }
  ]
}
GHSA-JRH5-VHR9-QH7Q
Vulnerability from github – Published: 2024-11-13 14:12 – Updated: 2024-11-13 18:58Summary
A vulnerability in CraftCMS allows an attacker to bypass local file system validation by utilizing a double file:// scheme (e.g., file://file:////). This enables the attacker to specify sensitive folders as the file system, leading to potential file overwriting through malicious uploads, unauthorized access to sensitive files, and, under certain conditions, remote code execution (RCE) via Server-Side Template Injection (SSTI) payloads.
Note that this will only work if you have an authenticated administrator account with allowAdminChanges enabled.
https://craftcms.com/knowledge-base/securing-craft#set-allowAdminChanges-to-false-in-production
Details
The issue lies in line 57 of cms/src/helpers/FileHelper.php, it only removes file:// on the most left. It is trivial to bypass this sanitization by adding 2 file://, e.g. file://file:////.
    public static function normalizePath($path, $ds = DIRECTORY_SEPARATOR): string
    {
        // Remove any file protocol wrappers
        $path = StringHelper::removeLeft($path, 'file://');

        // Is this a UNC network share path?
        $isUnc = (str_starts_with($path, '//') || str_starts_with($path, '\\\\'));

        // Normalize the path
        $path = parent::normalizePath($path, $ds);

        // If it is UNC, add those slashes back in front
        if ($isUnc) {
            $path = $ds . $ds . ltrim($path, $ds);
        }

        return $path;
    }
PoC
- Sign in with an admin account and navigate to
Settings → Assets, then create a new volume. - n the Asset Filesystem section, create a new file system and set the Base Path to
file://file:////vendor. Without the prefix, the selection fails.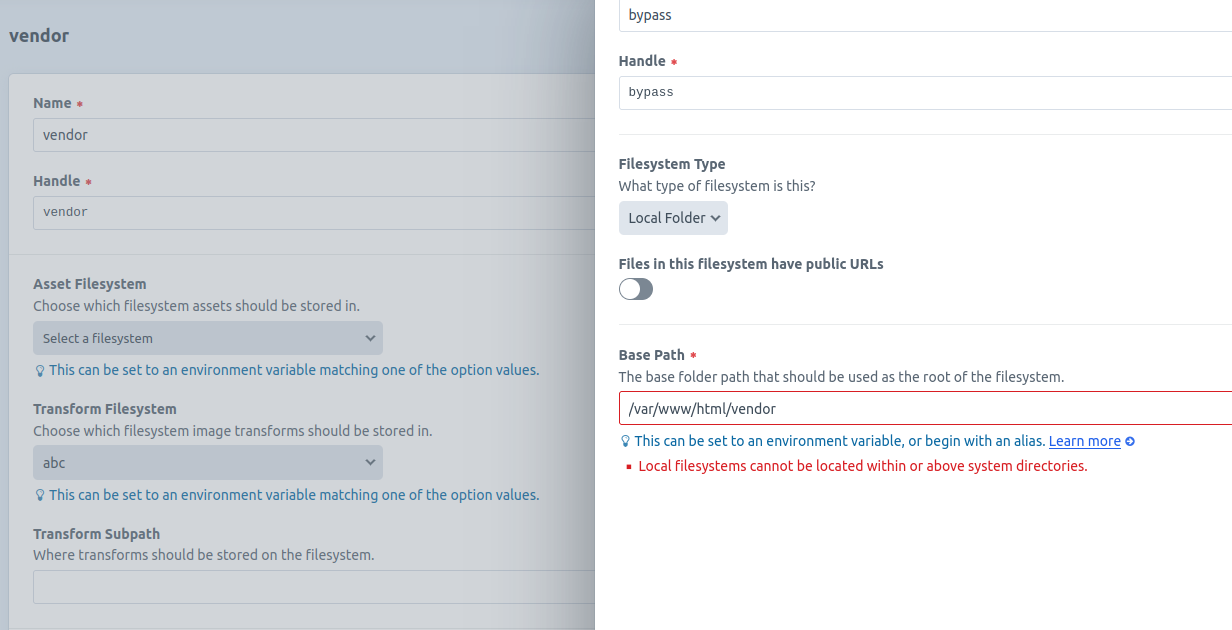 With the double
file://prefix, the selection succeeds.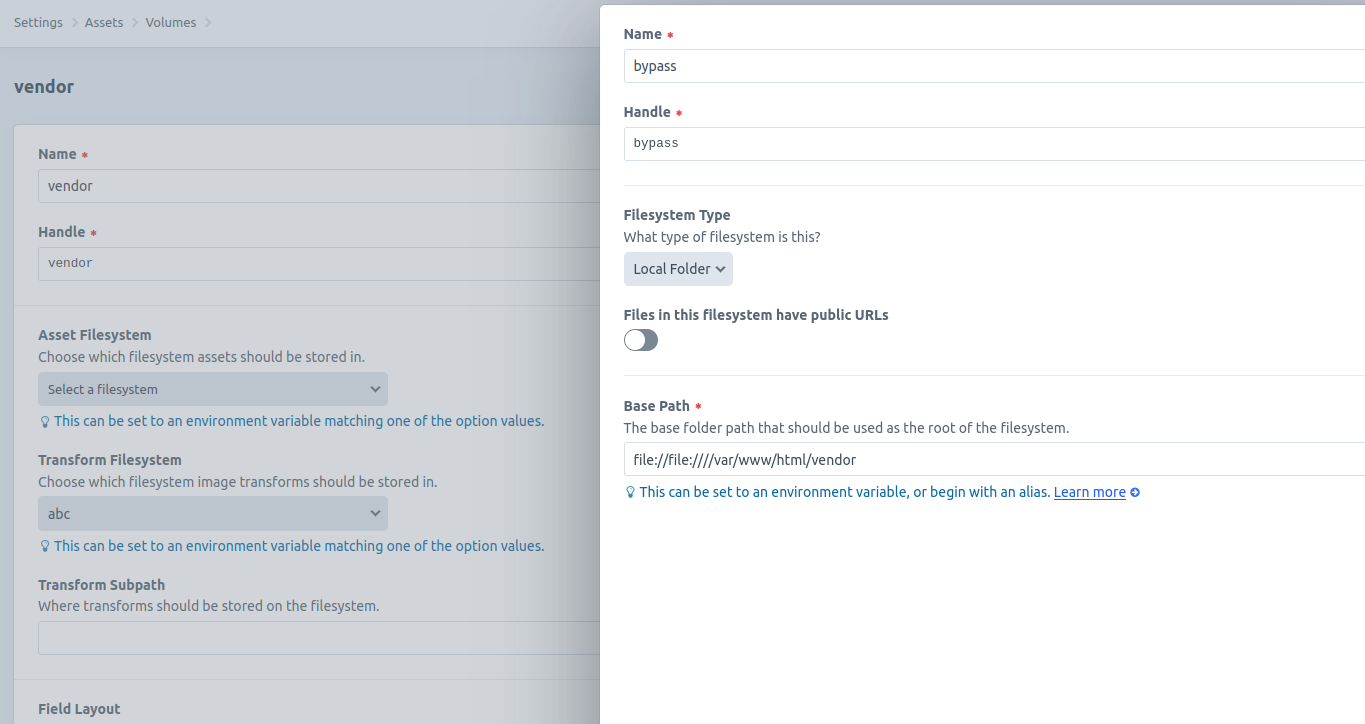
- Access Assets from the left navigation bar, then upload a file into this volume.
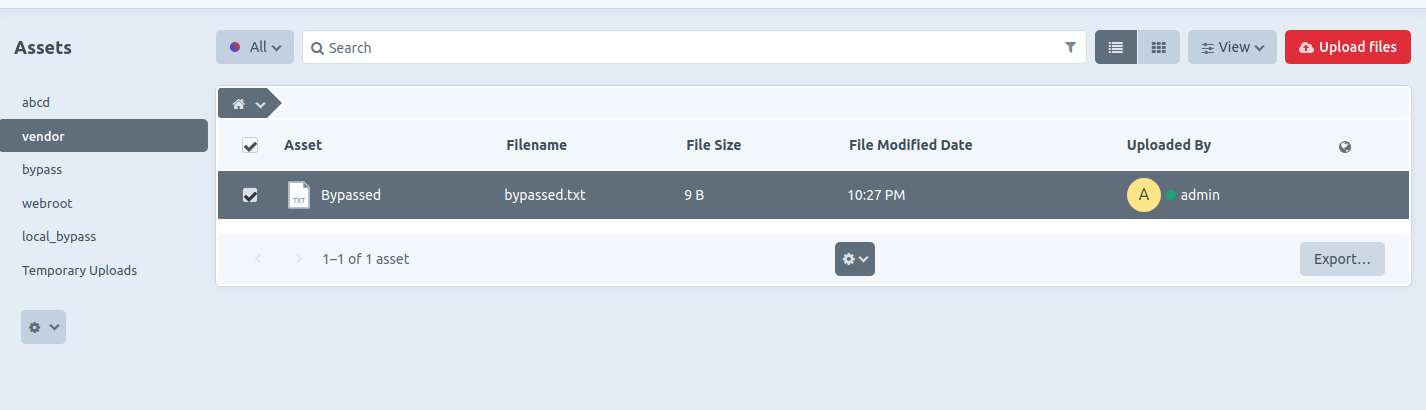
- The file is successfully uploaded and stored in the sensitive folder specified (e.g.,
/vendor).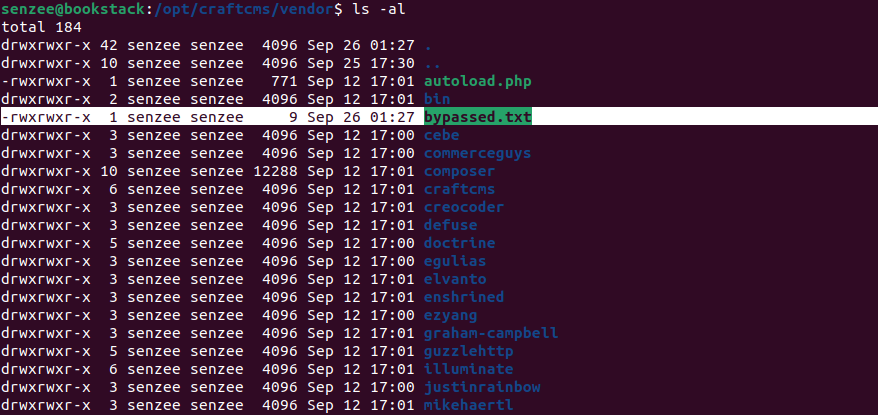
- SSTI payloads can be uploaded to
/templatesfolder, though full code execution was not achieved during testing, some payloads were still successful, leading to sensitive information disclosure, among other potential impacts.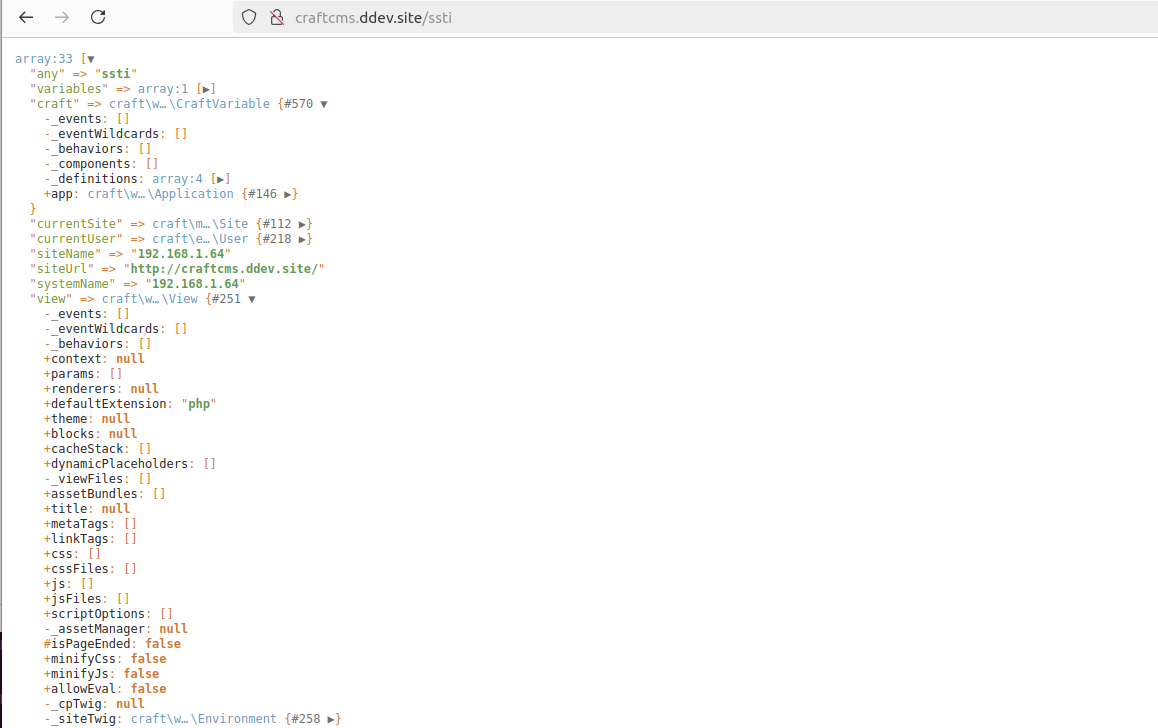
Impact
Attackers who compromise an admin account(The admin user is not equal to the server owner) can exploit this flaw to assign sensitive folders as the base path of the filesystem. For instance, if the path /templates is specified (e.g., file://file:////var/www/html/templates), the attacker could upload SSTI payloads. While CraftCMS includes strict SSTI input sanitization, RCE may still be possible if the attacker can craft a valid payload, as seen in similar vulnerabilities (e.g., GHSA-44wr-rmwq-3phw).
Additionally, attackers can upload tampered files to overwrite critical web application files. By enabling public URLs for files in the specified filesystem, they can also retrieve sensitive files (e.g., configuration files from the local file system).
Although the vulnerability is exploitable only in the authenticated users, configuration with ALLOW_ADMIN_CHANGES=true, there is still a potential security threat.
{
"affected": [
{
"database_specific": {
"last_known_affected_version_range": "\u003c= 5.4.5.1"
},
"package": {
"ecosystem": "Packagist",
"name": "craftcms/cms"
},
"ranges": [
{
"events": [
{
"introduced": "5.0.0-RC1"
},
{
"fixed": "5.4.6"
}
],
"type": "ECOSYSTEM"
}
]
},
{
"database_specific": {
"last_known_affected_version_range": "\u003c= 4.12.4.1"
},
"package": {
"ecosystem": "Packagist",
"name": "craftcms/cms"
},
"ranges": [
{
"events": [
{
"introduced": "4.0.0-RC1"
},
{
"fixed": "4.12.5"
}
],
"type": "ECOSYSTEM"
}
]
}
],
"aliases": [
"CVE-2024-52291"
],
"database_specific": {
"cwe_ids": [
"CWE-22"
],
"github_reviewed": true,
"github_reviewed_at": "2024-11-13T14:12:36Z",
"nvd_published_at": "2024-11-13T17:15:12Z",
"severity": "HIGH"
},
"details": "### Summary\nA vulnerability in CraftCMS allows an attacker to bypass local file system validation by utilizing a double `file://` scheme (e.g., `file://file:////`). This enables the attacker to specify sensitive folders as the file system, leading to potential file overwriting through malicious uploads, unauthorized access to sensitive files, and, under certain conditions, remote code execution (RCE) via Server-Side Template Injection (SSTI) payloads.\n\nNote that this will only work if you have an authenticated administrator account with [allowAdminChanges enabled](https://craftcms.com/docs/5.x/reference/config/general.html#allowadminchanges).\n\nhttps://craftcms.com/knowledge-base/securing-craft#set-allowAdminChanges-to-false-in-production\n\n### Details\nThe issue lies in line 57 of `cms/src/helpers/FileHelper.php`, it only removes `file://` on the most left. It is trivial to bypass this sanitization by adding 2 `file://`, e.g. `file://file:////`.\n```php\n public static function normalizePath($path, $ds = DIRECTORY_SEPARATOR): string\n {\n // Remove any file protocol wrappers\n $path = StringHelper::removeLeft($path, \u0027file://\u0027);\n\n // Is this a UNC network share path?\n $isUnc = (str_starts_with($path, \u0027//\u0027) || str_starts_with($path, \u0027\\\\\\\\\u0027));\n\n // Normalize the path\n $path = parent::normalizePath($path, $ds);\n\n // If it is UNC, add those slashes back in front\n if ($isUnc) {\n $path = $ds . $ds . ltrim($path, $ds);\n }\n\n return $path;\n }\n```\n\n### PoC\n1. Sign in with an admin account and navigate to `Settings \u2192 Assets`, then create a new volume.\n2. n the Asset Filesystem section, create a new file system and set the Base Path to `file://file:////vendor`.\nWithout the prefix, the selection fails.\n \nWith the double `file://` prefix, the selection succeeds.\n \n3. Access Assets from the left navigation bar, then upload a file into this volume.\n \n4. The file is successfully uploaded and stored in the sensitive folder specified (e.g., `/vendor`).\n \n5. SSTI payloads can be uploaded to `/templates` folder, though full code execution was not achieved during testing, some payloads were still successful, leading to sensitive information disclosure, among other potential impacts.\n \n\n### Impact\nAttackers who compromise an admin account(The admin user is not equal to the server owner) can exploit this flaw to assign sensitive folders as the base path of the filesystem. For instance, if the path `/templates` is specified (e.g., `file://file:////var/www/html/templates`), the attacker could upload SSTI payloads. While CraftCMS includes strict SSTI input sanitization, RCE may still be possible if the attacker can craft a valid payload, as seen in similar vulnerabilities (e.g., [GHSA-44wr-rmwq-3phw](https://github.com/advisories/GHSA-44wr-rmwq-3phw)).\n\nAdditionally, attackers can upload tampered files to overwrite critical web application files. By enabling public URLs for files in the specified filesystem, they can also retrieve sensitive files (e.g., configuration files from the local file system).\n\nAlthough the vulnerability is exploitable only in the authenticated users, configuration with `ALLOW_ADMIN_CHANGES=true`, there is still a potential security threat.\n\n",
"id": "GHSA-jrh5-vhr9-qh7q",
"modified": "2024-11-13T18:58:32Z",
"published": "2024-11-13T14:12:36Z",
"references": [
{
"type": "WEB",
"url": "https://github.com/craftcms/cms/security/advisories/GHSA-jrh5-vhr9-qh7q"
},
{
"type": "ADVISORY",
"url": "https://nvd.nist.gov/vuln/detail/CVE-2024-52291"
},
{
"type": "PACKAGE",
"url": "https://github.com/craftcms/cms"
}
],
"schema_version": "1.4.0",
"severity": [
{
"score": "CVSS:3.1/AV:N/AC:L/PR:H/UI:R/S:C/C:H/I:H/A:H",
"type": "CVSS_V3"
},
{
"score": "CVSS:4.0/AV:N/AC:L/AT:P/PR:H/UI:A/VC:H/VI:H/VA:H/SC:H/SI:H/SA:H/E:P",
"type": "CVSS_V4"
}
],
"summary": "Local File System Validation Bypass Leading to File Overwrite, Sensitive File Access, and Potential Code Execution"
}
Drag nodes to arrange them. Double-click a related vulnerability to open it, or a source to visit its link. The Physics button on the left tunes the layout and the simulation; the legend at the bottom left hides or shows nodes by kind and by sighting type.
Sightings
| Author | Source | Type | Date | Other |
|---|
Nomenclature
- Seen: The vulnerability was mentioned, discussed, or observed by the user.
- Confirmed: The vulnerability has been validated from an analyst's perspective.
- Published Proof of Concept: A public proof of concept is available for this vulnerability.
- Exploited: The vulnerability was observed as exploited by the user who reported the sighting.
- Patched: The vulnerability was observed as successfully patched by the user who reported the sighting.
- Not exploited: The vulnerability was not observed as exploited by the user who reported the sighting.
- Not confirmed: The user expressed doubt about the validity of the vulnerability.
- Not patched: The vulnerability was not observed as successfully patched by the user who reported the sighting.
Vulnerability timeline
Sightings and recorded dates, grouped by day · UTC
How durations are calculated
Following the VTEM framework (Black Hat USA 2015), time to patch starts when the vendor or a coordinator was informed, total time to patch at discovery, and disclosure to patch at public disclosure; vendor response time runs from the report to its acknowledgement. Time to exploit and time unpatched start at the earliest discovery or report, falling back to public disclosure. Unpatched time ends at the first recorded patch, or the calculation time when no patch is recorded. Exploitation to patch shows the interval between those two events; a published proof of concept is a public exploit, not exploitation.
Each result shows its source dates. A negative interval means the end event came first; when date-only inputs leave the order open, the result says so. Date-only inputs are approximate. The earliest evidence wins: KEV report dates and sightings are labelled as such. Records describing another vulnerability are listed but never calculated from, and a PoC alone does not establish exploitation. Missing patch evidence does not prove that no patch exists. Filters below change the event list only.
Loading timeline…

The approach is described in our paper Mapping CVEs to MITRE ATT&CK Techniques: A Curated Gold-Set Classifier and the Limits of LLM-Assisted Label Expansion.
Browse all ATT&CK techniques and the vulnerabilities related to each.
Related by attack behaviour
Vulnerabilities whose description is nearest to this one in the vector space of the CIRCL/vulnerability-attack-technique-biencoder model. This is a similarity search over the bi-encoder space (plain cosine), not a classification, and it has no measured accuracy.