GHSA-CWX6-CX7X-4Q34
Vulnerability from github – Published: 2024-04-22 18:37 – Updated: 2024-04-23 14:15Summary
SQL injection vulnerability in POST /search/search=packages in LibreNMS 24.3.0 allows a user with global read privileges to execute SQL commands via the package parameter.
Details
There is a lack of hygiene of data coming from the user in line 83 of the file librenms/includes/html/pages/search/packages.inc.php
PoC
https://doc.clickup.com/9013166444/p/h/8ckm0bc-53/16811991bb5fff6
Impact
With this vulnerability, we can exploit a SQL injection time based vulnerability to extract all data from the database, such as administrator credentials
{
"affected": [
{
"package": {
"ecosystem": "Packagist",
"name": "librenms/librenms"
},
"ranges": [
{
"events": [
{
"introduced": "0"
},
{
"fixed": "24.4.0"
}
],
"type": "ECOSYSTEM"
}
]
}
],
"aliases": [
"CVE-2024-32461"
],
"database_specific": {
"cwe_ids": [
"CWE-89"
],
"github_reviewed": true,
"github_reviewed_at": "2024-04-22T18:37:21Z",
"nvd_published_at": "2024-04-22T22:15:07Z",
"severity": "HIGH"
},
"details": "### Summary\nSQL injection vulnerability in POST /search/search=packages in LibreNMS 24.3.0 allows a user with global read privileges to execute SQL commands via the package parameter. \n\n### Details\nThere is a lack of hygiene of data coming from the user in line 83 of the file librenms/includes/html/pages/search/packages.inc.php\n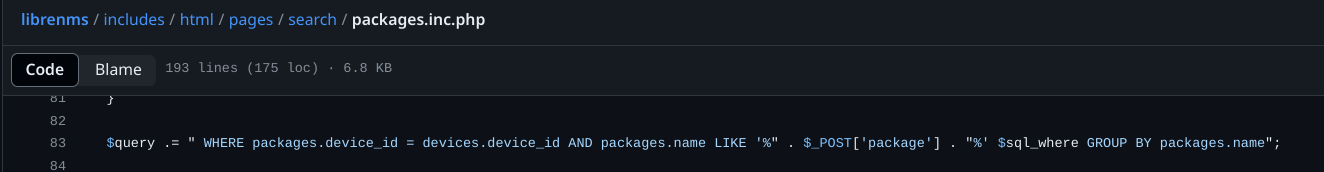\n\n### PoC\nhttps://doc.clickup.com/9013166444/p/h/8ckm0bc-53/16811991bb5fff6\n\n### Impact\nWith this vulnerability, we can exploit a SQL injection time based vulnerability to extract all data from the database, such as administrator credentials\n",
"id": "GHSA-cwx6-cx7x-4q34",
"modified": "2024-04-23T14:15:04Z",
"published": "2024-04-22T18:37:21Z",
"references": [
{
"type": "WEB",
"url": "https://github.com/librenms/librenms/security/advisories/GHSA-cwx6-cx7x-4q34"
},
{
"type": "ADVISORY",
"url": "https://nvd.nist.gov/vuln/detail/CVE-2024-32461"
},
{
"type": "WEB",
"url": "https://github.com/librenms/librenms/commit/d29201fce134347f891102699fbde7070debee33"
},
{
"type": "WEB",
"url": "https://doc.clickup.com/9013166444/p/h/8ckm0bc-53/16811991bb5fff6"
},
{
"type": "PACKAGE",
"url": "https://github.com/librenms/librenms"
}
],
"schema_version": "1.4.0",
"severity": [
{
"score": "CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H",
"type": "CVSS_V3"
}
],
"summary": "LibreNMS vulnerable to SQL injection time-based leads to database extraction"
}
Sightings
| Author | Source | Type | Date | Other |
|---|
Nomenclature
- Seen: The vulnerability was mentioned, discussed, or observed by the user.
- Confirmed: The vulnerability has been validated from an analyst's perspective.
- Published Proof of Concept: A public proof of concept is available for this vulnerability.
- Exploited: The vulnerability was observed as exploited by the user who reported the sighting.
- Patched: The vulnerability was observed as successfully patched by the user who reported the sighting.
- Not exploited: The vulnerability was not observed as exploited by the user who reported the sighting.
- Not confirmed: The user expressed doubt about the validity of the vulnerability.
- Not patched: The vulnerability was not observed as successfully patched by the user who reported the sighting.

The approach is described in our paper Mapping CVEs to MITRE ATT&CK Techniques: A Curated Gold-Set Classifier and the Limits of LLM-Assisted Label Expansion.
Browse all ATT&CK techniques and the vulnerabilities related to each.
Related by attack behaviour
Vulnerabilities whose description is nearest to this one in the vector space of the CIRCL/vulnerability-attack-technique-biencoder model. This is a similarity search over the bi-encoder space (plain cosine), not a classification, and it has no measured accuracy.