CVE-2024-32880 (GCVE-0-2024-32880)
Vulnerability from cvelistv5 – Published: 2024-04-26 17:30 – Updated: 2024-08-02 02:20- CWE-434 - Unrestricted Upload of File with Dangerous Type
| URL | Tags |
|---|---|
| https://github.com/pyload/pyload/security/advisor… | x_refsource_CONFIRM |
{
"containers": {
"adp": [
{
"affected": [
{
"cpes": [
"cpe:2.3:a:pyload:pyload:-:*:*:*:*:*:*:*"
],
"defaultStatus": "unknown",
"product": "pyload",
"vendor": "pyload",
"versions": [
{
"status": "affected",
"version": "*"
}
]
}
],
"metrics": [
{
"other": {
"content": {
"id": "CVE-2024-32880",
"options": [
{
"Exploitation": "none"
},
{
"Automatable": "no"
},
{
"Technical Impact": "total"
}
],
"role": "CISA Coordinator",
"timestamp": "2024-04-26T18:47:38.741143Z",
"version": "2.0.3"
},
"type": "ssvc"
}
}
],
"providerMetadata": {
"dateUpdated": "2024-06-04T17:51:11.607Z",
"orgId": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
"shortName": "CISA-ADP"
},
"title": "CISA ADP Vulnrichment"
},
{
"providerMetadata": {
"dateUpdated": "2024-08-02T02:20:35.649Z",
"orgId": "af854a3a-2127-422b-91ae-364da2661108",
"shortName": "CVE"
},
"references": [
{
"name": "https://github.com/pyload/pyload/security/advisories/GHSA-3f7w-p8vr-4v5f",
"tags": [
"x_refsource_CONFIRM",
"x_transferred"
],
"url": "https://github.com/pyload/pyload/security/advisories/GHSA-3f7w-p8vr-4v5f"
}
],
"title": "CVE Program Container"
}
],
"cna": {
"affected": [
{
"product": "pyload",
"vendor": "pyload",
"versions": [
{
"status": "affected",
"version": "\u003c= 4.2.0"
}
]
}
],
"descriptions": [
{
"lang": "en",
"value": "pyload is an open-source Download Manager written in pure Python. An authenticated user can change the download folder and upload a crafted template to the specified folder lead to remote code execution. There is no fix available at the time of publication."
}
],
"metrics": [
{
"cvssV3_1": {
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "HIGH",
"baseScore": 9.1,
"baseSeverity": "CRITICAL",
"confidentialityImpact": "HIGH",
"integrityImpact": "HIGH",
"privilegesRequired": "HIGH",
"scope": "CHANGED",
"userInteraction": "NONE",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:C/C:H/I:H/A:H",
"version": "3.1"
}
}
],
"problemTypes": [
{
"descriptions": [
{
"cweId": "CWE-434",
"description": "CWE-434: Unrestricted Upload of File with Dangerous Type",
"lang": "en",
"type": "CWE"
}
]
}
],
"providerMetadata": {
"dateUpdated": "2024-04-26T17:30:24.685Z",
"orgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
"shortName": "GitHub_M"
},
"references": [
{
"name": "https://github.com/pyload/pyload/security/advisories/GHSA-3f7w-p8vr-4v5f",
"tags": [
"x_refsource_CONFIRM"
],
"url": "https://github.com/pyload/pyload/security/advisories/GHSA-3f7w-p8vr-4v5f"
}
],
"source": {
"advisory": "GHSA-3f7w-p8vr-4v5f",
"discovery": "UNKNOWN"
},
"title": "pyLoad allows upload to arbitrary folder lead to RCE"
}
},
"cveMetadata": {
"assignerOrgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
"assignerShortName": "GitHub_M",
"cveId": "CVE-2024-32880",
"datePublished": "2024-04-26T17:30:24.685Z",
"dateReserved": "2024-04-19T14:07:11.230Z",
"dateUpdated": "2024-08-02T02:20:35.649Z",
"state": "PUBLISHED"
},
"dataType": "CVE_RECORD",
"dataVersion": "5.1",
"vulnerability-lookup:meta": {
"epss": {
"cve": "CVE-2024-32880",
"date": "2026-09-28",
"epss": "0.01354",
"percentile": "0.7049"
},
"nvd": {
"cve": {
"affected": [
{
"affectedData": [
{
"product": "pyload",
"vendor": "pyload",
"versions": [
{
"status": "affected",
"version": "\u003c= 4.2.0"
}
]
}
],
"source": "security-advisories@github.com"
},
{
"affectedData": [
{
"cpes": [
"cpe:2.3:a:pyload:pyload:-:*:*:*:*:*:*:*"
],
"defaultStatus": "unknown",
"product": "pyload",
"vendor": "pyload",
"versions": [
{
"status": "affected",
"version": "*"
}
]
}
],
"source": "134c704f-9b21-4f2e-91b3-4a467353bcc0"
}
],
"configurations": [
{
"nodes": [
{
"cpeMatch": [
{
"criteria": "cpe:2.3:a:pyload:pyload:*:*:*:*:*:*:*:*",
"matchCriteriaId": "9347973D-3989-4969-8721-8A55ABBE2F6E",
"versionEndIncluding": "0.5.0",
"vulnerable": true
}
],
"negate": false,
"operator": "OR"
}
]
}
],
"cveTags": [],
"descriptions": [
{
"lang": "en",
"value": "pyload is an open-source Download Manager written in pure Python. An authenticated user can change the download folder and upload a crafted template to the specified folder lead to remote code execution. There is no fix available at the time of publication."
},
{
"lang": "es",
"value": "pyload es un administrador de descargas de c\u00f3digo abierto escrito en Python puro. Un usuario autenticado puede cambiar la carpeta de descarga y cargar una plantilla manipulada en la carpeta especificada, lo que lleva a la ejecuci\u00f3n remota del c\u00f3digo. No hay ninguna soluci\u00f3n disponible en el momento de la publicaci\u00f3n."
}
],
"id": "CVE-2024-32880",
"lastModified": "2026-06-17T07:30:36.520",
"metrics": {
"cvssMetricV31": [
{
"cvssData": {
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "HIGH",
"baseScore": 9.1,
"baseSeverity": "CRITICAL",
"confidentialityImpact": "HIGH",
"integrityImpact": "HIGH",
"privilegesRequired": "HIGH",
"scope": "CHANGED",
"userInteraction": "NONE",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:C/C:H/I:H/A:H",
"version": "3.1"
},
"exploitabilityScore": 2.3,
"impactScore": 6.0,
"source": "security-advisories@github.com",
"type": "Secondary"
},
{
"cvssData": {
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "HIGH",
"baseScore": 7.2,
"baseSeverity": "HIGH",
"confidentialityImpact": "HIGH",
"integrityImpact": "HIGH",
"privilegesRequired": "HIGH",
"scope": "UNCHANGED",
"userInteraction": "NONE",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H",
"version": "3.1"
},
"exploitabilityScore": 1.2,
"impactScore": 5.9,
"source": "nvd@nist.gov",
"type": "Primary"
}
],
"ssvcV203": [
{
"source": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
"ssvcData": {
"id": "CVE-2024-32880",
"options": [
{
"exploitation": "none"
},
{
"automatable": "no"
},
{
"technicalImpact": "total"
}
],
"role": "CISA Coordinator",
"timestamp": "2024-04-26T18:47:38.741143Z",
"version": "2.0.3"
}
}
]
},
"published": "2024-04-26T18:15:45.970",
"references": [
{
"source": "security-advisories@github.com",
"tags": [
"Exploit",
"Vendor Advisory"
],
"url": "https://github.com/pyload/pyload/security/advisories/GHSA-3f7w-p8vr-4v5f"
},
{
"source": "af854a3a-2127-422b-91ae-364da2661108",
"tags": [
"Exploit",
"Vendor Advisory"
],
"url": "https://github.com/pyload/pyload/security/advisories/GHSA-3f7w-p8vr-4v5f"
}
],
"sourceIdentifier": "security-advisories@github.com",
"vulnStatus": "Analyzed",
"weaknesses": [
{
"description": [
{
"lang": "en",
"value": "CWE-434"
}
],
"source": "security-advisories@github.com",
"type": "Secondary"
}
]
}
},
"redhat_vex": {
"current_release_date": "2025-05-28T21:18:42+00:00",
"cve": "CVE-2024-32880",
"id": "CVE-2024-32880",
"initial_release_date": "2024-01-01T00:00:00+00:00",
"product_status:known_not_affected": "1",
"source": "Red Hat CSAF VEX",
"status": "final",
"title": "pyLoad allows upload to arbitrary folder lead to RCE",
"url": "https://security.access.redhat.com/data/csaf/v2/vex/2024/cve-2024-32880.json",
"version": "3"
},
"vulnrichment": {
"containers": {
"adp": [
{
"affected": [
{
"cpes": [
"cpe:2.3:a:pyload:pyload:-:*:*:*:*:*:*:*"
],
"defaultStatus": "unknown",
"product": "pyload",
"vendor": "pyload",
"versions": [
{
"status": "affected",
"version": "*"
}
]
}
],
"metrics": [
{
"other": {
"content": {
"id": "CVE-2024-32880",
"options": [
{
"Exploitation": "none"
},
{
"Automatable": "no"
},
{
"Technical Impact": "total"
}
],
"role": "CISA Coordinator",
"timestamp": "2024-04-26T18:47:38.741143Z",
"version": "2.0.3"
},
"type": "ssvc"
}
}
],
"providerMetadata": {
"dateUpdated": "2024-04-26T18:45:47.257Z",
"orgId": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
"shortName": "CISA-ADP"
},
"title": "CISA ADP Vulnrichment"
}
],
"cna": {
"affected": [
{
"product": "pyload",
"vendor": "pyload",
"versions": [
{
"status": "affected",
"version": "\u003c= 4.2.0"
}
]
}
],
"descriptions": [
{
"lang": "en",
"value": "pyload is an open-source Download Manager written in pure Python. An authenticated user can change the download folder and upload a crafted template to the specified folder lead to remote code execution. There is no fix available at the time of publication."
}
],
"metrics": [
{
"cvssV3_1": {
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "HIGH",
"baseScore": 9.1,
"baseSeverity": "CRITICAL",
"confidentialityImpact": "HIGH",
"integrityImpact": "HIGH",
"privilegesRequired": "HIGH",
"scope": "CHANGED",
"userInteraction": "NONE",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:C/C:H/I:H/A:H",
"version": "3.1"
}
}
],
"problemTypes": [
{
"descriptions": [
{
"cweId": "CWE-434",
"description": "CWE-434: Unrestricted Upload of File with Dangerous Type",
"lang": "en",
"type": "CWE"
}
]
}
],
"providerMetadata": {
"dateUpdated": "2024-04-26T17:30:24.685Z",
"orgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
"shortName": "GitHub_M"
},
"references": [
{
"name": "https://github.com/pyload/pyload/security/advisories/GHSA-3f7w-p8vr-4v5f",
"tags": [
"x_refsource_CONFIRM"
],
"url": "https://github.com/pyload/pyload/security/advisories/GHSA-3f7w-p8vr-4v5f"
}
],
"source": {
"advisory": "GHSA-3f7w-p8vr-4v5f",
"discovery": "UNKNOWN"
},
"title": "pyLoad allows upload to arbitrary folder lead to RCE"
}
},
"cveMetadata": {
"assignerOrgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
"assignerShortName": "GitHub_M",
"cveId": "CVE-2024-32880",
"datePublished": "2024-04-26T17:30:24.685Z",
"dateReserved": "2024-04-19T14:07:11.230Z",
"dateUpdated": "2024-06-04T17:51:11.607Z",
"state": "PUBLISHED"
},
"dataType": "CVE_RECORD",
"dataVersion": "5.1"
}
}
}
FKIE_CVE-2024-32880
Vulnerability from fkie_nvd - Published: 2024-04-26 18:15 - Updated: 2026-06-17 07:307.2 (High) - CVSS:3.1/
| URL | Tags | ||
|---|---|---|---|
| security-advisories@github.com | https://github.com/pyload/pyload/security/advisories/GHSA-3f7w-p8vr-4v5f | Exploit, Vendor Advisory | |
| af854a3a-2127-422b-91ae-364da2661108 | https://github.com/pyload/pyload/security/advisories/GHSA-3f7w-p8vr-4v5f | Exploit, Vendor Advisory |
{
  "affected": [
    {
      "affectedData": [
        {
          "product": "pyload",
          "vendor": "pyload",
          "versions": [
            {
              "status": "affected",
              "version": "\u003c= 4.2.0"
            }
          ]
        }
      ],
      "source": "security-advisories@github.com"
    },
    {
      "affectedData": [
        {
          "cpes": [
            "cpe:2.3:a:pyload:pyload:-:*:*:*:*:*:*:*"
          ],
          "defaultStatus": "unknown",
          "product": "pyload",
          "vendor": "pyload",
          "versions": [
            {
              "status": "affected",
              "version": "*"
            }
          ]
        }
      ],
      "source": "134c704f-9b21-4f2e-91b3-4a467353bcc0"
    }
  ],
  "configurations": [
    {
      "nodes": [
        {
          "cpeMatch": [
            {
              "criteria": "cpe:2.3:a:pyload:pyload:*:*:*:*:*:*:*:*",
              "matchCriteriaId": "9347973D-3989-4969-8721-8A55ABBE2F6E",
              "versionEndIncluding": "0.5.0",
              "vulnerable": true
            }
          ],
          "negate": false,
          "operator": "OR"
        }
      ]
    }
  ],
  "cveTags": [],
  "descriptions": [
    {
      "lang": "en",
      "value": "pyload is an open-source Download Manager written in pure Python. An authenticated user can change the download folder and upload a crafted template to the specified folder lead to remote code execution. There is no fix available at the time of publication."
    },
    {
      "lang": "es",
      "value": "pyload es un administrador de descargas de c\u00f3digo abierto escrito en Python puro. Un usuario autenticado puede cambiar la carpeta de descarga y cargar una plantilla manipulada en la carpeta especificada, lo que lleva a la ejecuci\u00f3n remota del c\u00f3digo. No hay ninguna soluci\u00f3n disponible en el momento de la publicaci\u00f3n."
    }
  ],
  "id": "CVE-2024-32880",
  "lastModified": "2026-06-17T07:30:36.520",
  "metrics": {
    "cvssMetricV31": [
      {
        "cvssData": {
          "attackComplexity": "LOW",
          "attackVector": "NETWORK",
          "availabilityImpact": "HIGH",
          "baseScore": 9.1,
          "baseSeverity": "CRITICAL",
          "confidentialityImpact": "HIGH",
          "integrityImpact": "HIGH",
          "privilegesRequired": "HIGH",
          "scope": "CHANGED",
          "userInteraction": "NONE",
          "vectorString": "CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:C/C:H/I:H/A:H",
          "version": "3.1"
        },
        "exploitabilityScore": 2.3,
        "impactScore": 6.0,
        "source": "security-advisories@github.com",
        "type": "Secondary"
      },
      {
        "cvssData": {
          "attackComplexity": "LOW",
          "attackVector": "NETWORK",
          "availabilityImpact": "HIGH",
          "baseScore": 7.2,
          "baseSeverity": "HIGH",
          "confidentialityImpact": "HIGH",
          "integrityImpact": "HIGH",
          "privilegesRequired": "HIGH",
          "scope": "UNCHANGED",
          "userInteraction": "NONE",
          "vectorString": "CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H",
          "version": "3.1"
        },
        "exploitabilityScore": 1.2,
        "impactScore": 5.9,
        "source": "nvd@nist.gov",
        "type": "Primary"
      }
    ],
    "ssvcV203": [
      {
        "source": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
        "ssvcData": {
          "id": "CVE-2024-32880",
          "options": [
            {
              "exploitation": "none"
            },
            {
              "automatable": "no"
            },
            {
              "technicalImpact": "total"
            }
          ],
          "role": "CISA Coordinator",
          "timestamp": "2024-04-26T18:47:38.741143Z",
          "version": "2.0.3"
        }
      }
    ]
  },
  "published": "2024-04-26T18:15:45.970",
  "references": [
    {
      "source": "security-advisories@github.com",
      "tags": [
        "Exploit",
        "Vendor Advisory"
      ],
      "url": "https://github.com/pyload/pyload/security/advisories/GHSA-3f7w-p8vr-4v5f"
    },
    {
      "source": "af854a3a-2127-422b-91ae-364da2661108",
      "tags": [
        "Exploit",
        "Vendor Advisory"
      ],
      "url": "https://github.com/pyload/pyload/security/advisories/GHSA-3f7w-p8vr-4v5f"
    }
  ],
  "sourceIdentifier": "security-advisories@github.com",
  "vulnStatus": "Analyzed",
  "weaknesses": [
    {
      "description": [
        {
          "lang": "en",
          "value": "CWE-434"
        }
      ],
      "source": "security-advisories@github.com",
      "type": "Secondary"
    }
  ]
}
GHSA-3F7W-P8VR-4V5F
Vulnerability from github – Published: 2024-04-24 21:16 – Updated: 2024-04-26 18:51Summary
An authenticated user can change the download folder and upload a crafted template to the specified folder lead to remote code execution
Details
example version: 0.5 file:src/pyload/webui/app/blueprints/app_blueprint.py
@bp.route("/render/<path:filename>", endpoint="render")
def render(filename):
    mimetype = mimetypes.guess_type(filename)[0] or "text/html"
    data = render_template(filename)
    return flask.Response(data, mimetype=mimetype)
So, if we can control file in the path "pyload/webui/app/templates" in latest version and path in "module/web/media/js"(the difference is the older version0.4.20 only renders file with extension name ".js"), the render_template func will works like SSTI(server-side template injection) when render the evil file we control.
in /settings page and the choose option general/general, where we can change the download folder.
Also, we can find the pyLoad install folder in /info page
So, we can change the value of Download folder to the template path. Then through /json/add_package we can upload a crafted template file to RCE.
@bp.route("/json/add_package", methods=["POST"], endpoint="add_package")
# @apiver_check
@login_required("ADD")
def add_package():
    api = flask.current_app.config["PYLOAD_API"]

    package_name = flask.request.form.get("add_name", "New Package").strip()
    queue = int(flask.request.form["add_dest"])
    links = [l.strip() for l in flask.request.form["add_links"].splitlines()]
    pw = flask.request.form.get("add_password", "").strip("\n\r")

    try:
        file = flask.request.files["add_file"]

        if file.filename:
            if not package_name or package_name == "New Package":
                package_name = file.filename

            file_path = os.path.join(
                api.get_config_value("general", "storage_folder"), "tmp_" + file.filename
            )
            file.save(file_path)
            links.insert(0, file_path)

    except Exception:
        pass

    urls = [url for url in links if url.strip()]
    pack = api.add_package(package_name, urls, queue)
    if pw:
        data = {"password": pw}
        api.set_package_data(pack, data)

    return jsonify(True)
PoC
First login into the admin page, then visit the info page to get the path of pyload installation folder. Second, change the download folder to PYLOAD_INSTALL_DIR/ webui/app/templates/ Third, upload crafted template file through /json/add_package through parameter add_file the content of crafted template file and its filename is "341.html":
{{x.__init__.__globals__['__builtins__']['eval']("__import__('os').popen('whoami').read()")}}
Last, visit http://TARGET/render/tmp_341.html to trigger the RCE
Impact
It is a RCE vulnerability and I think it affects all versions. In earlier version 0.4.20, the trigger difference is the pyload installation folder path difference and the upload file must with extension ".js" . The render js code in version 0.4.20:
@route("/media/js/<path:re:.+\.js>")
def js_dynamic(path):
    response.headers['Expires'] = time.strftime("%a, %d %b %Y %H:%M:%S GMT",
                                                time.gmtime(time.time() + 60 * 60 * 24 * 2))
    response.headers['Cache-control'] = "public"
    response.headers['Content-Type'] = "text/javascript; charset=UTF-8"

    try:
        # static files are not rendered
        if "static" not in path and "mootools" not in path:
            t = env.get_template("js/%s" % path)
            return t.render()
        else:
            return static_file(path, root=join(PROJECT_DIR, "media", "js"))
    except:
        return HTTPError(404, "Not Found")
{
"affected": [
{
"package": {
"ecosystem": "PyPI",
"name": "pyload-ng"
},
"ranges": [
{
"events": [
{
"introduced": "0"
},
{
"last_affected": "0.5.0"
}
],
"type": "ECOSYSTEM"
}
]
}
],
"aliases": [
"CVE-2024-32880"
],
"database_specific": {
"cwe_ids": [
"CWE-434"
],
"github_reviewed": true,
"github_reviewed_at": "2024-04-24T21:16:59Z",
"nvd_published_at": "2024-04-26T18:15:45Z",
"severity": "CRITICAL"
},
"details": "### Summary\nAn authenticated user can change the download folder and upload a crafted template to the specified folder lead to remote code execution\n\n### Details\nexample version: 0.5\nfile:src/pyload/webui/app/blueprints/app_blueprint.py\n```python\n@bp.route(\"/render/\u003cpath:filename\u003e\", endpoint=\"render\")\ndef render(filename):\n mimetype = mimetypes.guess_type(filename)[0] or \"text/html\"\n data = render_template(filename)\n return flask.Response(data, mimetype=mimetype)\n```\nSo, if we can control file in the path \"pyload/webui/app/templates\" in latest version and path in \"module/web/media/js\"(the difference is the older version0.4.20 only renders file with extension name \".js\"), the render_template func will works like SSTI(server-side template injection) when render the evil file we control.\n\nin /settings page and the choose option general/general, where we can change the download folder. \n\n\nAlso, we can find the pyLoad install folder in /info page\n\nSo, we can change the value of Download folder to the template path. Then through /json/add_package we can upload a crafted template file to RCE.\n```python\n@bp.route(\"/json/add_package\", methods=[\"POST\"], endpoint=\"add_package\")\n# @apiver_check\n@login_required(\"ADD\")\ndef add_package():\n api = flask.current_app.config[\"PYLOAD_API\"]\n\n package_name = flask.request.form.get(\"add_name\", \"New Package\").strip()\n queue = int(flask.request.form[\"add_dest\"])\n links = [l.strip() for l in flask.request.form[\"add_links\"].splitlines()]\n pw = flask.request.form.get(\"add_password\", \"\").strip(\"\\n\\r\")\n\n try:\n file = flask.request.files[\"add_file\"]\n\n if file.filename:\n if not package_name or package_name == \"New Package\":\n package_name = file.filename\n\n file_path = os.path.join(\n api.get_config_value(\"general\", \"storage_folder\"), \"tmp_\" + file.filename\n )\n file.save(file_path)\n links.insert(0, file_path)\n\n except Exception:\n pass\n\n urls = [url for url in links if url.strip()]\n pack = api.add_package(package_name, urls, queue)\n if pw:\n data = {\"password\": pw}\n api.set_package_data(pack, data)\n\n return jsonify(True)\n```\n### PoC\nFirst login into the admin page, then visit the info page to get the path of pyload installation folder.\nSecond, change the download folder to PYLOAD_INSTALL_DIR/ webui/app/templates/\nThird, upload crafted template file through /json/add_package through parameter add_file\nthe content of crafted template file and its filename is \"341.html\":\n```\n{{x.__init__.__globals__[\u0027__builtins__\u0027][\u0027eval\u0027](\"__import__(\u0027os\u0027).popen(\u0027whoami\u0027).read()\")}}\n```\n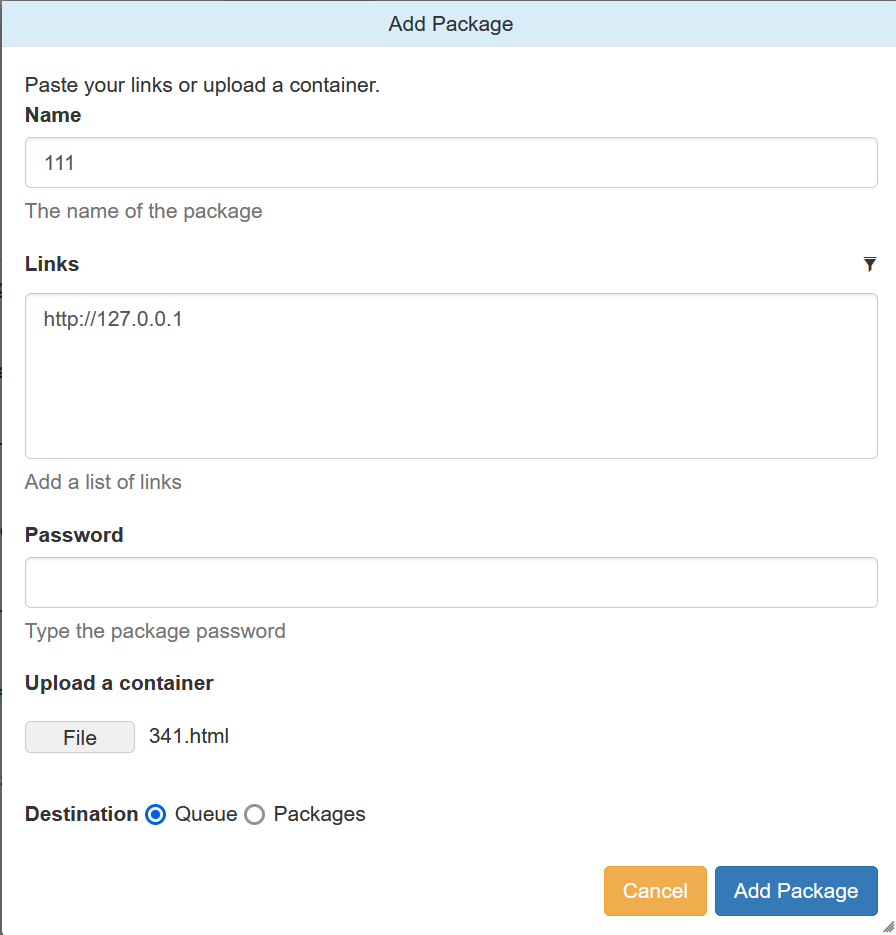\nLast, visit http://TARGET/render/tmp_341.html to trigger the RCE\n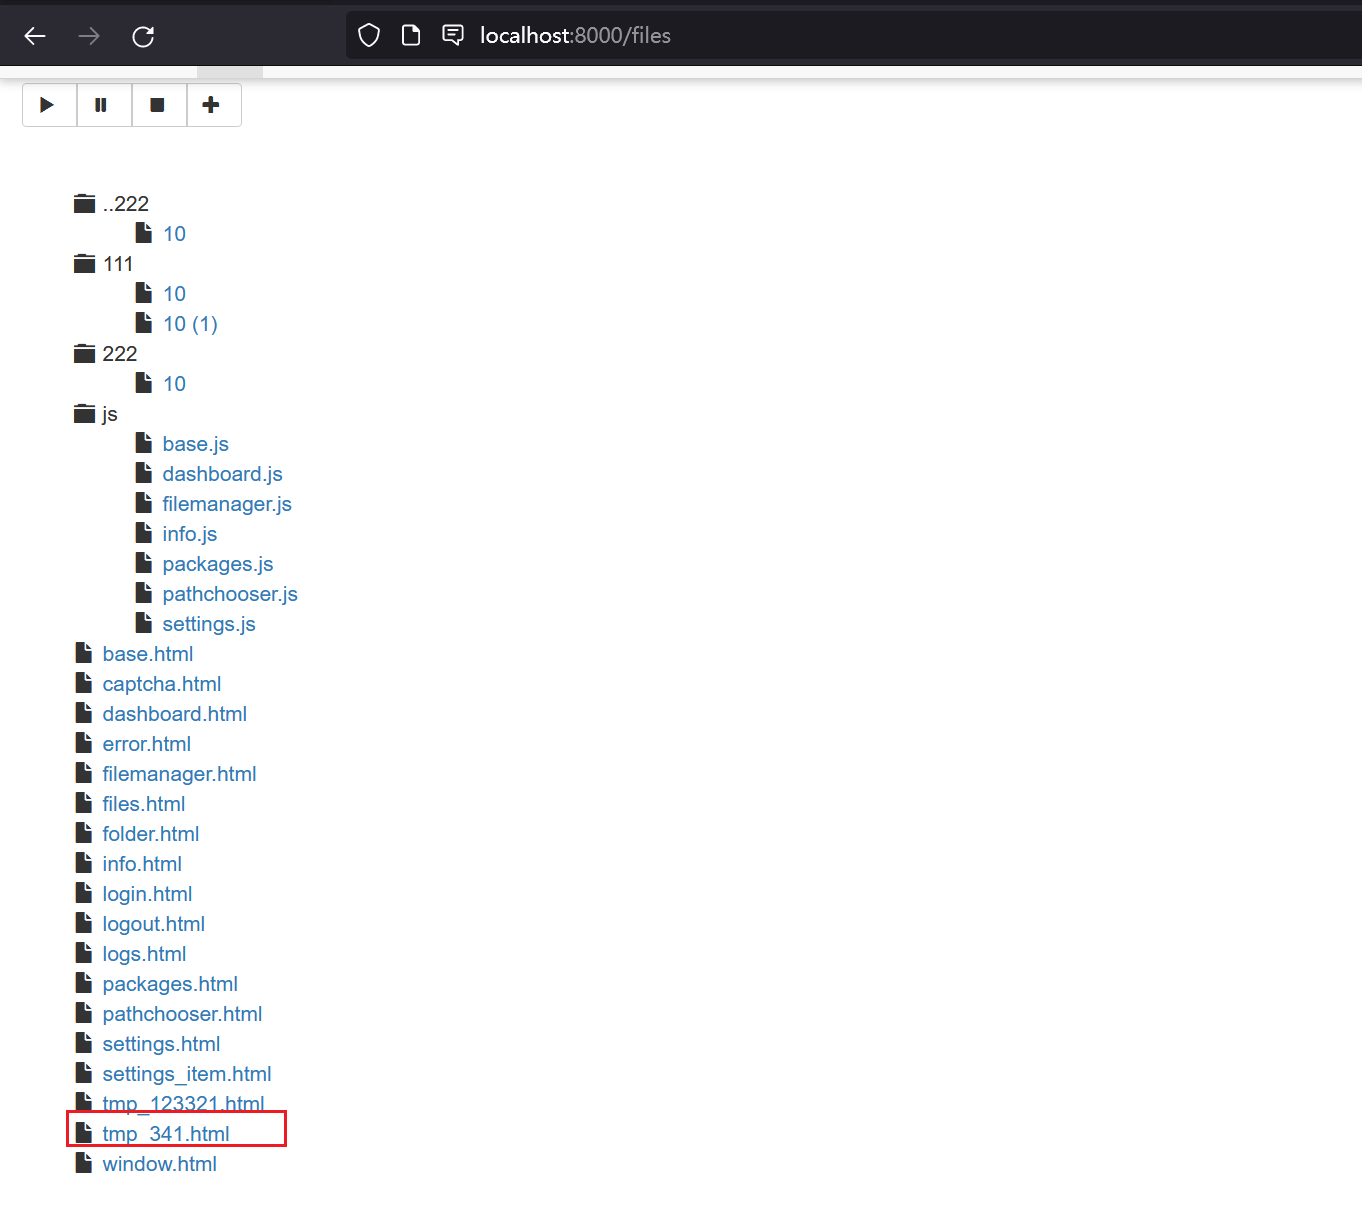\n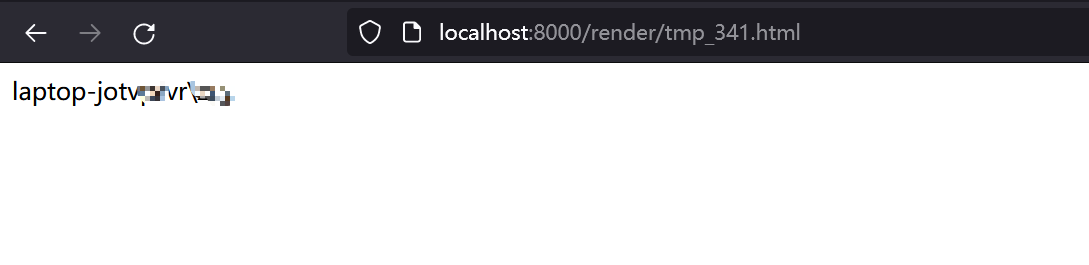\n\n### Impact\nIt is a RCE vulnerability and I think it affects all versions. In earlier version 0.4.20, the trigger difference is the pyload installation folder path difference and the upload file must with extension \".js\" .\nThe render js code in version 0.4.20:\n```python\n@route(\"/media/js/\u003cpath:re:.+\\.js\u003e\")\ndef js_dynamic(path):\n response.headers[\u0027Expires\u0027] = time.strftime(\"%a, %d %b %Y %H:%M:%S GMT\",\n time.gmtime(time.time() + 60 * 60 * 24 * 2))\n response.headers[\u0027Cache-control\u0027] = \"public\"\n response.headers[\u0027Content-Type\u0027] = \"text/javascript; charset=UTF-8\"\n\n try:\n # static files are not rendered\n if \"static\" not in path and \"mootools\" not in path:\n t = env.get_template(\"js/%s\" % path)\n return t.render()\n else:\n return static_file(path, root=join(PROJECT_DIR, \"media\", \"js\"))\n except:\n return HTTPError(404, \"Not Found\")\n```",
"id": "GHSA-3f7w-p8vr-4v5f",
"modified": "2024-04-26T18:51:15Z",
"published": "2024-04-24T21:16:59Z",
"references": [
{
"type": "WEB",
"url": "https://github.com/pyload/pyload/security/advisories/GHSA-3f7w-p8vr-4v5f"
},
{
"type": "ADVISORY",
"url": "https://nvd.nist.gov/vuln/detail/CVE-2024-32880"
},
{
"type": "PACKAGE",
"url": "https://github.com/pyload/pyload"
}
],
"schema_version": "1.4.0",
"severity": [
{
"score": "CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:C/C:H/I:H/A:H",
"type": "CVSS_V3"
}
],
"summary": "pyLoad allows upload to arbitrary folder lead to RCE"
}
GSD-2024-32880
Vulnerability from gsd - Updated: 2024-04-20 05:02{
"gsd": {
"metadata": {
"exploitCode": "unknown",
"remediation": "unknown",
"reportConfidence": "confirmed",
"type": "vulnerability"
},
"osvSchema": {
"aliases": [
"CVE-2024-32880"
],
"details": "pyload is an open-source Download Manager written in pure Python. An authenticated user can change the download folder and upload a crafted template to the specified folder lead to remote code execution. There is no fix available at the time of publication.",
"id": "GSD-2024-32880",
"modified": "2024-04-20T05:02:00.467829Z",
"schema_version": "1.4.0"
}
},
"namespaces": {
"cve.org": {
"CVE_data_meta": {
"ASSIGNER": "security-advisories@github.com",
"ID": "CVE-2024-32880",
"STATE": "PUBLIC"
},
"affects": {
"vendor": {
"vendor_data": [
{
"product": {
"product_data": [
{
"product_name": "pyload",
"version": {
"version_data": [
{
"version_affected": "=",
"version_value": "\u003c= 4.2.0"
}
]
}
}
]
},
"vendor_name": "pyload"
}
]
}
},
"data_format": "MITRE",
"data_type": "CVE",
"data_version": "4.0",
"description": {
"description_data": [
{
"lang": "eng",
"value": "pyload is an open-source Download Manager written in pure Python. An authenticated user can change the download folder and upload a crafted template to the specified folder lead to remote code execution. There is no fix available at the time of publication."
}
]
},
"impact": {
"cvss": [
{
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "HIGH",
"baseScore": 9.1,
"baseSeverity": "CRITICAL",
"confidentialityImpact": "HIGH",
"integrityImpact": "HIGH",
"privilegesRequired": "HIGH",
"scope": "CHANGED",
"userInteraction": "NONE",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:C/C:H/I:H/A:H",
"version": "3.1"
}
]
},
"problemtype": {
"problemtype_data": [
{
"description": [
{
"cweId": "CWE-434",
"lang": "eng",
"value": "CWE-434: Unrestricted Upload of File with Dangerous Type"
}
]
}
]
},
"references": {
"reference_data": [
{
"name": "https://github.com/pyload/pyload/security/advisories/GHSA-3f7w-p8vr-4v5f",
"refsource": "MISC",
"url": "https://github.com/pyload/pyload/security/advisories/GHSA-3f7w-p8vr-4v5f"
}
]
},
"source": {
"advisory": "GHSA-3f7w-p8vr-4v5f",
"discovery": "UNKNOWN"
}
},
"nvd.nist.gov": {
"cve": {
"descriptions": [
{
"lang": "en",
"value": "pyload is an open-source Download Manager written in pure Python. An authenticated user can change the download folder and upload a crafted template to the specified folder lead to remote code execution. There is no fix available at the time of publication."
}
],
"id": "CVE-2024-32880",
"lastModified": "2024-04-26T19:59:19.793",
"metrics": {
"cvssMetricV31": [
{
"cvssData": {
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "HIGH",
"baseScore": 9.1,
"baseSeverity": "CRITICAL",
"confidentialityImpact": "HIGH",
"integrityImpact": "HIGH",
"privilegesRequired": "HIGH",
"scope": "CHANGED",
"userInteraction": "NONE",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:C/C:H/I:H/A:H",
"version": "3.1"
},
"exploitabilityScore": 2.3,
"impactScore": 6.0,
"source": "security-advisories@github.com",
"type": "Secondary"
}
]
},
"published": "2024-04-26T18:15:45.970",
"references": [
{
"source": "security-advisories@github.com",
"url": "https://github.com/pyload/pyload/security/advisories/GHSA-3f7w-p8vr-4v5f"
}
],
"sourceIdentifier": "security-advisories@github.com",
"vulnStatus": "Awaiting Analysis",
"weaknesses": [
{
"description": [
{
"lang": "en",
"value": "CWE-434"
}
],
"source": "security-advisories@github.com",
"type": "Secondary"
}
]
}
}
}
}
PYSEC-2026-492
Vulnerability from pysec - Published: 2026-06-29 11:50 - Updated: 2026-07-09 17:40Summary
An authenticated user can change the download folder and upload a crafted template to the specified folder lead to remote code execution
Details
example version: 0.5 file:src/pyload/webui/app/blueprints/app_blueprint.py
@bp.route("/render/<path:filename>", endpoint="render")
def render(filename):
    mimetype = mimetypes.guess_type(filename)[0] or "text/html"
    data = render_template(filename)
    return flask.Response(data, mimetype=mimetype)
So, if we can control file in the path "pyload/webui/app/templates" in latest version and path in "module/web/media/js"(the difference is the older version0.4.20 only renders file with extension name ".js"), the render_template func will works like SSTI(server-side template injection) when render the evil file we control.
in /settings page and the choose option general/general, where we can change the download folder.
Also, we can find the pyLoad install folder in /info page
So, we can change the value of Download folder to the template path. Then through /json/add_package we can upload a crafted template file to RCE.
@bp.route("/json/add_package", methods=["POST"], endpoint="add_package")
# @apiver_check
@login_required("ADD")
def add_package():
    api = flask.current_app.config["PYLOAD_API"]

    package_name = flask.request.form.get("add_name", "New Package").strip()
    queue = int(flask.request.form["add_dest"])
    links = [l.strip() for l in flask.request.form["add_links"].splitlines()]
    pw = flask.request.form.get("add_password", "").strip("\n\r")

    try:
        file = flask.request.files["add_file"]

        if file.filename:
            if not package_name or package_name == "New Package":
                package_name = file.filename

            file_path = os.path.join(
                api.get_config_value("general", "storage_folder"), "tmp_" + file.filename
            )
            file.save(file_path)
            links.insert(0, file_path)

    except Exception:
        pass

    urls = [url for url in links if url.strip()]
    pack = api.add_package(package_name, urls, queue)
    if pw:
        data = {"password": pw}
        api.set_package_data(pack, data)

    return jsonify(True)
PoC
First login into the admin page, then visit the info page to get the path of pyload installation folder. Second, change the download folder to PYLOAD_INSTALL_DIR/ webui/app/templates/ Third, upload crafted template file through /json/add_package through parameter add_file the content of crafted template file and its filename is "341.html":
{{x.__init__.__globals__['__builtins__']['eval']("__import__('os').popen('whoami').read()")}}
Last, visit http://TARGET/render/tmp_341.html to trigger the RCE
Impact
It is a RCE vulnerability and I think it affects all versions. In earlier version 0.4.20, the trigger difference is the pyload installation folder path difference and the upload file must with extension ".js" . The render js code in version 0.4.20:
@route("/media/js/<path:re:.+\.js>")
def js_dynamic(path):
    response.headers['Expires'] = time.strftime("%a, %d %b %Y %H:%M:%S GMT",
                                                time.gmtime(time.time() + 60 * 60 * 24 * 2))
    response.headers['Cache-control'] = "public"
    response.headers['Content-Type'] = "text/javascript; charset=UTF-8"

    try:
        # static files are not rendered
        if "static" not in path and "mootools" not in path:
            t = env.get_template("js/%s" % path)
            return t.render()
        else:
            return static_file(path, root=join(PROJECT_DIR, "media", "js"))
    except:
        return HTTPError(404, "Not Found")
| Name | purl | pyload-ng | pkg:pypi/pyload-ng |
|---|
{
"affected": [
{
"package": {
"ecosystem": "PyPI",
"name": "pyload-ng",
"purl": "pkg:pypi/pyload-ng"
},
"ranges": [
{
"events": [
{
"introduced": "0"
},
{
"last_affected": "0.5.0"
}
],
"type": "ECOSYSTEM"
}
],
"versions": [
"0.5.0a5.dev528",
"0.5.0a5.dev532",
"0.5.0a5.dev535",
"0.5.0a5.dev536",
"0.5.0a5.dev537",
"0.5.0a5.dev539",
"0.5.0a5.dev540",
"0.5.0a5.dev545",
"0.5.0a5.dev562",
"0.5.0a5.dev564",
"0.5.0a5.dev565",
"0.5.0a6.dev570",
"0.5.0a6.dev578",
"0.5.0a6.dev587",
"0.5.0a7.dev596",
"0.5.0a8.dev602",
"0.5.0a9.dev615",
"0.5.0a9.dev629",
"0.5.0a9.dev632",
"0.5.0a9.dev641",
"0.5.0a9.dev643",
"0.5.0a9.dev655",
"0.5.0a9.dev806",
"0.5.0b1.dev1",
"0.5.0b1.dev2",
"0.5.0b1.dev3",
"0.5.0b1.dev4",
"0.5.0b1.dev5",
"0.5.0b2.dev10",
"0.5.0b2.dev11",
"0.5.0b2.dev12",
"0.5.0b2.dev9",
"0.5.0b3.dev100",
"0.5.0b3.dev13",
"0.5.0b3.dev14",
"0.5.0b3.dev17",
"0.5.0b3.dev18",
"0.5.0b3.dev19",
"0.5.0b3.dev20",
"0.5.0b3.dev21",
"0.5.0b3.dev22",
"0.5.0b3.dev24",
"0.5.0b3.dev26",
"0.5.0b3.dev27",
"0.5.0b3.dev28",
"0.5.0b3.dev29",
"0.5.0b3.dev30",
"0.5.0b3.dev31",
"0.5.0b3.dev32",
"0.5.0b3.dev33",
"0.5.0b3.dev34",
"0.5.0b3.dev35",
"0.5.0b3.dev38",
"0.5.0b3.dev39",
"0.5.0b3.dev40",
"0.5.0b3.dev41",
"0.5.0b3.dev42",
"0.5.0b3.dev43",
"0.5.0b3.dev44",
"0.5.0b3.dev45",
"0.5.0b3.dev46",
"0.5.0b3.dev47",
"0.5.0b3.dev48",
"0.5.0b3.dev49",
"0.5.0b3.dev50",
"0.5.0b3.dev51",
"0.5.0b3.dev52",
"0.5.0b3.dev53",
"0.5.0b3.dev54",
"0.5.0b3.dev57",
"0.5.0b3.dev60",
"0.5.0b3.dev62",
"0.5.0b3.dev64",
"0.5.0b3.dev65",
"0.5.0b3.dev66",
"0.5.0b3.dev67",
"0.5.0b3.dev68",
"0.5.0b3.dev69",
"0.5.0b3.dev70",
"0.5.0b3.dev71",
"0.5.0b3.dev72",
"0.5.0b3.dev73",
"0.5.0b3.dev74",
"0.5.0b3.dev75",
"0.5.0b3.dev76",
"0.5.0b3.dev77",
"0.5.0b3.dev78",
"0.5.0b3.dev79",
"0.5.0b3.dev80",
"0.5.0b3.dev81",
"0.5.0b3.dev82",
"0.5.0b3.dev85",
"0.5.0b3.dev87",
"0.5.0b3.dev88",
"0.5.0b3.dev89",
"0.5.0b3.dev90",
"0.5.0b3.dev91",
"0.5.0b3.dev92",
"0.5.0b3.dev93",
"0.5.0b3.dev94",
"0.5.0b3.dev95",
"0.5.0b3.dev96",
"0.5.0b3.dev97",
"0.5.0b3.dev98",
"0.5.0b3.dev99",
"0.5.0b3.dev101"
]
}
],
"aliases": [
"CVE-2024-32880",
"GHSA-3f7w-p8vr-4v5f"
],
"details": "### Summary\nAn authenticated user can change the download folder and upload a crafted template to the specified folder lead to remote code execution\n\n### Details\nexample version: 0.5\nfile:src/pyload/webui/app/blueprints/app_blueprint.py\n```python\n@bp.route(\"/render/\u003cpath:filename\u003e\", endpoint=\"render\")\ndef render(filename):\n mimetype = mimetypes.guess_type(filename)[0] or \"text/html\"\n data = render_template(filename)\n return flask.Response(data, mimetype=mimetype)\n```\nSo, if we can control file in the path \"pyload/webui/app/templates\" in latest version and path in \"module/web/media/js\"(the difference is the older version0.4.20 only renders file with extension name \".js\"), the render_template func will works like SSTI(server-side template injection) when render the evil file we control.\n\nin /settings page and the choose option general/general, where we can change the download folder. \n\n \nAlso, we can find the pyLoad install folder in /info page\n\n So, we can change the value of Download folder to the template path. Then through /json/add_package we can upload a crafted template file to RCE.\n```python\n@bp.route(\"/json/add_package\", methods=[\"POST\"], endpoint=\"add_package\")\n# @apiver_check\n@login_required(\"ADD\")\ndef add_package():\n api = flask.current_app.config[\"PYLOAD_API\"]\n\n package_name = flask.request.form.get(\"add_name\", \"New Package\").strip()\n queue = int(flask.request.form[\"add_dest\"])\n links = [l.strip() for l in flask.request.form[\"add_links\"].splitlines()]\n pw = flask.request.form.get(\"add_password\", \"\").strip(\"\\n\\r\")\n\n try:\n file = flask.request.files[\"add_file\"]\n\n if file.filename:\n if not package_name or package_name == \"New Package\":\n package_name = file.filename\n\n file_path = os.path.join(\n api.get_config_value(\"general\", \"storage_folder\"), \"tmp_\" + file.filename\n )\n file.save(file_path)\n links.insert(0, file_path)\n\n except Exception:\n pass\n\n urls = [url for url in links if url.strip()]\n pack = api.add_package(package_name, urls, queue)\n if pw:\n data = {\"password\": pw}\n api.set_package_data(pack, data)\n\n return jsonify(True)\n```\n### PoC\nFirst login into the admin page, then visit the info page to get the path of pyload installation folder.\nSecond, change the download folder to PYLOAD_INSTALL_DIR/ webui/app/templates/\nThird, upload crafted template file through /json/add_package through parameter add_file\nthe content of crafted template file and its filename is \"341.html\":\n```\n{{x.__init__.__globals__[\u0027__builtins__\u0027][\u0027eval\u0027](\"__import__(\u0027os\u0027).popen(\u0027whoami\u0027).read()\")}}\n```\n\n Last, visit http://TARGET/render/tmp_341.html to trigger the RCE\n\n \n \n### Impact\nIt is a RCE vulnerability and I think it affects all versions. In earlier version 0.4.20, the trigger difference is the pyload installation folder path difference and the upload file must with extension \".js\" .\nThe render js code in version 0.4.20:\n```python\n@route(\"/media/js/\u003cpath:re:.+\\.js\u003e\")\ndef js_dynamic(path):\n response.headers[\u0027Expires\u0027] = time.strftime(\"%a, %d %b %Y %H:%M:%S GMT\",\n time.gmtime(time.time() + 60 * 60 * 24 * 2))\n response.headers[\u0027Cache-control\u0027] = \"public\"\n response.headers[\u0027Content-Type\u0027] = \"text/javascript; charset=UTF-8\"\n\n try:\n # static files are not rendered\n if \"static\" not in path and \"mootools\" not in path:\n t = env.get_template(\"js/%s\" % path)\n return t.render()\n else:\n return static_file(path, root=join(PROJECT_DIR, \"media\", \"js\"))\n except:\n return HTTPError(404, \"Not Found\")\n```",
"id": "PYSEC-2026-492",
"modified": "2026-07-09T17:40:16.770673Z",
"published": "2026-06-29T11:50:39.394067Z",
"references": [
{
"type": "WEB",
"url": "https://github.com/pyload/pyload/security/advisories/GHSA-3f7w-p8vr-4v5f"
},
{
"type": "ADVISORY",
"url": "https://nvd.nist.gov/vuln/detail/CVE-2024-32880"
},
{
"type": "PACKAGE",
"url": "https://github.com/pyload/pyload"
},
{
"type": "PACKAGE",
"url": "https://pypi.org/project/pyload-ng"
},
{
"type": "ADVISORY",
"url": "https://github.com/advisories/GHSA-3f7w-p8vr-4v5f"
}
],
"severity": [
{
"score": "CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:C/C:H/I:H/A:H",
"type": "CVSS_V3"
}
],
"summary": "pyLoad allows upload to arbitrary folder lead to RCE"
}
Sightings
| Author | Source | Type | Date | Other |
|---|
Nomenclature
- Seen: The vulnerability was mentioned, discussed, or observed by the user.
- Confirmed: The vulnerability has been validated from an analyst's perspective.
- Published Proof of Concept: A public proof of concept is available for this vulnerability.
- Exploited: The vulnerability was observed as exploited by the user who reported the sighting.
- Patched: The vulnerability was observed as successfully patched by the user who reported the sighting.
- Not exploited: The vulnerability was not observed as exploited by the user who reported the sighting.
- Not confirmed: The user expressed doubt about the validity of the vulnerability.
- Not patched: The vulnerability was not observed as successfully patched by the user who reported the sighting.

The approach is described in our paper Mapping CVEs to MITRE ATT&CK Techniques: A Curated Gold-Set Classifier and the Limits of LLM-Assisted Label Expansion.
Browse all ATT&CK techniques and the vulnerabilities related to each.
Related by attack behaviour
Vulnerabilities whose description is nearest to this one in the vector space of the CIRCL/vulnerability-attack-technique-biencoder model. This is a similarity search over the bi-encoder space (plain cosine), not a classification, and it has no measured accuracy.