CVE-2024-29179 (GCVE-0-2024-29179)
Vulnerability from cvelistv5 – Published: 2024-03-25 20:27 – Updated: 2025-04-10 18:29- CWE-79 - Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting')
| URL | Tags |
|---|---|
| https://github.com/thorsten/phpMyFAQ/security/adv… | x_refsource_CONFIRM |
{
"containers": {
"adp": [
{
"metrics": [
{
"other": {
"content": {
"id": "CVE-2024-29179",
"options": [
{
"Exploitation": "none"
},
{
"Automatable": "no"
},
{
"Technical Impact": "partial"
}
],
"role": "CISA Coordinator",
"timestamp": "2024-07-16T17:47:56.549461Z",
"version": "2.0.3"
},
"type": "ssvc"
}
}
],
"providerMetadata": {
"dateUpdated": "2025-04-10T18:29:53.455Z",
"orgId": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
"shortName": "CISA-ADP"
},
"title": "CISA ADP Vulnrichment"
},
{
"providerMetadata": {
"dateUpdated": "2024-08-02T01:10:54.091Z",
"orgId": "af854a3a-2127-422b-91ae-364da2661108",
"shortName": "CVE"
},
"references": [
{
"name": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-hm8r-95g3-5hj9",
"tags": [
"x_refsource_CONFIRM",
"x_transferred"
],
"url": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-hm8r-95g3-5hj9"
}
],
"title": "CVE Program Container"
}
],
"cna": {
"affected": [
{
"product": "phpMyFAQ",
"vendor": "thorsten",
"versions": [
{
"status": "affected",
"version": "3.2.5"
}
]
}
],
"descriptions": [
{
"lang": "en",
"value": "phpMyFAQ is an open source FAQ web application for PHP 8.1+ and MySQL, PostgreSQL and other databases. An attacker with admin privileges can upload an attachment containing JS code without extension and the application will render it as HTML which allows for XSS attacks."
}
],
"metrics": [
{
"cvssV3_0": {
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "LOW",
"baseScore": 4.3,
"baseSeverity": "MEDIUM",
"confidentialityImpact": "LOW",
"integrityImpact": "LOW",
"privilegesRequired": "HIGH",
"scope": "UNCHANGED",
"userInteraction": "REQUIRED",
"vectorString": "CVSS:3.0/AV:N/AC:L/PR:H/UI:R/S:U/C:L/I:L/A:L",
"version": "3.0"
}
}
],
"problemTypes": [
{
"descriptions": [
{
"cweId": "CWE-79",
"description": "CWE-79: Improper Neutralization of Input During Web Page Generation (\u0027Cross-site Scripting\u0027)",
"lang": "en",
"type": "CWE"
}
]
}
],
"providerMetadata": {
"dateUpdated": "2024-03-25T20:27:55.083Z",
"orgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
"shortName": "GitHub_M"
},
"references": [
{
"name": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-hm8r-95g3-5hj9",
"tags": [
"x_refsource_CONFIRM"
],
"url": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-hm8r-95g3-5hj9"
}
],
"source": {
"advisory": "GHSA-hm8r-95g3-5hj9",
"discovery": "UNKNOWN"
},
"title": "phpMyFAQ Stored Cross-site Scripting at File Attachments"
}
},
"cveMetadata": {
"assignerOrgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
"assignerShortName": "GitHub_M",
"cveId": "CVE-2024-29179",
"datePublished": "2024-03-25T20:27:55.083Z",
"dateReserved": "2024-03-18T17:07:00.092Z",
"dateUpdated": "2025-04-10T18:29:53.455Z",
"state": "PUBLISHED"
},
"dataType": "CVE_RECORD",
"dataVersion": "5.1",
"vulnerability-lookup:meta": {
"epss": {
"cve": "CVE-2024-29179",
"date": "2026-10-23",
"epss": "0.00508",
"percentile": "0.4256"
},
"nvd": {
"cve": {
"affected": [
{
"affectedData": [
{
"product": "phpMyFAQ",
"vendor": "thorsten",
"versions": [
{
"status": "affected",
"version": "3.2.5"
}
]
}
],
"source": "security-advisories@github.com"
}
],
"configurations": [
{
"nodes": [
{
"cpeMatch": [
{
"criteria": "cpe:2.3:a:phpmyfaq:phpmyfaq:3.2.5:*:*:*:*:*:*:*",
"matchCriteriaId": "99BD7923-9316-46E2-B3C4-33105AD9E901",
"vulnerable": true
}
],
"negate": false,
"operator": "OR"
}
]
}
],
"cveTags": [],
"descriptions": [
{
"lang": "en",
"value": "phpMyFAQ is an open source FAQ web application for PHP 8.1+ and MySQL, PostgreSQL and other databases. An attacker with admin privileges can upload an attachment containing JS code without extension and the application will render it as HTML which allows for XSS attacks."
},
{
"lang": "es",
"value": "phpMyFAQ es una aplicaci\u00f3n web de preguntas frecuentes de c\u00f3digo abierto para PHP 8.1+ y MySQL, PostgreSQL y otras bases de datos. Un atacante con privilegios de administrador puede cargar un archivo adjunto que contenga c\u00f3digo JS sin extensi\u00f3n y la aplicaci\u00f3n lo representar\u00e1 como HTML, lo que permite ataques XSS."
}
],
"id": "CVE-2024-29179",
"lastModified": "2026-06-17T07:22:34.323",
"metrics": {
"cvssMetricV30": [
{
"cvssData": {
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "LOW",
"baseScore": 4.3,
"baseSeverity": "MEDIUM",
"confidentialityImpact": "LOW",
"integrityImpact": "LOW",
"privilegesRequired": "HIGH",
"scope": "UNCHANGED",
"userInteraction": "REQUIRED",
"vectorString": "CVSS:3.0/AV:N/AC:L/PR:H/UI:R/S:U/C:L/I:L/A:L",
"version": "3.0"
},
"exploitabilityScore": 0.9,
"impactScore": 3.4,
"source": "security-advisories@github.com",
"type": "Secondary"
}
],
"cvssMetricV31": [
{
"cvssData": {
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "NONE",
"baseScore": 4.8,
"baseSeverity": "MEDIUM",
"confidentialityImpact": "LOW",
"integrityImpact": "LOW",
"privilegesRequired": "HIGH",
"scope": "CHANGED",
"userInteraction": "REQUIRED",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:H/UI:R/S:C/C:L/I:L/A:N",
"version": "3.1"
},
"exploitabilityScore": 1.7,
"impactScore": 2.7,
"source": "nvd@nist.gov",
"type": "Primary"
}
],
"ssvcV203": [
{
"source": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
"ssvcData": {
"id": "CVE-2024-29179",
"options": [
{
"exploitation": "none"
},
{
"automatable": "no"
},
{
"technicalImpact": "partial"
}
],
"role": "CISA Coordinator",
"timestamp": "2024-07-16T17:47:56.549461Z",
"version": "2.0.3"
}
}
]
},
"published": "2024-03-25T21:15:47.050",
"references": [
{
"source": "security-advisories@github.com",
"tags": [
"Exploit",
"Vendor Advisory"
],
"url": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-hm8r-95g3-5hj9"
},
{
"source": "af854a3a-2127-422b-91ae-364da2661108",
"tags": [
"Exploit",
"Vendor Advisory"
],
"url": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-hm8r-95g3-5hj9"
}
],
"sourceIdentifier": "security-advisories@github.com",
"vulnStatus": "Analyzed",
"weaknesses": [
{
"description": [
{
"lang": "en",
"value": "CWE-79"
}
],
"source": "security-advisories@github.com",
"type": "Secondary"
},
{
"description": [
{
"lang": "en",
"value": "CWE-79"
}
],
"source": "nvd@nist.gov",
"type": "Primary"
}
]
}
},
"redhat_vex": {
"current_release_date": "2025-05-28T21:10:25+00:00",
"cve": "CVE-2024-29179",
"id": "CVE-2024-29179",
"initial_release_date": "2024-01-01T00:00:00+00:00",
"product_status:known_not_affected": "1",
"source": "Red Hat CSAF VEX",
"status": "final",
"title": "phpMyFAQ Stored Cross-site Scripting at File Attachments",
"url": "https://security.access.redhat.com/data/csaf/v2/vex/2024/cve-2024-29179.json",
"version": "3"
},
"vulnrichment": {
"containers": {
"adp": [
{
"providerMetadata": {
"dateUpdated": "2024-08-02T01:10:54.091Z",
"orgId": "af854a3a-2127-422b-91ae-364da2661108",
"shortName": "CVE"
},
"references": [
{
"name": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-hm8r-95g3-5hj9",
"tags": [
"x_refsource_CONFIRM",
"x_transferred"
],
"url": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-hm8r-95g3-5hj9"
}
],
"title": "CVE Program Container"
},
{
"metrics": [
{
"other": {
"content": {
"id": "CVE-2024-29179",
"options": [
{
"Exploitation": "none"
},
{
"Automatable": "no"
},
{
"Technical Impact": "partial"
}
],
"role": "CISA Coordinator",
"timestamp": "2024-07-16T17:47:56.549461Z",
"version": "2.0.3"
},
"type": "ssvc"
}
}
],
"providerMetadata": {
"dateUpdated": "2024-07-16T17:48:02.964Z",
"orgId": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
"shortName": "CISA-ADP"
},
"title": "CISA ADP Vulnrichment"
}
],
"cna": {
"affected": [
{
"product": "phpMyFAQ",
"vendor": "thorsten",
"versions": [
{
"status": "affected",
"version": "3.2.5"
}
]
}
],
"descriptions": [
{
"lang": "en",
"value": "phpMyFAQ is an open source FAQ web application for PHP 8.1+ and MySQL, PostgreSQL and other databases. An attacker with admin privileges can upload an attachment containing JS code without extension and the application will render it as HTML which allows for XSS attacks."
}
],
"metrics": [
{
"cvssV3_0": {
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "LOW",
"baseScore": 4.3,
"baseSeverity": "MEDIUM",
"confidentialityImpact": "LOW",
"integrityImpact": "LOW",
"privilegesRequired": "HIGH",
"scope": "UNCHANGED",
"userInteraction": "REQUIRED",
"vectorString": "CVSS:3.0/AV:N/AC:L/PR:H/UI:R/S:U/C:L/I:L/A:L",
"version": "3.0"
}
}
],
"problemTypes": [
{
"descriptions": [
{
"cweId": "CWE-79",
"description": "CWE-79: Improper Neutralization of Input During Web Page Generation (\u0027Cross-site Scripting\u0027)",
"lang": "en",
"type": "CWE"
}
]
}
],
"providerMetadata": {
"dateUpdated": "2024-03-25T20:27:55.083Z",
"orgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
"shortName": "GitHub_M"
},
"references": [
{
"name": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-hm8r-95g3-5hj9",
"tags": [
"x_refsource_CONFIRM"
],
"url": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-hm8r-95g3-5hj9"
}
],
"source": {
"advisory": "GHSA-hm8r-95g3-5hj9",
"discovery": "UNKNOWN"
},
"title": "phpMyFAQ Stored Cross-site Scripting at File Attachments"
}
},
"cveMetadata": {
"assignerOrgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
"assignerShortName": "GitHub_M",
"cveId": "CVE-2024-29179",
"datePublished": "2024-03-25T20:27:55.083Z",
"dateReserved": "2024-03-18T17:07:00.092Z",
"dateUpdated": "2025-04-10T18:29:53.455Z",
"state": "PUBLISHED"
},
"dataType": "CVE_RECORD",
"dataVersion": "5.1"
}
}
}
BDU:2024-02322 (CVE-2024-29179)
Vulnerability from fstec – Published: 2024-03-27 – Updated: 2024-03-27 – View on bdu.fstec.ru Exploit publicly available Fixed- CWE-79 - Непринятие мер по защите структуры веб-страницы (или \«Межсайтовая сценарная атака\»)
{
  "CVSS 2.0": "AV:N/AC:L/Au:M/C:P/I:P/A:P",
  "CVSS 3.0": "AV:N/AC:L/PR:H/UI:R/S:U/C:L/I:L/A:L",
  "CVSS 4.0": null,
  "remediation_\u0418\u0434\u0435\u043d\u0442\u0438\u0444\u0438\u043a\u0430\u0442\u043e\u0440": null,
  "remediation_\u041d\u0430\u0438\u043c\u0435\u043d\u043e\u0432\u0430\u043d\u0438\u0435": null,
  "\u0412\u0435\u043d\u0434\u043e\u0440 \u041f\u041e": "\u0421\u043e\u043e\u0431\u0449\u0435\u0441\u0442\u0432\u043e \u0441\u0432\u043e\u0431\u043e\u0434\u043d\u043e\u0433\u043e \u043f\u0440\u043e\u0433\u0440\u0430\u043c\u043c\u043d\u043e\u0433\u043e \u043e\u0431\u0435\u0441\u043f\u0435\u0447\u0435\u043d\u0438\u044f",
  "\u0412\u0435\u0440\u0441\u0438\u044f \u041f\u041e": "\u043e\u0442 3.2.5 \u0434\u043e 3.2.6 (phpMyFAQ)",
  "\u0412\u043e\u0437\u043c\u043e\u0436\u043d\u044b\u0435 \u043c\u0435\u0440\u044b \u043f\u043e \u0443\u0441\u0442\u0440\u0430\u043d\u0435\u043d\u0438\u044e": "\u0418\u0441\u043f\u043e\u043b\u044c\u0437\u043e\u0432\u0430\u043d\u0438\u0435 \u0440\u0435\u043a\u043e\u043c\u0435\u043d\u0434\u0430\u0446\u0438\u0439:\nhttps://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-hm8r-95g3-5hj9",
  "\u0414\u0430\u0442\u0430 \u0432\u044b\u044f\u0432\u043b\u0435\u043d\u0438\u044f": "25.03.2024",
  "\u0414\u0430\u0442\u0430 \u043f\u043e\u0441\u043b\u0435\u0434\u043d\u0435\u0433\u043e \u043e\u0431\u043d\u043e\u0432\u043b\u0435\u043d\u0438\u044f": "27.03.2024",
  "\u0414\u0430\u0442\u0430 \u043f\u0443\u0431\u043b\u0438\u043a\u0430\u0446\u0438\u0438": "27.03.2024",
  "\u0418\u0434\u0435\u043d\u0442\u0438\u0444\u0438\u043a\u0430\u0442\u043e\u0440": "BDU:2024-02322",
  "\u0418\u0434\u0435\u043d\u0442\u0438\u0444\u0438\u043a\u0430\u0442\u043e\u0440\u044b \u0434\u0440\u0443\u0433\u0438\u0445 \u0441\u0438\u0441\u0442\u0435\u043c \u043e\u043f\u0438\u0441\u0430\u043d\u0438\u0439 \u0443\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u0438": "CVE-2024-29179",
  "\u0418\u043d\u0444\u043e\u0440\u043c\u0430\u0446\u0438\u044f \u043e\u0431 \u0443\u0441\u0442\u0440\u0430\u043d\u0435\u043d\u0438\u0438": "\u0423\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u044c \u0443\u0441\u0442\u0440\u0430\u043d\u0435\u043d\u0430",
  "\u041a\u043b\u0430\u0441\u0441 \u0443\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u0438": "\u0423\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u044c \u043a\u043e\u0434\u0430",
  "\u041d\u0430\u0437\u0432\u0430\u043d\u0438\u0435 \u041f\u041e": "phpMyFAQ",
  "\u041d\u0430\u0438\u043c\u0435\u043d\u043e\u0432\u0430\u043d\u0438\u0435 \u041e\u0421 \u0438 \u0442\u0438\u043f \u0430\u043f\u043f\u0430\u0440\u0430\u0442\u043d\u043e\u0439 \u043f\u043b\u0430\u0442\u0444\u043e\u0440\u043c\u044b": null,
  "\u041d\u0430\u0438\u043c\u0435\u043d\u043e\u0432\u0430\u043d\u0438\u0435 \u0443\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u0438": "\u0423\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u044c \u0432\u0435\u0431-\u043f\u0440\u0438\u043b\u043e\u0436\u0435\u043d\u0438\u044f phpMyFAQ, \u043f\u043e\u0437\u0432\u043e\u043b\u044f\u044e\u0449\u0430\u044f \u043d\u0430\u0440\u0443\u0448\u0438\u0442\u0435\u043b\u044e \u043f\u0440\u043e\u0432\u043e\u0434\u0438\u0442\u044c \u043c\u0435\u0436\u0441\u0430\u0439\u0442\u043e\u0432\u044b\u0435 \u0441\u0446\u0435\u043d\u0430\u0440\u043d\u044b\u0435 \u0430\u0442\u0430\u043a\u0438 (XSS)",
  "\u041d\u0430\u043b\u0438\u0447\u0438\u0435 \u044d\u043a\u0441\u043f\u043b\u043e\u0439\u0442\u0430": "\u0421\u0443\u0449\u0435\u0441\u0442\u0432\u0443\u0435\u0442 \u0432 \u043e\u0442\u043a\u0440\u044b\u0442\u043e\u043c \u0434\u043e\u0441\u0442\u0443\u043f\u0435",
  "\u041e\u043f\u0438\u0441\u0430\u043d\u0438\u0435 \u043e\u0448\u0438\u0431\u043a\u0438 CWE": "\u041d\u0435\u043f\u0440\u0438\u043d\u044f\u0442\u0438\u0435 \u043c\u0435\u0440 \u043f\u043e \u0437\u0430\u0449\u0438\u0442\u0435 \u0441\u0442\u0440\u0443\u043a\u0442\u0443\u0440\u044b \u0432\u0435\u0431-\u0441\u0442\u0440\u0430\u043d\u0438\u0446\u044b (\u0438\u043b\u0438 \\\u00ab\u041c\u0435\u0436\u0441\u0430\u0439\u0442\u043e\u0432\u0430\u044f \u0441\u0446\u0435\u043d\u0430\u0440\u043d\u0430\u044f \u0430\u0442\u0430\u043a\u0430\\\u00bb) (CWE-79)",
  "\u041e\u043f\u0438\u0441\u0430\u043d\u0438\u0435 \u0443\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u0438": "\u0423\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u044c \u0432\u0435\u0431-\u043f\u0440\u0438\u043b\u043e\u0436\u0435\u043d\u0438\u044f phpMyFAQ \u0441\u0432\u044f\u0437\u0430\u043d\u0430 \u0441 \u043d\u0435\u043f\u0440\u0438\u043d\u044f\u0442\u0438\u0435\u043c \u043c\u0435\u0440 \u043f\u043e \u0437\u0430\u0449\u0438\u0442\u0435 \u0441\u0442\u0440\u0443\u043a\u0442\u0443\u0440\u044b \u0432\u0435\u0431-\u0441\u0442\u0440\u0430\u043d\u0438\u0446\u044b. \u042d\u043a\u0441\u043f\u043b\u0443\u0430\u0442\u0430\u0446\u0438\u044f \u0443\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u0438 \u043c\u043e\u0436\u0435\u0442 \u043f\u043e\u0437\u0432\u043e\u043b\u0438\u0442\u044c \u043d\u0430\u0440\u0443\u0448\u0438\u0442\u0435\u043b\u044e, \u0434\u0435\u0439\u0441\u0442\u0432\u0443\u044e\u0449\u0435\u043c\u0443 \u0443\u0434\u0430\u043b\u0451\u043d\u043d\u043e, \u043f\u0440\u043e\u0432\u043e\u0434\u0438\u0442\u044c \u043c\u0435\u0436\u0441\u0430\u0439\u0442\u043e\u0432\u044b\u0435 \u0441\u0446\u0435\u043d\u0430\u0440\u043d\u044b\u0435 \u0430\u0442\u0430\u043a\u0438 (XSS)  \u0441 \u043f\u043e\u043c\u043e\u0449\u044c\u044e \u0441\u043f\u0435\u0446\u0438\u0430\u043b\u044c\u043d\u043e \u0441\u043e\u0437\u0434\u0430\u043d\u043d\u044b\u0445 \u0444\u0430\u0439\u043b\u043e\u0432 \u0441 \u0440\u0430\u0441\u0448\u0438\u0440\u0435\u043d\u0438\u0435\u043c .html",
  "\u041f\u043e\u0441\u043b\u0435\u0434\u0441\u0442\u0432\u0438\u044f \u044d\u043a\u0441\u043f\u043b\u0443\u0430\u0442\u0430\u0446\u0438\u0438 \u0443\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u0438": null,
  "\u041f\u0440\u043e\u0447\u0430\u044f \u0438\u043d\u0444\u043e\u0440\u043c\u0430\u0446\u0438\u044f": null,
  "\u0421\u0432\u044f\u0437\u044c \u0441 \u0438\u043d\u0446\u0438\u0434\u0435\u043d\u0442\u0430\u043c\u0438 \u0418\u0411": "\u0414\u0430\u043d\u043d\u044b\u0435 \u0443\u0442\u043e\u0447\u043d\u044f\u044e\u0442\u0441\u044f",
  "\u0421\u043e\u0441\u0442\u043e\u044f\u043d\u0438\u0435 \u0443\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u0438": "\u041e\u043f\u0443\u0431\u043b\u0438\u043a\u043e\u0432\u0430\u043d\u0430",
  "\u0421\u043f\u043e\u0441\u043e\u0431 \u0443\u0441\u0442\u0440\u0430\u043d\u0435\u043d\u0438\u044f": "\u041e\u0431\u043d\u043e\u0432\u043b\u0435\u043d\u0438\u0435 \u043f\u0440\u043e\u0433\u0440\u0430\u043c\u043c\u043d\u043e\u0433\u043e \u043e\u0431\u0435\u0441\u043f\u0435\u0447\u0435\u043d\u0438\u044f",
  "\u0421\u043f\u043e\u0441\u043e\u0431 \u044d\u043a\u0441\u043f\u043b\u0443\u0430\u0442\u0430\u0446\u0438\u0438": "\u0418\u043d\u044a\u0435\u043a\u0446\u0438\u044f",
  "\u0421\u0441\u044b\u043b\u043a\u0438 \u043d\u0430 \u0438\u0441\u0442\u043e\u0447\u043d\u0438\u043a\u0438": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-hm8r-95g3-5hj9\nhttps://vuldb.com/?id.257892",
  "\u0421\u0442\u0430\u0442\u0443\u0441 \u0443\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u0438": "\u041f\u043e\u0434\u0442\u0432\u0435\u0440\u0436\u0434\u0435\u043d\u0430 \u043f\u0440\u043e\u0438\u0437\u0432\u043e\u0434\u0438\u0442\u0435\u043b\u0435\u043c",
  "\u0422\u0438\u043f \u041f\u041e": "\u041f\u0440\u0438\u043a\u043b\u0430\u0434\u043d\u043e\u0435 \u041f\u041e \u0438\u043d\u0444\u043e\u0440\u043c\u0430\u0446\u0438\u043e\u043d\u043d\u044b\u0445 \u0441\u0438\u0441\u0442\u0435\u043c",
  "\u0422\u0438\u043f \u043e\u0448\u0438\u0431\u043a\u0438 CWE": "CWE-79",
  "\u0423\u0440\u043e\u0432\u0435\u043d\u044c \u043e\u043f\u0430\u0441\u043d\u043e\u0441\u0442\u0438 \u0443\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u0438": "\u0421\u0440\u0435\u0434\u043d\u0438\u0439 \u0443\u0440\u043e\u0432\u0435\u043d\u044c \u043e\u043f\u0430\u0441\u043d\u043e\u0441\u0442\u0438 (\u0431\u0430\u0437\u043e\u0432\u0430\u044f \u043e\u0446\u0435\u043d\u043a\u0430 CVSS 2.0 \u0441\u043e\u0441\u0442\u0430\u0432\u043b\u044f\u0435\u0442 5,8)\n\u0421\u0440\u0435\u0434\u043d\u0438\u0439 \u0443\u0440\u043e\u0432\u0435\u043d\u044c \u043e\u043f\u0430\u0441\u043d\u043e\u0441\u0442\u0438 (\u0431\u0430\u0437\u043e\u0432\u0430\u044f \u043e\u0446\u0435\u043d\u043a\u0430 CVSS 3.0 \u0441\u043e\u0441\u0442\u0430\u0432\u043b\u044f\u0435\u0442 4,3)"
}
FKIE_CVE-2024-29179
Vulnerability from fkie_nvd - Published: 2024-03-25 21:15 - Updated: 2026-06-17 07:22| URL | Tags | ||
|---|---|---|---|
| security-advisories@github.com | https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-hm8r-95g3-5hj9 | Exploit, Vendor Advisory | |
| af854a3a-2127-422b-91ae-364da2661108 | https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-hm8r-95g3-5hj9 | Exploit, Vendor Advisory |
{
  "affected": [
    {
      "affectedData": [
        {
          "product": "phpMyFAQ",
          "vendor": "thorsten",
          "versions": [
            {
              "status": "affected",
              "version": "3.2.5"
            }
          ]
        }
      ],
      "source": "security-advisories@github.com"
    }
  ],
  "configurations": [
    {
      "nodes": [
        {
          "cpeMatch": [
            {
              "criteria": "cpe:2.3:a:phpmyfaq:phpmyfaq:3.2.5:*:*:*:*:*:*:*",
              "matchCriteriaId": "99BD7923-9316-46E2-B3C4-33105AD9E901",
              "vulnerable": true
            }
          ],
          "negate": false,
          "operator": "OR"
        }
      ]
    }
  ],
  "cveTags": [],
  "descriptions": [
    {
      "lang": "en",
      "value": "phpMyFAQ is an open source FAQ web application for PHP 8.1+ and MySQL, PostgreSQL and other databases. An attacker with admin privileges can upload an attachment containing JS code without extension and the application will render it as HTML which allows for XSS attacks."
    },
    {
      "lang": "es",
      "value": "phpMyFAQ es una aplicaci\u00f3n web de preguntas frecuentes de c\u00f3digo abierto para PHP 8.1+ y MySQL, PostgreSQL y otras bases de datos. Un atacante con privilegios de administrador puede cargar un archivo adjunto que contenga c\u00f3digo JS sin extensi\u00f3n y la aplicaci\u00f3n lo representar\u00e1 como HTML, lo que permite ataques XSS."
    }
  ],
  "id": "CVE-2024-29179",
  "lastModified": "2026-06-17T07:22:34.323",
  "metrics": {
    "cvssMetricV30": [
      {
        "cvssData": {
          "attackComplexity": "LOW",
          "attackVector": "NETWORK",
          "availabilityImpact": "LOW",
          "baseScore": 4.3,
          "baseSeverity": "MEDIUM",
          "confidentialityImpact": "LOW",
          "integrityImpact": "LOW",
          "privilegesRequired": "HIGH",
          "scope": "UNCHANGED",
          "userInteraction": "REQUIRED",
          "vectorString": "CVSS:3.0/AV:N/AC:L/PR:H/UI:R/S:U/C:L/I:L/A:L",
          "version": "3.0"
        },
        "exploitabilityScore": 0.9,
        "impactScore": 3.4,
        "source": "security-advisories@github.com",
        "type": "Secondary"
      }
    ],
    "cvssMetricV31": [
      {
        "cvssData": {
          "attackComplexity": "LOW",
          "attackVector": "NETWORK",
          "availabilityImpact": "NONE",
          "baseScore": 4.8,
          "baseSeverity": "MEDIUM",
          "confidentialityImpact": "LOW",
          "integrityImpact": "LOW",
          "privilegesRequired": "HIGH",
          "scope": "CHANGED",
          "userInteraction": "REQUIRED",
          "vectorString": "CVSS:3.1/AV:N/AC:L/PR:H/UI:R/S:C/C:L/I:L/A:N",
          "version": "3.1"
        },
        "exploitabilityScore": 1.7,
        "impactScore": 2.7,
        "source": "nvd@nist.gov",
        "type": "Primary"
      }
    ],
    "ssvcV203": [
      {
        "source": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
        "ssvcData": {
          "id": "CVE-2024-29179",
          "options": [
            {
              "exploitation": "none"
            },
            {
              "automatable": "no"
            },
            {
              "technicalImpact": "partial"
            }
          ],
          "role": "CISA Coordinator",
          "timestamp": "2024-07-16T17:47:56.549461Z",
          "version": "2.0.3"
        }
      }
    ]
  },
  "published": "2024-03-25T21:15:47.050",
  "references": [
    {
      "source": "security-advisories@github.com",
      "tags": [
        "Exploit",
        "Vendor Advisory"
      ],
      "url": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-hm8r-95g3-5hj9"
    },
    {
      "source": "af854a3a-2127-422b-91ae-364da2661108",
      "tags": [
        "Exploit",
        "Vendor Advisory"
      ],
      "url": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-hm8r-95g3-5hj9"
    }
  ],
  "sourceIdentifier": "security-advisories@github.com",
  "vulnStatus": "Analyzed",
  "weaknesses": [
    {
      "description": [
        {
          "lang": "en",
          "value": "CWE-79"
        }
      ],
      "source": "security-advisories@github.com",
      "type": "Secondary"
    },
    {
      "description": [
        {
          "lang": "en",
          "value": "CWE-79"
        }
      ],
      "source": "nvd@nist.gov",
      "type": "Primary"
    }
  ]
}
GHSA-HM8R-95G3-5HJ9
Vulnerability from github – Published: 2024-03-25 19:45 – Updated: 2024-03-25 22:31Summary
An attacker with admin privileges can upload an attachment containing JS code without extension and the application will render it as HTML which allows for XSS attacks.
Details
When attachments are uploaded without an extension, the application renders it as HTML by default. Therefore allowing attackers to upload .html files containing javascript code to perform XSS attacks. The direct file path to the uploaded attachment is also easily obtainable as it is made up of substrings of the file's MD5 hashes.
PoC
-
Admin users can upload attachments containing XSS payloads in files without extensions to bypass the .html extension check.
-
Since the path of the uploaded file is built entirely on the file’s MD5 hash and the attachment directory, it is possible for an attacker to know the direct path of the uploaded file.
E.g file MD5 hash: 38fff51cb7248a06d6142c6bdf846831
URL will be: http://127.0.0.1/phpmyfaq/attachments/38fff/51cb7/248a0/6d6142c6bdf846831

- /attachments
- /38fff (first 5 chars of MD5 hash)
- /51cb7 (next 5 chars of MD5 hash)
- /248a0 (next 5 chars of MD5 hash)
- /6d6142c6bdf846831 (remaining chars of MD5 hash)
- Even though the attachment was uploaded without a file extension, it is still rendered as .html, hence triggering the XSS payload.
Impact
This allows an attacker to execute arbitrary client side JavaScript within the context of another user's phpMyFAQ session.
{
"affected": [
{
"package": {
"ecosystem": "Packagist",
"name": "phpmyfaq/phpmyfaq"
},
"ranges": [
{
"events": [
{
"introduced": "3.2.5"
},
{
"fixed": "3.2.6"
}
],
"type": "ECOSYSTEM"
}
],
"versions": [
"3.2.5"
]
}
],
"aliases": [
"CVE-2024-29179"
],
"database_specific": {
"cwe_ids": [
"CWE-79"
],
"github_reviewed": true,
"github_reviewed_at": "2024-03-25T19:45:12Z",
"nvd_published_at": "2024-03-25T21:15:47Z",
"severity": "MODERATE"
},
"details": "### Summary\nAn attacker with admin privileges can upload an attachment containing JS code without extension and the application will render it as HTML which allows for XSS attacks.\n\n### Details\nWhen attachments are uploaded without an extension, the application renders it as HTML by default. Therefore allowing attackers to upload .html files containing javascript code to perform XSS attacks. The direct file path to the uploaded attachment is also easily obtainable as it is made up of substrings of the file\u0027s MD5 hashes.\n\n### PoC\n1. Admin users can upload attachments containing XSS payloads in files without extensions to bypass the .html extension check.\n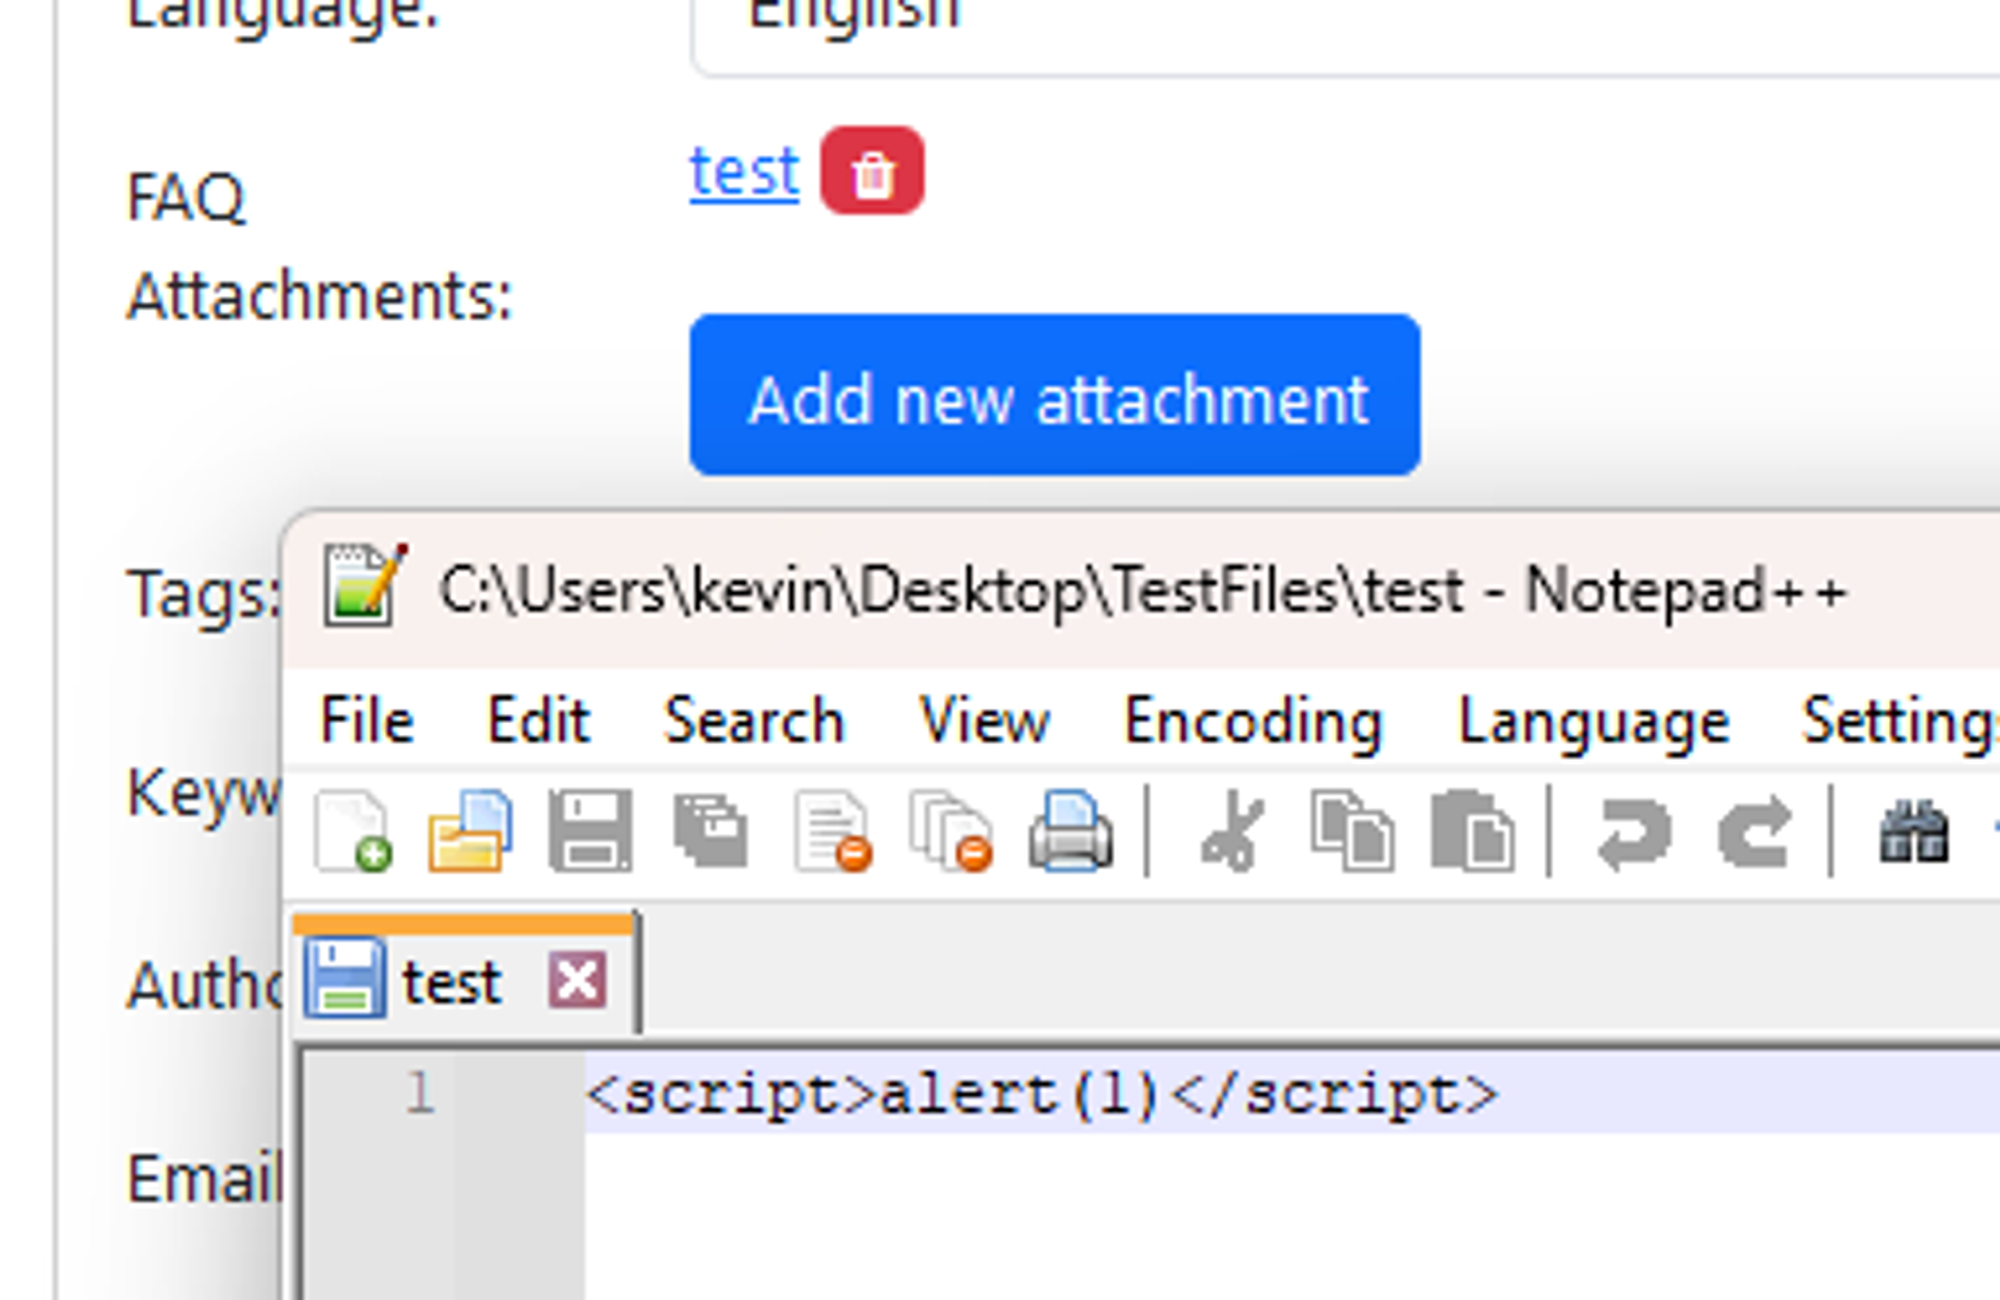\n\n2. Since the path of the uploaded file is built entirely on the file\u2019s MD5 hash and the attachment directory, it is possible for an attacker to know the direct path of the uploaded file.\n\n E.g file MD5 hash: 38fff51cb7248a06d6142c6bdf846831\n\n URL will be: http://127.0.0.1/phpmyfaq/attachments/38fff/51cb7/248a0/6d6142c6bdf846831\n\n - /attachments\n - /38fff (first 5 chars of MD5 hash)\n - /51cb7 (next 5 chars of MD5 hash)\n - /248a0 (next 5 chars of MD5 hash)\n - /6d6142c6bdf846831 (remaining chars of MD5 hash)\n\n3. Even though the attachment was uploaded without a file extension, it is still rendered as .html, hence triggering the XSS payload.\n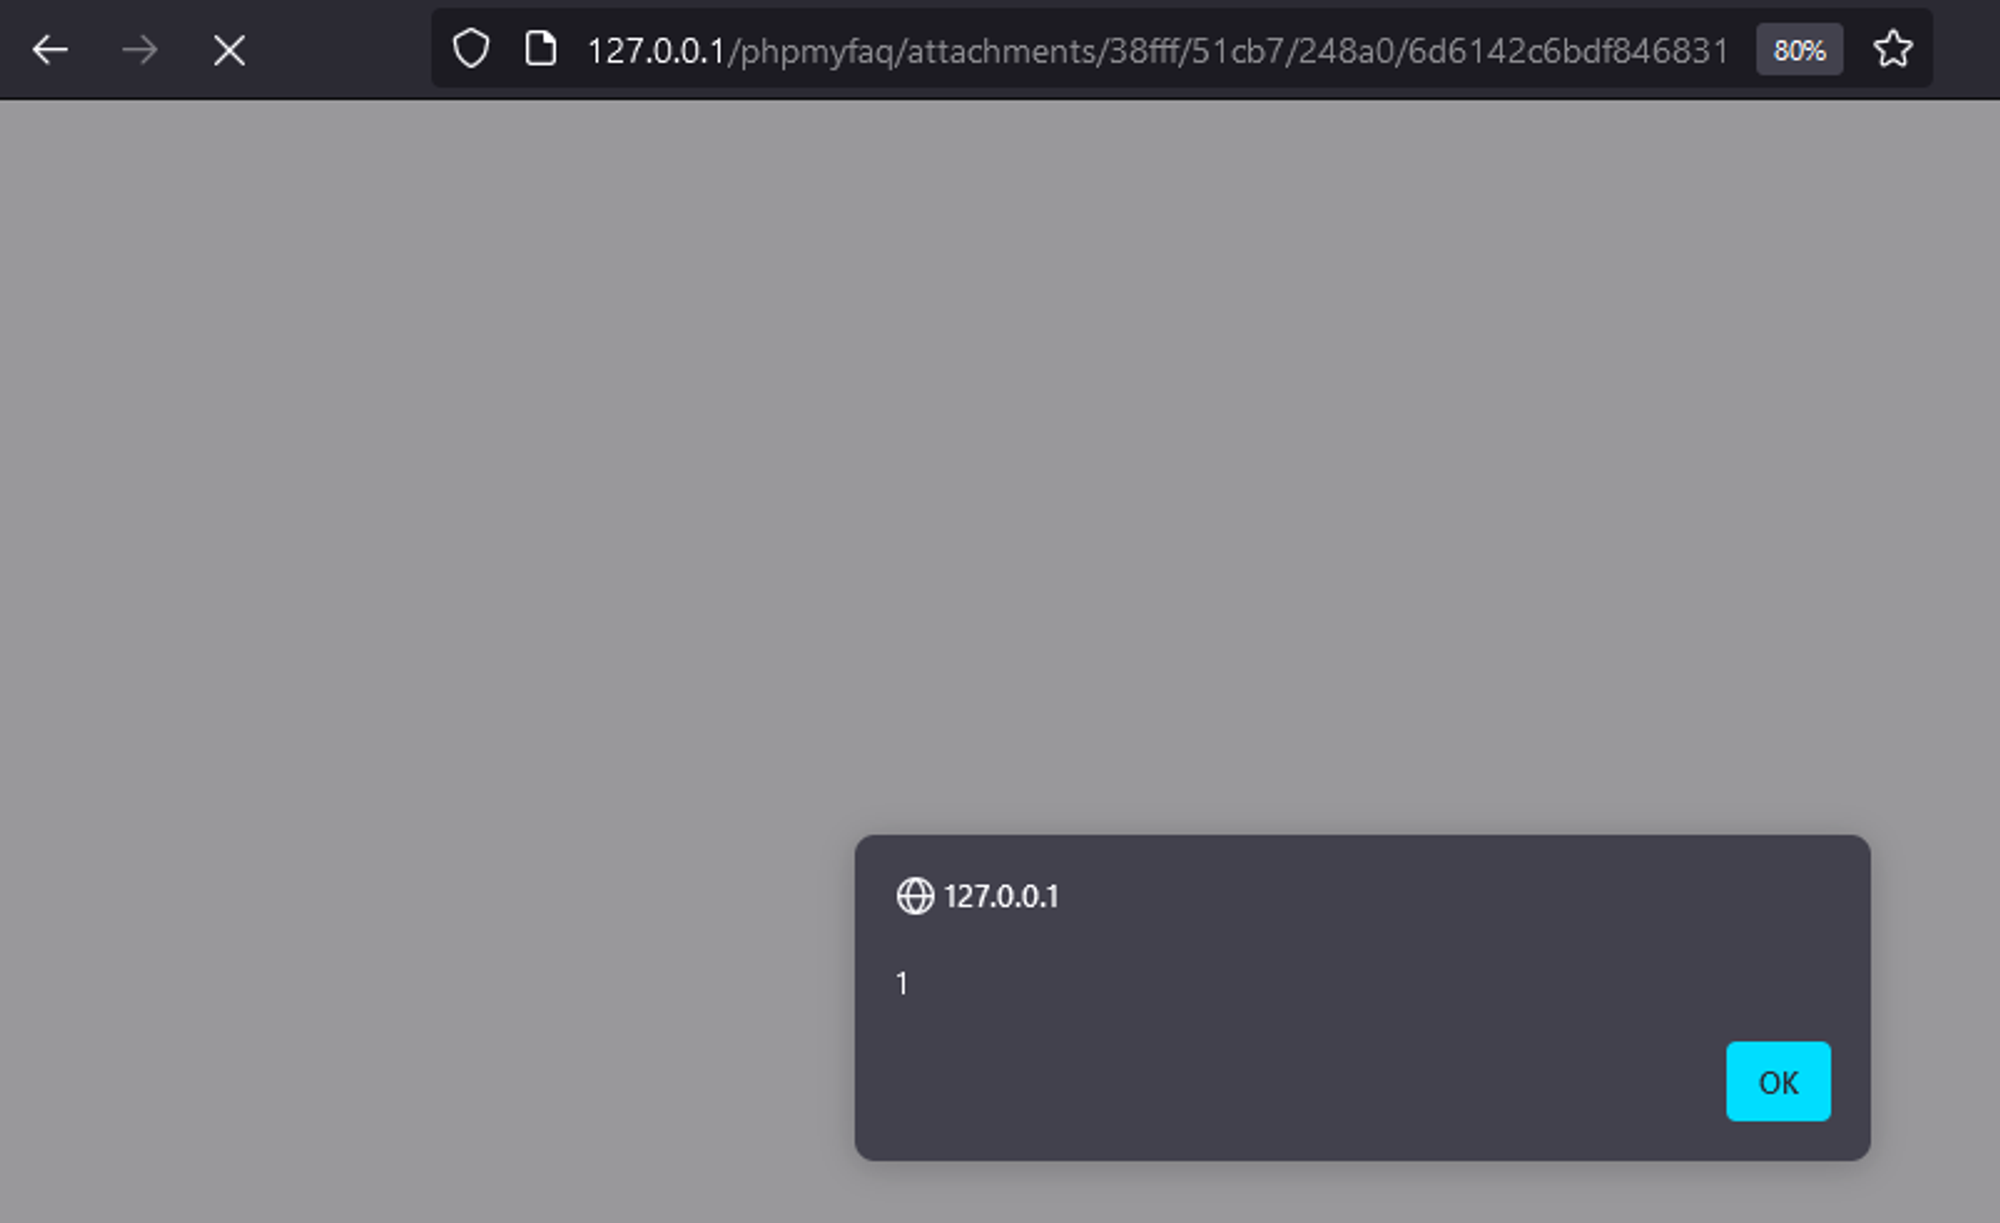\n\n### Impact\nThis allows an attacker to execute arbitrary client side JavaScript within the context of another user\u0027s phpMyFAQ session.\n\n",
"id": "GHSA-hm8r-95g3-5hj9",
"modified": "2024-03-25T22:31:44Z",
"published": "2024-03-25T19:45:12Z",
"references": [
{
"type": "WEB",
"url": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-hm8r-95g3-5hj9"
},
{
"type": "ADVISORY",
"url": "https://nvd.nist.gov/vuln/detail/CVE-2024-29179"
},
{
"type": "PACKAGE",
"url": "https://github.com/thorsten/phpMyFAQ"
}
],
"schema_version": "1.4.0",
"severity": [
{
"score": "CVSS:3.1/AV:N/AC:L/PR:H/UI:R/S:U/C:L/I:L/A:L",
"type": "CVSS_V3"
}
],
"summary": "phpMyFAQ Stored Cross-site Scripting at File Attachments"
}
GSD-2024-29179
Vulnerability from gsd - Updated: 2024-04-02 05:02{
"gsd": {
"metadata": {
"exploitCode": "unknown",
"remediation": "unknown",
"reportConfidence": "confirmed",
"type": "vulnerability"
},
"osvSchema": {
"aliases": [
"CVE-2024-29179"
],
"details": "phpMyFAQ is an open source FAQ web application for PHP 8.1+ and MySQL, PostgreSQL and other databases. An attacker with admin privileges can upload an attachment containing JS code without extension and the application will render it as HTML which allows for XSS attacks.",
"id": "GSD-2024-29179",
"modified": "2024-04-02T05:02:57.446553Z",
"schema_version": "1.4.0"
}
},
"namespaces": {
"cve.org": {
"CVE_data_meta": {
"ASSIGNER": "security-advisories@github.com",
"ID": "CVE-2024-29179",
"STATE": "PUBLIC"
},
"affects": {
"vendor": {
"vendor_data": [
{
"product": {
"product_data": [
{
"product_name": "phpMyFAQ",
"version": {
"version_data": [
{
"version_affected": "=",
"version_value": "3.2.5"
}
]
}
}
]
},
"vendor_name": "thorsten"
}
]
}
},
"data_format": "MITRE",
"data_type": "CVE",
"data_version": "4.0",
"description": {
"description_data": [
{
"lang": "eng",
"value": "phpMyFAQ is an open source FAQ web application for PHP 8.1+ and MySQL, PostgreSQL and other databases. An attacker with admin privileges can upload an attachment containing JS code without extension and the application will render it as HTML which allows for XSS attacks."
}
]
},
"impact": {
"cvss": [
{
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "LOW",
"baseScore": 4.3,
"baseSeverity": "MEDIUM",
"confidentialityImpact": "LOW",
"integrityImpact": "LOW",
"privilegesRequired": "HIGH",
"scope": "UNCHANGED",
"userInteraction": "REQUIRED",
"vectorString": "CVSS:3.0/AV:N/AC:L/PR:H/UI:R/S:U/C:L/I:L/A:L",
"version": "3.0"
}
]
},
"problemtype": {
"problemtype_data": [
{
"description": [
{
"cweId": "CWE-79",
"lang": "eng",
"value": "CWE-79: Improper Neutralization of Input During Web Page Generation (\u0027Cross-site Scripting\u0027)"
}
]
}
]
},
"references": {
"reference_data": [
{
"name": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-hm8r-95g3-5hj9",
"refsource": "MISC",
"url": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-hm8r-95g3-5hj9"
}
]
},
"source": {
"advisory": "GHSA-hm8r-95g3-5hj9",
"discovery": "UNKNOWN"
}
},
"nvd.nist.gov": {
"cve": {
"descriptions": [
{
"lang": "en",
"value": "phpMyFAQ is an open source FAQ web application for PHP 8.1+ and MySQL, PostgreSQL and other databases. An attacker with admin privileges can upload an attachment containing JS code without extension and the application will render it as HTML which allows for XSS attacks."
},
{
"lang": "es",
"value": "phpMyFAQ es una aplicaci\u00f3n web de preguntas frecuentes de c\u00f3digo abierto para PHP 8.1+ y MySQL, PostgreSQL y otras bases de datos. Un atacante con privilegios de administrador puede cargar un archivo adjunto que contenga c\u00f3digo JS sin extensi\u00f3n y la aplicaci\u00f3n lo representar\u00e1 como HTML, lo que permite ataques XSS."
}
],
"id": "CVE-2024-29179",
"lastModified": "2024-03-26T12:55:05.010",
"metrics": {
"cvssMetricV30": [
{
"cvssData": {
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "LOW",
"baseScore": 4.3,
"baseSeverity": "MEDIUM",
"confidentialityImpact": "LOW",
"integrityImpact": "LOW",
"privilegesRequired": "HIGH",
"scope": "UNCHANGED",
"userInteraction": "REQUIRED",
"vectorString": "CVSS:3.0/AV:N/AC:L/PR:H/UI:R/S:U/C:L/I:L/A:L",
"version": "3.0"
},
"exploitabilityScore": 0.9,
"impactScore": 3.4,
"source": "security-advisories@github.com",
"type": "Secondary"
}
]
},
"published": "2024-03-25T21:15:47.050",
"references": [
{
"source": "security-advisories@github.com",
"url": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-hm8r-95g3-5hj9"
}
],
"sourceIdentifier": "security-advisories@github.com",
"vulnStatus": "Awaiting Analysis",
"weaknesses": [
{
"description": [
{
"lang": "en",
"value": "CWE-79"
}
],
"source": "security-advisories@github.com",
"type": "Secondary"
}
]
}
}
}
}
Drag nodes to arrange them. Double-click a related vulnerability to open it, or a source to visit its link. The Physics button on the left tunes the layout and the simulation; the legend at the bottom left hides or shows nodes by kind and by sighting type.
Sightings
| Author | Source | Type | Date | Other |
|---|
Nomenclature
- Seen: The vulnerability was mentioned, discussed, or observed by the user.
- Confirmed: The vulnerability has been validated from an analyst's perspective.
- Published Proof of Concept: A public proof of concept is available for this vulnerability.
- Exploited: The vulnerability was observed as exploited by the user who reported the sighting.
- Patched: The vulnerability was observed as successfully patched by the user who reported the sighting.
- Not exploited: The vulnerability was not observed as exploited by the user who reported the sighting.
- Not confirmed: The user expressed doubt about the validity of the vulnerability.
- Not patched: The vulnerability was not observed as successfully patched by the user who reported the sighting.
Vulnerability timeline
Sightings and recorded dates, grouped by day · UTC
Loading timeline…

The approach is described in our paper Mapping CVEs to MITRE ATT&CK Techniques: A Curated Gold-Set Classifier and the Limits of LLM-Assisted Label Expansion.
Browse all ATT&CK techniques and the vulnerabilities related to each.
Related by attack behaviour
Vulnerabilities whose description is nearest to this one in the vector space of the CIRCL/vulnerability-attack-technique-biencoder model. This is a similarity search over the bi-encoder space (plain cosine), not a classification, and it has no measured accuracy.