CVE-2024-27300 (GCVE-0-2024-27300)
Vulnerability from cvelistv5 – Published: 2024-03-25 18:30 – Updated: 2024-08-02 00:28- CWE-79 - Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting')
| URL | Tags |
|---|---|
| https://github.com/thorsten/phpMyFAQ/security/adv… | x_refsource_CONFIRM |
| https://github.com/thorsten/phpMyFAQ/commit/09336… | x_refsource_MISC |
| https://github.com/thorsten/phpMyFAQ/commit/de903… | x_refsource_MISC |
{
"containers": {
"adp": [
{
"affected": [
{
"cpes": [
"cpe:2.3:a:thorsten:phpmyfaq:*:*:*:*:*:*:*:*"
],
"defaultStatus": "unknown",
"product": "phpmyfaq",
"vendor": "thorsten",
"versions": [
{
"lessThan": "3.2.6",
"status": "affected",
"version": "0",
"versionType": "custom"
}
]
}
],
"metrics": [
{
"other": {
"content": {
"id": "CVE-2024-27300",
"options": [
{
"Exploitation": "poc"
},
{
"Automatable": "no"
},
{
"Technical Impact": "partial"
}
],
"role": "CISA Coordinator",
"timestamp": "2024-03-25T19:29:59.933358Z",
"version": "2.0.3"
},
"type": "ssvc"
}
}
],
"providerMetadata": {
"dateUpdated": "2024-08-01T15:40:57.698Z",
"orgId": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
"shortName": "CISA-ADP"
},
"title": "CISA ADP Vulnrichment"
},
{
"providerMetadata": {
"dateUpdated": "2024-08-02T00:28:00.229Z",
"orgId": "af854a3a-2127-422b-91ae-364da2661108",
"shortName": "CVE"
},
"references": [
{
"name": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-q7g6-xfh2-vhpx",
"tags": [
"x_refsource_CONFIRM",
"x_transferred"
],
"url": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-q7g6-xfh2-vhpx"
},
{
"name": "https://github.com/thorsten/phpMyFAQ/commit/09336b0ff0e0a04aa0c97c5975651af4769d2459",
"tags": [
"x_refsource_MISC",
"x_transferred"
],
"url": "https://github.com/thorsten/phpMyFAQ/commit/09336b0ff0e0a04aa0c97c5975651af4769d2459"
},
{
"name": "https://github.com/thorsten/phpMyFAQ/commit/de90315c9bd4ead5fe6ba5586f6b016843aa8209",
"tags": [
"x_refsource_MISC",
"x_transferred"
],
"url": "https://github.com/thorsten/phpMyFAQ/commit/de90315c9bd4ead5fe6ba5586f6b016843aa8209"
}
],
"title": "CVE Program Container"
}
],
"cna": {
"affected": [
{
"product": "phpMyFAQ",
"vendor": "thorsten",
"versions": [
{
"status": "affected",
"version": "3.2.5"
}
]
}
],
"descriptions": [
{
"lang": "en",
"value": "phpMyFAQ is an open source FAQ web application for PHP 8.1+ and MySQL, PostgreSQL and other databases. The `email` field in phpMyFAQ\u0027s user control panel page is vulnerable to stored XSS attacks due to the inadequacy of PHP\u0027s `FILTER_VALIDATE_EMAIL` function, which only validates the email format, not its content. This vulnerability enables an attacker to execute arbitrary client-side JavaScript within the context of another user\u0027s phpMyFAQ session. This vulnerability is fixed in 3.2.6."
}
],
"metrics": [
{
"cvssV3_1": {
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "LOW",
"baseScore": 5.5,
"baseSeverity": "MEDIUM",
"confidentialityImpact": "LOW",
"integrityImpact": "LOW",
"privilegesRequired": "LOW",
"scope": "UNCHANGED",
"userInteraction": "REQUIRED",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:U/C:L/I:L/A:L",
"version": "3.1"
}
}
],
"problemTypes": [
{
"descriptions": [
{
"cweId": "CWE-79",
"description": "CWE-79: Improper Neutralization of Input During Web Page Generation (\u0027Cross-site Scripting\u0027)",
"lang": "en",
"type": "CWE"
}
]
}
],
"providerMetadata": {
"dateUpdated": "2024-03-25T18:32:00.543Z",
"orgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
"shortName": "GitHub_M"
},
"references": [
{
"name": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-q7g6-xfh2-vhpx",
"tags": [
"x_refsource_CONFIRM"
],
"url": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-q7g6-xfh2-vhpx"
},
{
"name": "https://github.com/thorsten/phpMyFAQ/commit/09336b0ff0e0a04aa0c97c5975651af4769d2459",
"tags": [
"x_refsource_MISC"
],
"url": "https://github.com/thorsten/phpMyFAQ/commit/09336b0ff0e0a04aa0c97c5975651af4769d2459"
},
{
"name": "https://github.com/thorsten/phpMyFAQ/commit/de90315c9bd4ead5fe6ba5586f6b016843aa8209",
"tags": [
"x_refsource_MISC"
],
"url": "https://github.com/thorsten/phpMyFAQ/commit/de90315c9bd4ead5fe6ba5586f6b016843aa8209"
}
],
"source": {
"advisory": "GHSA-q7g6-xfh2-vhpx",
"discovery": "UNKNOWN"
},
"title": "phpMyFAQ Stored XSS at user email"
}
},
"cveMetadata": {
"assignerOrgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
"assignerShortName": "GitHub_M",
"cveId": "CVE-2024-27300",
"datePublished": "2024-03-25T18:30:35.810Z",
"dateReserved": "2024-02-22T18:08:38.875Z",
"dateUpdated": "2024-08-02T00:28:00.229Z",
"state": "PUBLISHED"
},
"dataType": "CVE_RECORD",
"dataVersion": "5.1",
"vulnerability-lookup:meta": {
"epss": {
"cve": "CVE-2024-27300",
"date": "2026-10-15",
"epss": "0.00691",
"percentile": "0.51811"
},
"nvd": {
"cve": {
"affected": [
{
"affectedData": [
{
"product": "phpMyFAQ",
"vendor": "thorsten",
"versions": [
{
"status": "affected",
"version": "3.2.5"
}
]
}
],
"source": "security-advisories@github.com"
},
{
"affectedData": [
{
"cpes": [
"cpe:2.3:a:thorsten:phpmyfaq:*:*:*:*:*:*:*:*"
],
"defaultStatus": "unknown",
"product": "phpmyfaq",
"vendor": "thorsten",
"versions": [
{
"lessThan": "3.2.6",
"status": "affected",
"version": "0",
"versionType": "custom"
}
]
}
],
"source": "134c704f-9b21-4f2e-91b3-4a467353bcc0"
}
],
"configurations": [
{
"nodes": [
{
"cpeMatch": [
{
"criteria": "cpe:2.3:a:phpmyfaq:phpmyfaq:3.2.5:*:*:*:*:*:*:*",
"matchCriteriaId": "99BD7923-9316-46E2-B3C4-33105AD9E901",
"vulnerable": true
}
],
"negate": false,
"operator": "OR"
}
]
}
],
"cveTags": [],
"descriptions": [
{
"lang": "en",
"value": "phpMyFAQ is an open source FAQ web application for PHP 8.1+ and MySQL, PostgreSQL and other databases. The `email` field in phpMyFAQ\u0027s user control panel page is vulnerable to stored XSS attacks due to the inadequacy of PHP\u0027s `FILTER_VALIDATE_EMAIL` function, which only validates the email format, not its content. This vulnerability enables an attacker to execute arbitrary client-side JavaScript within the context of another user\u0027s phpMyFAQ session. This vulnerability is fixed in 3.2.6."
},
{
"lang": "es",
"value": "phpMyFAQ es una aplicaci\u00f3n web de preguntas frecuentes de c\u00f3digo abierto para PHP 8.1+ y MySQL, PostgreSQL y otras bases de datos. El campo `email` en la p\u00e1gina del panel de control de usuario de phpMyFAQ es vulnerable a ataques XSS almacenados debido a la insuficiencia de la funci\u00f3n `FILTER_VALIDATE_EMAIL` de PHP, que solo valida el formato del correo electr\u00f3nico, no su contenido. Esta vulnerabilidad permite a un atacante ejecutar JavaScript arbitrario del lado del cliente dentro del contexto de la sesi\u00f3n phpMyFAQ de otro usuario. Esta vulnerabilidad se soluciona en 3.2.6."
}
],
"id": "CVE-2024-27300",
"lastModified": "2026-06-17T07:19:36.197",
"metrics": {
"cvssMetricV31": [
{
"cvssData": {
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "LOW",
"baseScore": 5.5,
"baseSeverity": "MEDIUM",
"confidentialityImpact": "LOW",
"integrityImpact": "LOW",
"privilegesRequired": "LOW",
"scope": "UNCHANGED",
"userInteraction": "REQUIRED",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:U/C:L/I:L/A:L",
"version": "3.1"
},
"exploitabilityScore": 2.1,
"impactScore": 3.4,
"source": "security-advisories@github.com",
"type": "Secondary"
},
{
"cvssData": {
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "NONE",
"baseScore": 5.4,
"baseSeverity": "MEDIUM",
"confidentialityImpact": "LOW",
"integrityImpact": "LOW",
"privilegesRequired": "LOW",
"scope": "CHANGED",
"userInteraction": "REQUIRED",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:C/C:L/I:L/A:N",
"version": "3.1"
},
"exploitabilityScore": 2.3,
"impactScore": 2.7,
"source": "nvd@nist.gov",
"type": "Primary"
}
],
"ssvcV203": [
{
"source": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
"ssvcData": {
"id": "CVE-2024-27300",
"options": [
{
"exploitation": "poc"
},
{
"automatable": "no"
},
{
"technicalImpact": "partial"
}
],
"role": "CISA Coordinator",
"timestamp": "2024-03-25T19:29:59.933358Z",
"version": "2.0.3"
}
}
]
},
"published": "2024-03-25T19:15:57.807",
"references": [
{
"source": "security-advisories@github.com",
"tags": [
"Patch"
],
"url": "https://github.com/thorsten/phpMyFAQ/commit/09336b0ff0e0a04aa0c97c5975651af4769d2459"
},
{
"source": "security-advisories@github.com",
"tags": [
"Patch"
],
"url": "https://github.com/thorsten/phpMyFAQ/commit/de90315c9bd4ead5fe6ba5586f6b016843aa8209"
},
{
"source": "security-advisories@github.com",
"tags": [
"Exploit",
"Vendor Advisory"
],
"url": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-q7g6-xfh2-vhpx"
},
{
"source": "af854a3a-2127-422b-91ae-364da2661108",
"tags": [
"Patch"
],
"url": "https://github.com/thorsten/phpMyFAQ/commit/09336b0ff0e0a04aa0c97c5975651af4769d2459"
},
{
"source": "af854a3a-2127-422b-91ae-364da2661108",
"tags": [
"Patch"
],
"url": "https://github.com/thorsten/phpMyFAQ/commit/de90315c9bd4ead5fe6ba5586f6b016843aa8209"
},
{
"source": "af854a3a-2127-422b-91ae-364da2661108",
"tags": [
"Exploit",
"Vendor Advisory"
],
"url": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-q7g6-xfh2-vhpx"
}
],
"sourceIdentifier": "security-advisories@github.com",
"vulnStatus": "Analyzed",
"weaknesses": [
{
"description": [
{
"lang": "en",
"value": "CWE-79"
}
],
"source": "security-advisories@github.com",
"type": "Secondary"
},
{
"description": [
{
"lang": "en",
"value": "CWE-79"
}
],
"source": "nvd@nist.gov",
"type": "Primary"
}
]
}
},
"redhat_vex": {
"current_release_date": "2025-05-28T21:30:38+00:00",
"cve": "CVE-2024-27300",
"id": "CVE-2024-27300",
"initial_release_date": "2024-01-01T00:00:00+00:00",
"product_status:known_not_affected": "1",
"source": "Red Hat CSAF VEX",
"status": "final",
"title": "phpMyFAQ Stored XSS at user email",
"url": "https://security.access.redhat.com/data/csaf/v2/vex/2024/cve-2024-27300.json",
"version": "3"
},
"vulnrichment": {
"containers": {
"adp": [
{
"providerMetadata": {
"dateUpdated": "2024-08-02T00:28:00.229Z",
"orgId": "af854a3a-2127-422b-91ae-364da2661108",
"shortName": "CVE"
},
"references": [
{
"name": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-q7g6-xfh2-vhpx",
"tags": [
"x_refsource_CONFIRM",
"x_transferred"
],
"url": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-q7g6-xfh2-vhpx"
},
{
"name": "https://github.com/thorsten/phpMyFAQ/commit/09336b0ff0e0a04aa0c97c5975651af4769d2459",
"tags": [
"x_refsource_MISC",
"x_transferred"
],
"url": "https://github.com/thorsten/phpMyFAQ/commit/09336b0ff0e0a04aa0c97c5975651af4769d2459"
},
{
"name": "https://github.com/thorsten/phpMyFAQ/commit/de90315c9bd4ead5fe6ba5586f6b016843aa8209",
"tags": [
"x_refsource_MISC",
"x_transferred"
],
"url": "https://github.com/thorsten/phpMyFAQ/commit/de90315c9bd4ead5fe6ba5586f6b016843aa8209"
}
],
"title": "CVE Program Container"
},
{
"affected": [
{
"cpes": [
"cpe:2.3:a:thorsten:phpmyfaq:*:*:*:*:*:*:*:*"
],
"defaultStatus": "unknown",
"product": "phpmyfaq",
"vendor": "thorsten",
"versions": [
{
"lessThan": "3.2.6",
"status": "affected",
"version": "0",
"versionType": "custom"
}
]
}
],
"metrics": [
{
"other": {
"content": {
"id": "CVE-2024-27300",
"options": [
{
"Exploitation": "poc"
},
{
"Automatable": "no"
},
{
"Technical Impact": "partial"
}
],
"role": "CISA Coordinator",
"timestamp": "2024-03-25T19:29:59.933358Z",
"version": "2.0.3"
},
"type": "ssvc"
}
}
],
"providerMetadata": {
"dateUpdated": "2024-08-01T15:40:52.146Z",
"orgId": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
"shortName": "CISA-ADP"
},
"title": "CISA ADP Vulnrichment"
}
],
"cna": {
"affected": [
{
"product": "phpMyFAQ",
"vendor": "thorsten",
"versions": [
{
"status": "affected",
"version": "3.2.5"
}
]
}
],
"descriptions": [
{
"lang": "en",
"value": "phpMyFAQ is an open source FAQ web application for PHP 8.1+ and MySQL, PostgreSQL and other databases. The `email` field in phpMyFAQ\u0027s user control panel page is vulnerable to stored XSS attacks due to the inadequacy of PHP\u0027s `FILTER_VALIDATE_EMAIL` function, which only validates the email format, not its content. This vulnerability enables an attacker to execute arbitrary client-side JavaScript within the context of another user\u0027s phpMyFAQ session. This vulnerability is fixed in 3.2.6."
}
],
"metrics": [
{
"cvssV3_1": {
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "LOW",
"baseScore": 5.5,
"baseSeverity": "MEDIUM",
"confidentialityImpact": "LOW",
"integrityImpact": "LOW",
"privilegesRequired": "LOW",
"scope": "UNCHANGED",
"userInteraction": "REQUIRED",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:U/C:L/I:L/A:L",
"version": "3.1"
}
}
],
"problemTypes": [
{
"descriptions": [
{
"cweId": "CWE-79",
"description": "CWE-79: Improper Neutralization of Input During Web Page Generation (\u0027Cross-site Scripting\u0027)",
"lang": "en",
"type": "CWE"
}
]
}
],
"providerMetadata": {
"dateUpdated": "2024-03-25T18:32:00.543Z",
"orgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
"shortName": "GitHub_M"
},
"references": [
{
"name": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-q7g6-xfh2-vhpx",
"tags": [
"x_refsource_CONFIRM"
],
"url": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-q7g6-xfh2-vhpx"
},
{
"name": "https://github.com/thorsten/phpMyFAQ/commit/09336b0ff0e0a04aa0c97c5975651af4769d2459",
"tags": [
"x_refsource_MISC"
],
"url": "https://github.com/thorsten/phpMyFAQ/commit/09336b0ff0e0a04aa0c97c5975651af4769d2459"
},
{
"name": "https://github.com/thorsten/phpMyFAQ/commit/de90315c9bd4ead5fe6ba5586f6b016843aa8209",
"tags": [
"x_refsource_MISC"
],
"url": "https://github.com/thorsten/phpMyFAQ/commit/de90315c9bd4ead5fe6ba5586f6b016843aa8209"
}
],
"source": {
"advisory": "GHSA-q7g6-xfh2-vhpx",
"discovery": "UNKNOWN"
},
"title": "phpMyFAQ Stored XSS at user email"
}
},
"cveMetadata": {
"assignerOrgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
"assignerShortName": "GitHub_M",
"cveId": "CVE-2024-27300",
"datePublished": "2024-03-25T18:30:35.810Z",
"dateReserved": "2024-02-22T18:08:38.875Z",
"dateUpdated": "2024-08-02T00:28:00.229Z",
"state": "PUBLISHED"
},
"dataType": "CVE_RECORD",
"dataVersion": "5.1"
}
}
}
BDU:2024-02325 (CVE-2024-27300)
Vulnerability from fstec – Published: 2024-03-27 – Updated: 2024-03-27 – View on bdu.fstec.ru Exploit publicly available Fixed- CWE-79 - Непринятие мер по защите структуры веб-страницы (или \«Межсайтовая сценарная атака\»)
{
  "CVSS 2.0": "AV:N/AC:L/Au:S/C:P/I:P/A:P",
  "CVSS 3.0": "AV:N/AC:L/PR:L/UI:R/S:U/C:L/I:L/A:L",
  "CVSS 4.0": null,
  "remediation_\u0418\u0434\u0435\u043d\u0442\u0438\u0444\u0438\u043a\u0430\u0442\u043e\u0440": null,
  "remediation_\u041d\u0430\u0438\u043c\u0435\u043d\u043e\u0432\u0430\u043d\u0438\u0435": null,
  "\u0412\u0435\u043d\u0434\u043e\u0440 \u041f\u041e": "\u0421\u043e\u043e\u0431\u0449\u0435\u0441\u0442\u0432\u043e \u0441\u0432\u043e\u0431\u043e\u0434\u043d\u043e\u0433\u043e \u043f\u0440\u043e\u0433\u0440\u0430\u043c\u043c\u043d\u043e\u0433\u043e \u043e\u0431\u0435\u0441\u043f\u0435\u0447\u0435\u043d\u0438\u044f",
  "\u0412\u0435\u0440\u0441\u0438\u044f \u041f\u041e": "\u043e\u0442 3.2.5 \u0434\u043e 3.2.6 (phpMyFAQ)",
  "\u0412\u043e\u0437\u043c\u043e\u0436\u043d\u044b\u0435 \u043c\u0435\u0440\u044b \u043f\u043e \u0443\u0441\u0442\u0440\u0430\u043d\u0435\u043d\u0438\u044e": "\u0418\u0441\u043f\u043e\u043b\u044c\u0437\u043e\u0432\u0430\u043d\u0438\u0435 \u0440\u0435\u043a\u043e\u043c\u0435\u043d\u0434\u0430\u0446\u0438\u0439:\nhttps://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-q7g6-xfh2-vhpx",
  "\u0414\u0430\u0442\u0430 \u0432\u044b\u044f\u0432\u043b\u0435\u043d\u0438\u044f": "25.03.2024",
  "\u0414\u0430\u0442\u0430 \u043f\u043e\u0441\u043b\u0435\u0434\u043d\u0435\u0433\u043e \u043e\u0431\u043d\u043e\u0432\u043b\u0435\u043d\u0438\u044f": "27.03.2024",
  "\u0414\u0430\u0442\u0430 \u043f\u0443\u0431\u043b\u0438\u043a\u0430\u0446\u0438\u0438": "27.03.2024",
  "\u0418\u0434\u0435\u043d\u0442\u0438\u0444\u0438\u043a\u0430\u0442\u043e\u0440": "BDU:2024-02325",
  "\u0418\u0434\u0435\u043d\u0442\u0438\u0444\u0438\u043a\u0430\u0442\u043e\u0440\u044b \u0434\u0440\u0443\u0433\u0438\u0445 \u0441\u0438\u0441\u0442\u0435\u043c \u043e\u043f\u0438\u0441\u0430\u043d\u0438\u0439 \u0443\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u0438": "CVE-2024-27300",
  "\u0418\u043d\u0444\u043e\u0440\u043c\u0430\u0446\u0438\u044f \u043e\u0431 \u0443\u0441\u0442\u0440\u0430\u043d\u0435\u043d\u0438\u0438": "\u0423\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u044c \u0443\u0441\u0442\u0440\u0430\u043d\u0435\u043d\u0430",
  "\u041a\u043b\u0430\u0441\u0441 \u0443\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u0438": "\u0423\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u044c \u043a\u043e\u0434\u0430",
  "\u041d\u0430\u0437\u0432\u0430\u043d\u0438\u0435 \u041f\u041e": "phpMyFAQ",
  "\u041d\u0430\u0438\u043c\u0435\u043d\u043e\u0432\u0430\u043d\u0438\u0435 \u041e\u0421 \u0438 \u0442\u0438\u043f \u0430\u043f\u043f\u0430\u0440\u0430\u0442\u043d\u043e\u0439 \u043f\u043b\u0430\u0442\u0444\u043e\u0440\u043c\u044b": null,
  "\u041d\u0430\u0438\u043c\u0435\u043d\u043e\u0432\u0430\u043d\u0438\u0435 \u0443\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u0438": "\u0423\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u044c \u0444\u0443\u043d\u043a\u0446\u0438\u0438 FILTER_VALIDATE_EMAIL \u0432\u0435\u0431-\u043f\u0440\u0438\u043b\u043e\u0436\u0435\u043d\u0438\u044f phpMyFAQ, \u043f\u043e\u0437\u0432\u043e\u043b\u044f\u044e\u0449\u0430\u044f \u043d\u0430\u0440\u0443\u0448\u0438\u0442\u0435\u043b\u044e \u0432\u044b\u043f\u043e\u043b\u043d\u0438\u0442\u044c \u043f\u0440\u043e\u0438\u0437\u0432\u043e\u043b\u044c\u043d\u044b\u0439 \u043a\u043e\u0434",
  "\u041d\u0430\u043b\u0438\u0447\u0438\u0435 \u044d\u043a\u0441\u043f\u043b\u043e\u0439\u0442\u0430": "\u0421\u0443\u0449\u0435\u0441\u0442\u0432\u0443\u0435\u0442 \u0432 \u043e\u0442\u043a\u0440\u044b\u0442\u043e\u043c \u0434\u043e\u0441\u0442\u0443\u043f\u0435",
  "\u041e\u043f\u0438\u0441\u0430\u043d\u0438\u0435 \u043e\u0448\u0438\u0431\u043a\u0438 CWE": "\u041d\u0435\u043f\u0440\u0438\u043d\u044f\u0442\u0438\u0435 \u043c\u0435\u0440 \u043f\u043e \u0437\u0430\u0449\u0438\u0442\u0435 \u0441\u0442\u0440\u0443\u043a\u0442\u0443\u0440\u044b \u0432\u0435\u0431-\u0441\u0442\u0440\u0430\u043d\u0438\u0446\u044b (\u0438\u043b\u0438 \\\u00ab\u041c\u0435\u0436\u0441\u0430\u0439\u0442\u043e\u0432\u0430\u044f \u0441\u0446\u0435\u043d\u0430\u0440\u043d\u0430\u044f \u0430\u0442\u0430\u043a\u0430\\\u00bb) (CWE-79)",
  "\u041e\u043f\u0438\u0441\u0430\u043d\u0438\u0435 \u0443\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u0438": "\u0423\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u044c \u0444\u0443\u043d\u043a\u0446\u0438\u0438 FILTER_VALIDATE_EMAIL \u0432\u0435\u0431-\u043f\u0440\u0438\u043b\u043e\u0436\u0435\u043d\u0438\u044f phpMyFAQ \u0441\u0432\u044f\u0437\u0430\u043d\u0430 \u0441 \u043d\u0435\u043f\u0440\u0438\u043d\u044f\u0442\u0438\u0435\u043c \u043c\u0435\u0440 \u043f\u043e \u0437\u0430\u0449\u0438\u0442\u0435 \u0441\u0442\u0440\u0443\u043a\u0442\u0443\u0440\u044b \u0432\u0435\u0431-\u0441\u0442\u0440\u0430\u043d\u0438\u0446\u044b. \u042d\u043a\u0441\u043f\u043b\u0443\u0430\u0442\u0430\u0446\u0438\u044f \u0443\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u0438 \u043c\u043e\u0436\u0435\u0442 \u043f\u043e\u0437\u0432\u043e\u043b\u0438\u0442\u044c \u043d\u0430\u0440\u0443\u0448\u0438\u0442\u0435\u043b\u044e, \u0434\u0435\u0439\u0441\u0442\u0432\u0443\u044e\u0449\u0435\u043c\u0443 \u0443\u0434\u0430\u043b\u0451\u043d\u043d\u043e, \u0432\u044b\u043f\u043e\u043b\u043d\u0438\u0442\u044c \u043f\u0440\u043e\u0438\u0437\u0432\u043e\u043b\u044c\u043d\u044b\u0439 \u043a\u043e\u0434",
  "\u041f\u043e\u0441\u043b\u0435\u0434\u0441\u0442\u0432\u0438\u044f \u044d\u043a\u0441\u043f\u043b\u0443\u0430\u0442\u0430\u0446\u0438\u0438 \u0443\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u0438": null,
  "\u041f\u0440\u043e\u0447\u0430\u044f \u0438\u043d\u0444\u043e\u0440\u043c\u0430\u0446\u0438\u044f": null,
  "\u0421\u0432\u044f\u0437\u044c \u0441 \u0438\u043d\u0446\u0438\u0434\u0435\u043d\u0442\u0430\u043c\u0438 \u0418\u0411": "\u0414\u0430\u043d\u043d\u044b\u0435 \u0443\u0442\u043e\u0447\u043d\u044f\u044e\u0442\u0441\u044f",
  "\u0421\u043e\u0441\u0442\u043e\u044f\u043d\u0438\u0435 \u0443\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u0438": "\u041e\u043f\u0443\u0431\u043b\u0438\u043a\u043e\u0432\u0430\u043d\u0430",
  "\u0421\u043f\u043e\u0441\u043e\u0431 \u0443\u0441\u0442\u0440\u0430\u043d\u0435\u043d\u0438\u044f": "\u041e\u0431\u043d\u043e\u0432\u043b\u0435\u043d\u0438\u0435 \u043f\u0440\u043e\u0433\u0440\u0430\u043c\u043c\u043d\u043e\u0433\u043e \u043e\u0431\u0435\u0441\u043f\u0435\u0447\u0435\u043d\u0438\u044f",
  "\u0421\u043f\u043e\u0441\u043e\u0431 \u044d\u043a\u0441\u043f\u043b\u0443\u0430\u0442\u0430\u0446\u0438\u0438": "\u0418\u043d\u044a\u0435\u043a\u0446\u0438\u044f",
  "\u0421\u0441\u044b\u043b\u043a\u0438 \u043d\u0430 \u0438\u0441\u0442\u043e\u0447\u043d\u0438\u043a\u0438": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-q7g6-xfh2-vhpx\nhttps://github.com/thorsten/phpMyFAQ/commit/de90315c9bd4ead5fe6ba5586f6b016843aa8209\nhttps://github.com/thorsten/phpMyFAQ/commit/09336b0ff0e0a04aa0c97c5975651af4769d2459\nhttps://vuldb.com/?id.257889",
  "\u0421\u0442\u0430\u0442\u0443\u0441 \u0443\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u0438": "\u041f\u043e\u0434\u0442\u0432\u0435\u0440\u0436\u0434\u0435\u043d\u0430 \u043f\u0440\u043e\u0438\u0437\u0432\u043e\u0434\u0438\u0442\u0435\u043b\u0435\u043c",
  "\u0422\u0438\u043f \u041f\u041e": "\u041f\u0440\u0438\u043a\u043b\u0430\u0434\u043d\u043e\u0435 \u041f\u041e \u0438\u043d\u0444\u043e\u0440\u043c\u0430\u0446\u0438\u043e\u043d\u043d\u044b\u0445 \u0441\u0438\u0441\u0442\u0435\u043c",
  "\u0422\u0438\u043f \u043e\u0448\u0438\u0431\u043a\u0438 CWE": "CWE-79",
  "\u0423\u0440\u043e\u0432\u0435\u043d\u044c \u043e\u043f\u0430\u0441\u043d\u043e\u0441\u0442\u0438 \u0443\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u0438": "\u0421\u0440\u0435\u0434\u043d\u0438\u0439 \u0443\u0440\u043e\u0432\u0435\u043d\u044c \u043e\u043f\u0430\u0441\u043d\u043e\u0441\u0442\u0438 (\u0431\u0430\u0437\u043e\u0432\u0430\u044f \u043e\u0446\u0435\u043d\u043a\u0430 CVSS 2.0 \u0441\u043e\u0441\u0442\u0430\u0432\u043b\u044f\u0435\u0442 6,5)\n\u0421\u0440\u0435\u0434\u043d\u0438\u0439 \u0443\u0440\u043e\u0432\u0435\u043d\u044c \u043e\u043f\u0430\u0441\u043d\u043e\u0441\u0442\u0438 (\u0431\u0430\u0437\u043e\u0432\u0430\u044f \u043e\u0446\u0435\u043d\u043a\u0430 CVSS 3.0 \u0441\u043e\u0441\u0442\u0430\u0432\u043b\u044f\u0435\u0442 5,5)"
}
FKIE_CVE-2024-27300
Vulnerability from fkie_nvd - Published: 2024-03-25 19:15 - Updated: 2026-06-17 07:195.4 (Medium) - CVSS:3.1/
{
  "affected": [
    {
      "affectedData": [
        {
          "product": "phpMyFAQ",
          "vendor": "thorsten",
          "versions": [
            {
              "status": "affected",
              "version": "3.2.5"
            }
          ]
        }
      ],
      "source": "security-advisories@github.com"
    },
    {
      "affectedData": [
        {
          "cpes": [
            "cpe:2.3:a:thorsten:phpmyfaq:*:*:*:*:*:*:*:*"
          ],
          "defaultStatus": "unknown",
          "product": "phpmyfaq",
          "vendor": "thorsten",
          "versions": [
            {
              "lessThan": "3.2.6",
              "status": "affected",
              "version": "0",
              "versionType": "custom"
            }
          ]
        }
      ],
      "source": "134c704f-9b21-4f2e-91b3-4a467353bcc0"
    }
  ],
  "configurations": [
    {
      "nodes": [
        {
          "cpeMatch": [
            {
              "criteria": "cpe:2.3:a:phpmyfaq:phpmyfaq:3.2.5:*:*:*:*:*:*:*",
              "matchCriteriaId": "99BD7923-9316-46E2-B3C4-33105AD9E901",
              "vulnerable": true
            }
          ],
          "negate": false,
          "operator": "OR"
        }
      ]
    }
  ],
  "cveTags": [],
  "descriptions": [
    {
      "lang": "en",
      "value": "phpMyFAQ is an open source FAQ web application for PHP 8.1+ and MySQL, PostgreSQL and other databases. The `email` field in phpMyFAQ\u0027s user control panel page is vulnerable to stored XSS attacks due to the inadequacy of PHP\u0027s `FILTER_VALIDATE_EMAIL` function, which only validates the email format, not its content. This vulnerability enables an attacker to execute arbitrary client-side JavaScript within the context of another user\u0027s phpMyFAQ session. This vulnerability is fixed in 3.2.6."
    },
    {
      "lang": "es",
      "value": "phpMyFAQ es una aplicaci\u00f3n web de preguntas frecuentes de c\u00f3digo abierto para PHP 8.1+ y MySQL, PostgreSQL y otras bases de datos. El campo `email` en la p\u00e1gina del panel de control de usuario de phpMyFAQ es vulnerable a ataques XSS almacenados debido a la insuficiencia de la funci\u00f3n `FILTER_VALIDATE_EMAIL` de PHP, que solo valida el formato del correo electr\u00f3nico, no su contenido. Esta vulnerabilidad permite a un atacante ejecutar JavaScript arbitrario del lado del cliente dentro del contexto de la sesi\u00f3n phpMyFAQ de otro usuario. Esta vulnerabilidad se soluciona en 3.2.6."
    }
  ],
  "id": "CVE-2024-27300",
  "lastModified": "2026-06-17T07:19:36.197",
  "metrics": {
    "cvssMetricV31": [
      {
        "cvssData": {
          "attackComplexity": "LOW",
          "attackVector": "NETWORK",
          "availabilityImpact": "LOW",
          "baseScore": 5.5,
          "baseSeverity": "MEDIUM",
          "confidentialityImpact": "LOW",
          "integrityImpact": "LOW",
          "privilegesRequired": "LOW",
          "scope": "UNCHANGED",
          "userInteraction": "REQUIRED",
          "vectorString": "CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:U/C:L/I:L/A:L",
          "version": "3.1"
        },
        "exploitabilityScore": 2.1,
        "impactScore": 3.4,
        "source": "security-advisories@github.com",
        "type": "Secondary"
      },
      {
        "cvssData": {
          "attackComplexity": "LOW",
          "attackVector": "NETWORK",
          "availabilityImpact": "NONE",
          "baseScore": 5.4,
          "baseSeverity": "MEDIUM",
          "confidentialityImpact": "LOW",
          "integrityImpact": "LOW",
          "privilegesRequired": "LOW",
          "scope": "CHANGED",
          "userInteraction": "REQUIRED",
          "vectorString": "CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:C/C:L/I:L/A:N",
          "version": "3.1"
        },
        "exploitabilityScore": 2.3,
        "impactScore": 2.7,
        "source": "nvd@nist.gov",
        "type": "Primary"
      }
    ],
    "ssvcV203": [
      {
        "source": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
        "ssvcData": {
          "id": "CVE-2024-27300",
          "options": [
            {
              "exploitation": "poc"
            },
            {
              "automatable": "no"
            },
            {
              "technicalImpact": "partial"
            }
          ],
          "role": "CISA Coordinator",
          "timestamp": "2024-03-25T19:29:59.933358Z",
          "version": "2.0.3"
        }
      }
    ]
  },
  "published": "2024-03-25T19:15:57.807",
  "references": [
    {
      "source": "security-advisories@github.com",
      "tags": [
        "Patch"
      ],
      "url": "https://github.com/thorsten/phpMyFAQ/commit/09336b0ff0e0a04aa0c97c5975651af4769d2459"
    },
    {
      "source": "security-advisories@github.com",
      "tags": [
        "Patch"
      ],
      "url": "https://github.com/thorsten/phpMyFAQ/commit/de90315c9bd4ead5fe6ba5586f6b016843aa8209"
    },
    {
      "source": "security-advisories@github.com",
      "tags": [
        "Exploit",
        "Vendor Advisory"
      ],
      "url": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-q7g6-xfh2-vhpx"
    },
    {
      "source": "af854a3a-2127-422b-91ae-364da2661108",
      "tags": [
        "Patch"
      ],
      "url": "https://github.com/thorsten/phpMyFAQ/commit/09336b0ff0e0a04aa0c97c5975651af4769d2459"
    },
    {
      "source": "af854a3a-2127-422b-91ae-364da2661108",
      "tags": [
        "Patch"
      ],
      "url": "https://github.com/thorsten/phpMyFAQ/commit/de90315c9bd4ead5fe6ba5586f6b016843aa8209"
    },
    {
      "source": "af854a3a-2127-422b-91ae-364da2661108",
      "tags": [
        "Exploit",
        "Vendor Advisory"
      ],
      "url": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-q7g6-xfh2-vhpx"
    }
  ],
  "sourceIdentifier": "security-advisories@github.com",
  "vulnStatus": "Analyzed",
  "weaknesses": [
    {
      "description": [
        {
          "lang": "en",
          "value": "CWE-79"
        }
      ],
      "source": "security-advisories@github.com",
      "type": "Secondary"
    },
    {
      "description": [
        {
          "lang": "en",
          "value": "CWE-79"
        }
      ],
      "source": "nvd@nist.gov",
      "type": "Primary"
    }
  ]
}
GHSA-Q7G6-XFH2-VHPX
Vulnerability from github – Published: 2024-03-25 19:46 – Updated: 2024-03-25 22:28Summary
The email field in phpMyFAQ's user control panel page is vulnerable to stored XSS attacks due to the inadequacy of PHP's FILTER_VALIDATE_EMAIL function, which only validates the email format, not its content. This vulnerability enables an attacker to execute arbitrary client-side JavaScript within the context of another user's phpMyFAQ session.
Details
Despite using PHP's FILTER_VALIDATE_EMAIL function, the email field does not adequately validate the content of the email address. This means that malicious input, such as JavaScript code, can be accepted and stored in the database without being detected. When the stored data is retrieved and displayed on web pages, it is not properly sanitized to remove or neutralize any potentially harmful content, such as JavaScript code which leads to Stored XSS.
PoC
-
Login as any user, go to the user control panel, change email to any valid email and intercept the request.
-
Modify the request’s email parameter to the following payload:
"><svg/onload=confirm('XSS')>"@x.y -
Send the request and see that the XSS is triggered in the user control panel page.
-
Also affects any user who browse to "../admin/?action=user&user_action=listallusers"
Impact
This allows an attacker to execute arbitrary client side JavaScript within the context of another user's phpMyFAQ session.
{
"affected": [
{
"package": {
"ecosystem": "Packagist",
"name": "phpmyfaq/phpmyfaq"
},
"ranges": [
{
"events": [
{
"introduced": "3.2.5"
},
{
"fixed": "3.2.6"
}
],
"type": "ECOSYSTEM"
}
],
"versions": [
"3.2.5"
]
}
],
"aliases": [
"CVE-2024-27300"
],
"database_specific": {
"cwe_ids": [
"CWE-79"
],
"github_reviewed": true,
"github_reviewed_at": "2024-03-25T19:46:28Z",
"nvd_published_at": "2024-03-25T19:15:57Z",
"severity": "MODERATE"
},
"details": "### Summary\nThe `email` field in phpMyFAQ\u0027s user control panel page is vulnerable to stored XSS attacks due to the inadequacy of PHP\u0027s `FILTER_VALIDATE_EMAIL` function, which only validates the email format, not its content. This vulnerability enables an attacker to execute arbitrary client-side JavaScript within the context of another user\u0027s phpMyFAQ session.\n\n### Details\nDespite using PHP\u0027s `FILTER_VALIDATE_EMAIL` function, the email field does not adequately validate the content of the email address. This means that malicious input, such as JavaScript code, can be accepted and stored in the database without being detected. When the stored data is retrieved and displayed on web pages, it is not properly sanitized to remove or neutralize any potentially harmful content, such as JavaScript code which leads to Stored XSS.\n\n### PoC\n1. Login as any user, go to the user control panel, change email to any valid email and intercept the request.\n\n2. Modify the request\u2019s email parameter to the following payload: `\"\u003e\u003csvg/onload=confirm(\u0027XSS\u0027)\u003e\"@x.y`\n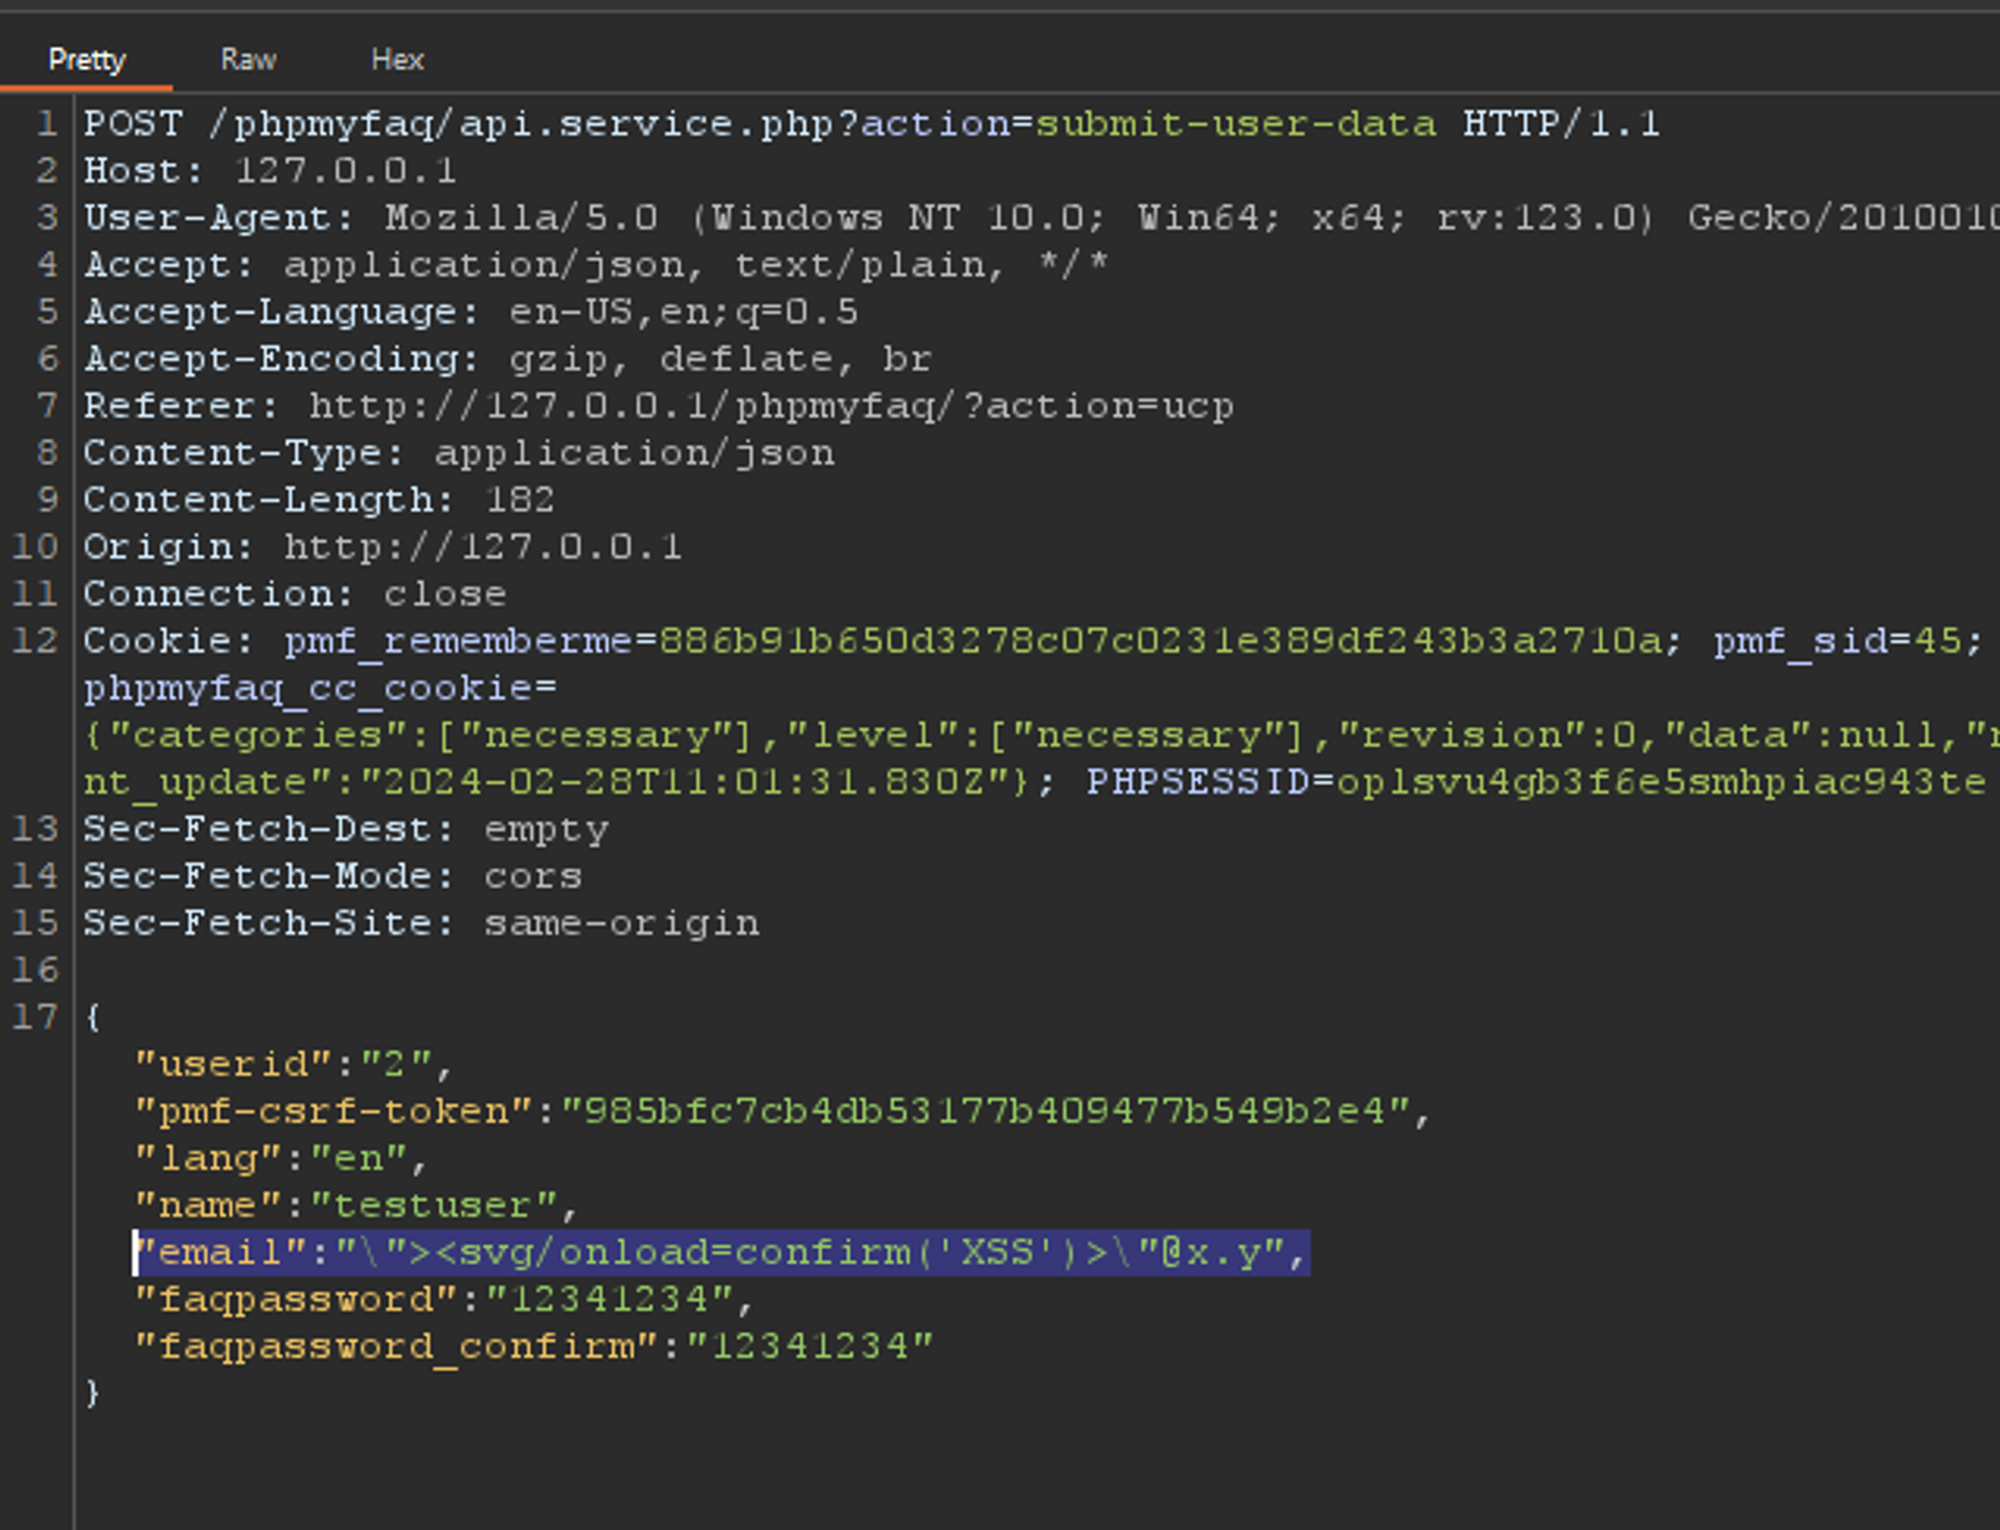\n\n\n3. Send the request and see that the XSS is triggered in the user control panel page.\n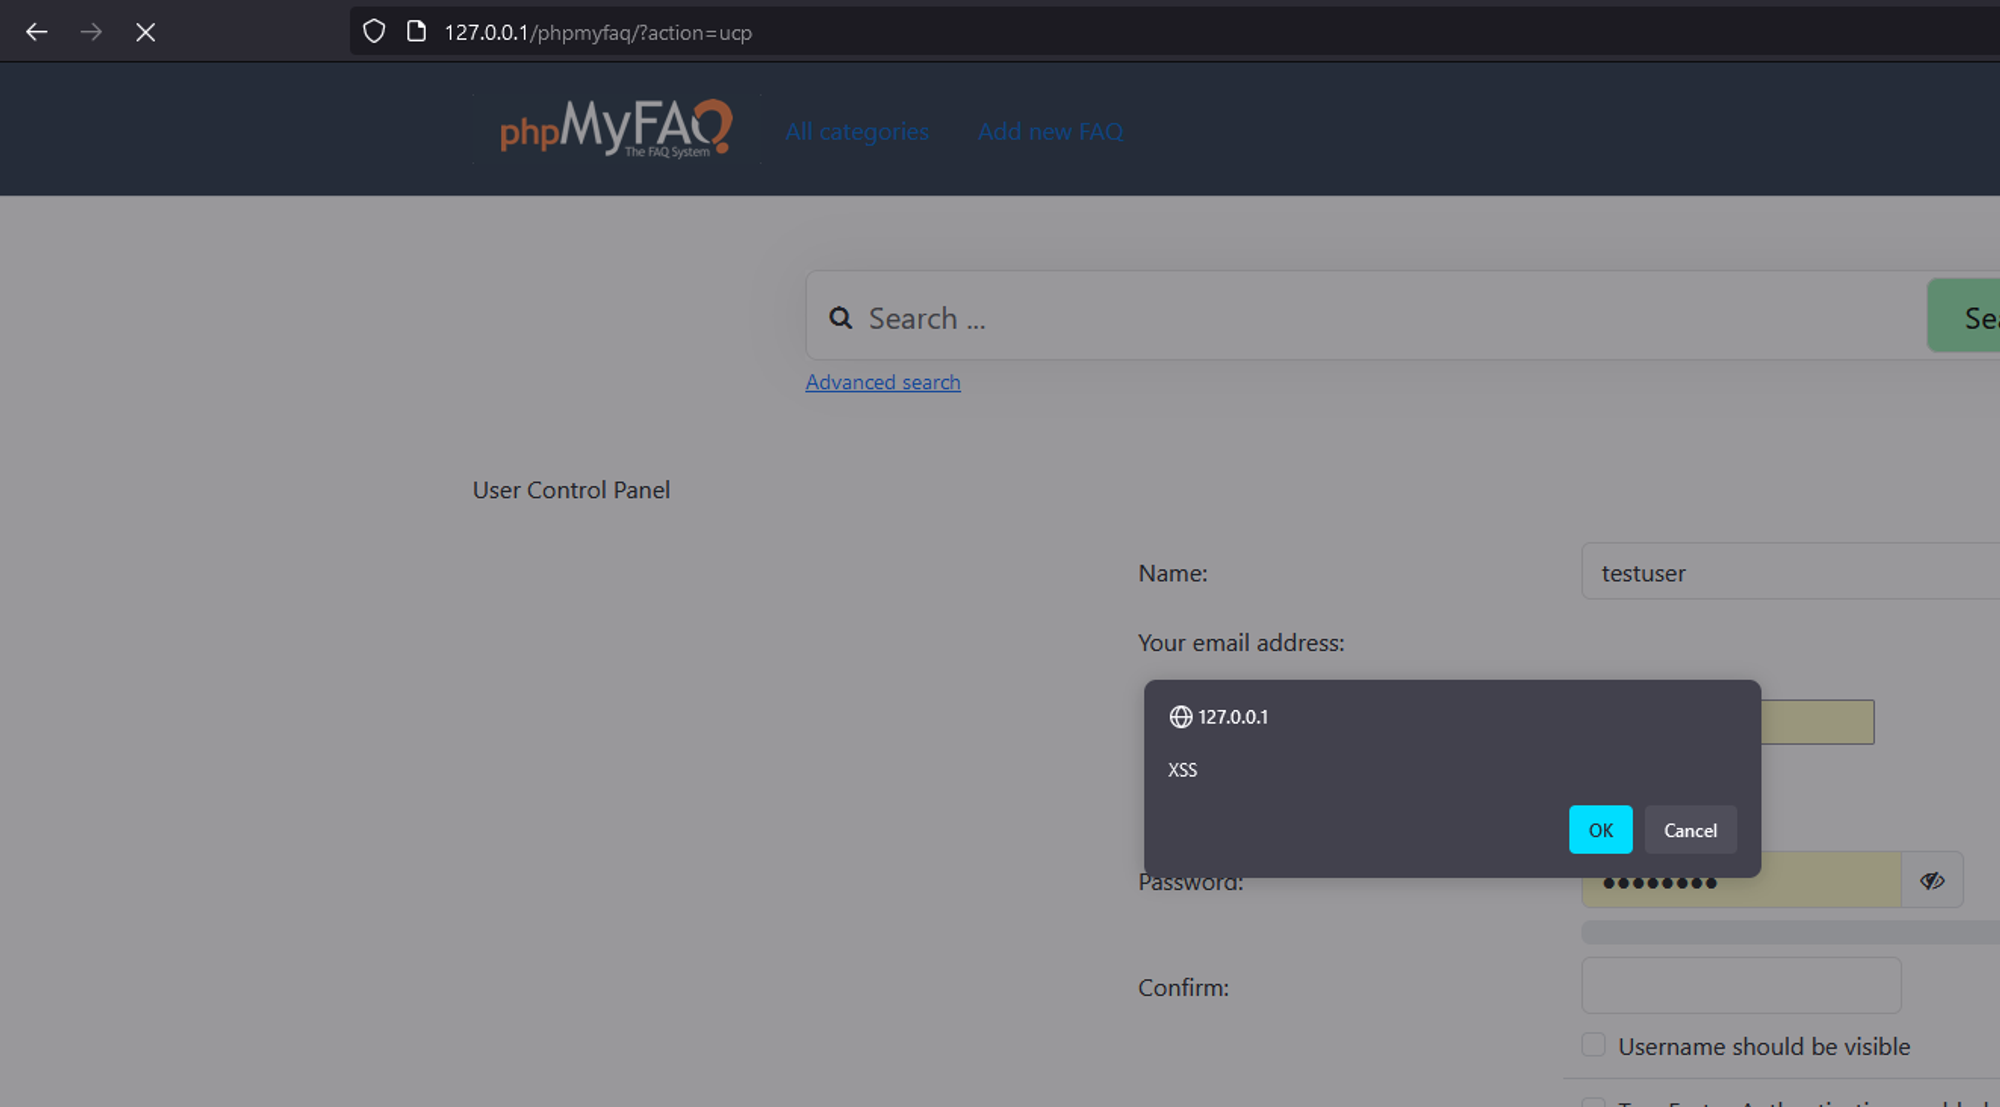\n\n\n4. Also affects any user who browse to \"../admin/?action=user\u0026user_action=listallusers\"\n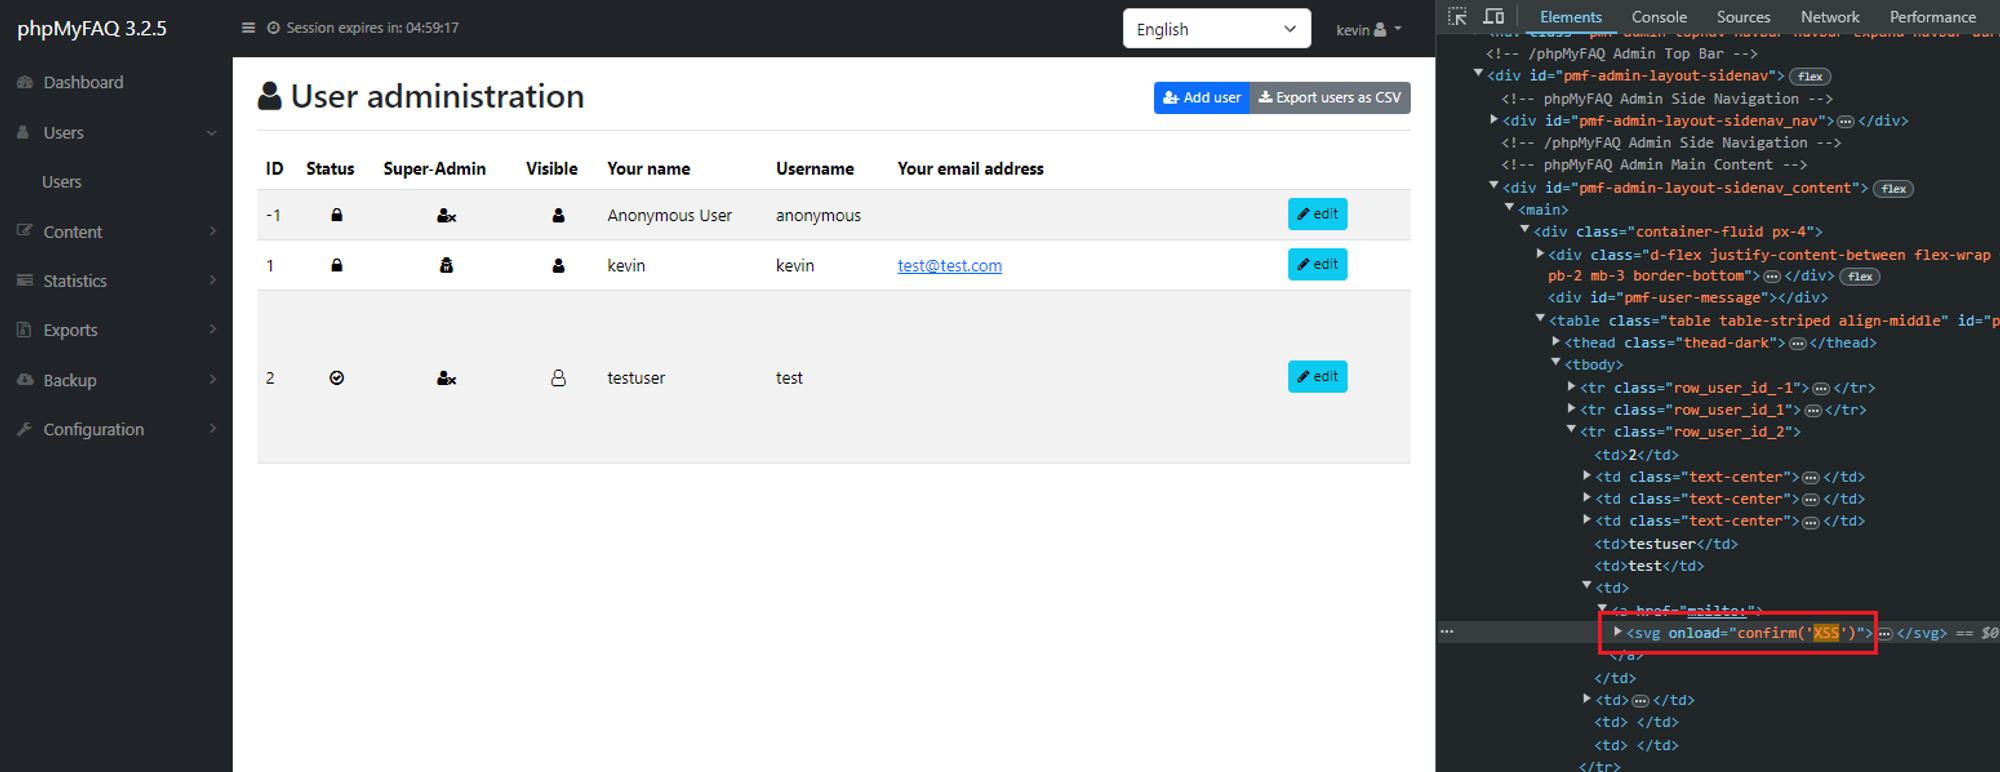\n\n\n### Impact\nThis allows an attacker to execute arbitrary client side JavaScript within the context of another user\u0027s phpMyFAQ session.\n",
"id": "GHSA-q7g6-xfh2-vhpx",
"modified": "2024-03-25T22:28:21Z",
"published": "2024-03-25T19:46:28Z",
"references": [
{
"type": "WEB",
"url": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-q7g6-xfh2-vhpx"
},
{
"type": "ADVISORY",
"url": "https://nvd.nist.gov/vuln/detail/CVE-2024-27300"
},
{
"type": "WEB",
"url": "https://github.com/thorsten/phpMyFAQ/commit/09336b0ff0e0a04aa0c97c5975651af4769d2459"
},
{
"type": "WEB",
"url": "https://github.com/thorsten/phpMyFAQ/commit/de90315c9bd4ead5fe6ba5586f6b016843aa8209"
},
{
"type": "PACKAGE",
"url": "https://github.com/thorsten/phpMyFAQ"
}
],
"schema_version": "1.4.0",
"severity": [
{
"score": "CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:U/C:L/I:L/A:L",
"type": "CVSS_V3"
}
],
"summary": "phpMyFAQ stored Cross-site Scripting at user email"
}
GSD-2024-27300
Vulnerability from gsd - Updated: 2024-02-23 06:03{
"gsd": {
"metadata": {
"exploitCode": "unknown",
"remediation": "unknown",
"reportConfidence": "confirmed",
"type": "vulnerability"
},
"osvSchema": {
"aliases": [
"CVE-2024-27300"
],
"details": "phpMyFAQ is an open source FAQ web application for PHP 8.1+ and MySQL, PostgreSQL and other databases. The `email` field in phpMyFAQ\u0027s user control panel page is vulnerable to stored XSS attacks due to the inadequacy of PHP\u0027s `FILTER_VALIDATE_EMAIL` function, which only validates the email format, not its content. This vulnerability enables an attacker to execute arbitrary client-side JavaScript within the context of another user\u0027s phpMyFAQ session. This vulnerability is fixed in 3.2.6.",
"id": "GSD-2024-27300",
"modified": "2024-02-23T06:03:43.533257Z",
"schema_version": "1.4.0"
}
},
"namespaces": {
"cve.org": {
"CVE_data_meta": {
"ASSIGNER": "security-advisories@github.com",
"ID": "CVE-2024-27300",
"STATE": "PUBLIC"
},
"affects": {
"vendor": {
"vendor_data": [
{
"product": {
"product_data": [
{
"product_name": "phpMyFAQ",
"version": {
"version_data": [
{
"version_affected": "=",
"version_value": "3.2.5"
}
]
}
}
]
},
"vendor_name": "thorsten"
}
]
}
},
"data_format": "MITRE",
"data_type": "CVE",
"data_version": "4.0",
"description": {
"description_data": [
{
"lang": "eng",
"value": "phpMyFAQ is an open source FAQ web application for PHP 8.1+ and MySQL, PostgreSQL and other databases. The `email` field in phpMyFAQ\u0027s user control panel page is vulnerable to stored XSS attacks due to the inadequacy of PHP\u0027s `FILTER_VALIDATE_EMAIL` function, which only validates the email format, not its content. This vulnerability enables an attacker to execute arbitrary client-side JavaScript within the context of another user\u0027s phpMyFAQ session. This vulnerability is fixed in 3.2.6."
}
]
},
"impact": {
"cvss": [
{
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "LOW",
"baseScore": 5.5,
"baseSeverity": "MEDIUM",
"confidentialityImpact": "LOW",
"integrityImpact": "LOW",
"privilegesRequired": "LOW",
"scope": "UNCHANGED",
"userInteraction": "REQUIRED",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:U/C:L/I:L/A:L",
"version": "3.1"
}
]
},
"problemtype": {
"problemtype_data": [
{
"description": [
{
"cweId": "CWE-79",
"lang": "eng",
"value": "CWE-79: Improper Neutralization of Input During Web Page Generation (\u0027Cross-site Scripting\u0027)"
}
]
}
]
},
"references": {
"reference_data": [
{
"name": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-q7g6-xfh2-vhpx",
"refsource": "MISC",
"url": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-q7g6-xfh2-vhpx"
},
{
"name": "https://github.com/thorsten/phpMyFAQ/commit/09336b0ff0e0a04aa0c97c5975651af4769d2459",
"refsource": "MISC",
"url": "https://github.com/thorsten/phpMyFAQ/commit/09336b0ff0e0a04aa0c97c5975651af4769d2459"
},
{
"name": "https://github.com/thorsten/phpMyFAQ/commit/de90315c9bd4ead5fe6ba5586f6b016843aa8209",
"refsource": "MISC",
"url": "https://github.com/thorsten/phpMyFAQ/commit/de90315c9bd4ead5fe6ba5586f6b016843aa8209"
}
]
},
"source": {
"advisory": "GHSA-q7g6-xfh2-vhpx",
"discovery": "UNKNOWN"
}
},
"nvd.nist.gov": {
"cve": {
"descriptions": [
{
"lang": "en",
"value": "phpMyFAQ is an open source FAQ web application for PHP 8.1+ and MySQL, PostgreSQL and other databases. The `email` field in phpMyFAQ\u0027s user control panel page is vulnerable to stored XSS attacks due to the inadequacy of PHP\u0027s `FILTER_VALIDATE_EMAIL` function, which only validates the email format, not its content. This vulnerability enables an attacker to execute arbitrary client-side JavaScript within the context of another user\u0027s phpMyFAQ session. This vulnerability is fixed in 3.2.6."
},
{
"lang": "es",
"value": "phpMyFAQ es una aplicaci\u00f3n web de preguntas frecuentes de c\u00f3digo abierto para PHP 8.1+ y MySQL, PostgreSQL y otras bases de datos. El campo `email` en la p\u00e1gina del panel de control de usuario de phpMyFAQ es vulnerable a ataques XSS almacenados debido a la insuficiencia de la funci\u00f3n `FILTER_VALIDATE_EMAIL` de PHP, que solo valida el formato del correo electr\u00f3nico, no su contenido. Esta vulnerabilidad permite a un atacante ejecutar JavaScript arbitrario del lado del cliente dentro del contexto de la sesi\u00f3n phpMyFAQ de otro usuario. Esta vulnerabilidad se soluciona en 3.2.6."
}
],
"id": "CVE-2024-27300",
"lastModified": "2024-03-26T12:55:05.010",
"metrics": {
"cvssMetricV31": [
{
"cvssData": {
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "LOW",
"baseScore": 5.5,
"baseSeverity": "MEDIUM",
"confidentialityImpact": "LOW",
"integrityImpact": "LOW",
"privilegesRequired": "LOW",
"scope": "UNCHANGED",
"userInteraction": "REQUIRED",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:U/C:L/I:L/A:L",
"version": "3.1"
},
"exploitabilityScore": 2.1,
"impactScore": 3.4,
"source": "security-advisories@github.com",
"type": "Secondary"
}
]
},
"published": "2024-03-25T19:15:57.807",
"references": [
{
"source": "security-advisories@github.com",
"url": "https://github.com/thorsten/phpMyFAQ/commit/09336b0ff0e0a04aa0c97c5975651af4769d2459"
},
{
"source": "security-advisories@github.com",
"url": "https://github.com/thorsten/phpMyFAQ/commit/de90315c9bd4ead5fe6ba5586f6b016843aa8209"
},
{
"source": "security-advisories@github.com",
"url": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-q7g6-xfh2-vhpx"
}
],
"sourceIdentifier": "security-advisories@github.com",
"vulnStatus": "Awaiting Analysis",
"weaknesses": [
{
"description": [
{
"lang": "en",
"value": "CWE-79"
}
],
"source": "security-advisories@github.com",
"type": "Secondary"
}
]
}
}
}
}
Drag nodes to arrange them. Double-click a related vulnerability to open it, or a source to visit its link. The Physics button on the left tunes the layout and the simulation; the legend at the bottom left hides or shows nodes by kind and by sighting type.
Sightings
| Author | Source | Type | Date | Other |
|---|
Nomenclature
- Seen: The vulnerability was mentioned, discussed, or observed by the user.
- Confirmed: The vulnerability has been validated from an analyst's perspective.
- Published Proof of Concept: A public proof of concept is available for this vulnerability.
- Exploited: The vulnerability was observed as exploited by the user who reported the sighting.
- Patched: The vulnerability was observed as successfully patched by the user who reported the sighting.
- Not exploited: The vulnerability was not observed as exploited by the user who reported the sighting.
- Not confirmed: The user expressed doubt about the validity of the vulnerability.
- Not patched: The vulnerability was not observed as successfully patched by the user who reported the sighting.
Vulnerability timeline
Sightings and recorded dates, grouped by day · UTC
Loading timeline…

The approach is described in our paper Mapping CVEs to MITRE ATT&CK Techniques: A Curated Gold-Set Classifier and the Limits of LLM-Assisted Label Expansion.
Browse all ATT&CK techniques and the vulnerabilities related to each.
Related by attack behaviour
Vulnerabilities whose description is nearest to this one in the vector space of the CIRCL/vulnerability-attack-technique-biencoder model. This is a similarity search over the bi-encoder space (plain cosine), not a classification, and it has no measured accuracy.