CWE-862
Weakness Allowed-with-ReviewMissing Authorization
Abstraction: Class · Status: Incomplete
The product does not perform an authorization check when an actor attempts to access a resource or perform an action.
Dimensions
- Behavior-Property: Missing
- Behavior-Type: Authorization
Mapping guidance
This CWE entry is a Class and might have Base-level children that would be more appropriate
Examine children of this entry to see if there is a better fit
Relationships and members
Modes of introduction
OMISSION: This weakness is caused by missing a security tactic during the architecture and design phase.
Authorization weaknesses may arise when a single-user application is ported to a multi-user environment.
A developer may introduce authorization weaknesses because of a lack of understanding about the underlying technologies. For example, a developer may assume that attackers cannot modify certain inputs such as headers or cookies.
Detection methods
Automated Static Analysis
Automated static analysis is useful for detecting commonly-used idioms for authorization. A tool may be able to analyze related configuration files, such as .htaccess in Apache web servers, or detect the usage of commonly-used authorization libraries.
Generally, automated static analysis tools have difficulty detecting custom authorization schemes. In addition, the software's design may include some functionality that is accessible to any user and does not require an authorization check; an automated technique that detects the absence of authorization may report false positives.
Effectiveness: Limited
Automated Dynamic Analysis
Automated dynamic analysis may find many or all possible interfaces that do not require authorization, but manual analysis is required to determine if the lack of authorization violates business logic.
Manual Analysis
This weakness can be detected using tools and techniques that require manual (human) analysis, such as penetration testing, threat modeling, and interactive tools that allow the tester to record and modify an active session.
Specifically, manual static analysis is useful for evaluating the correctness of custom authorization mechanisms.
Effectiveness: Moderate
These may be more effective than strictly automated techniques. This is especially the case with weaknesses that are related to design and business rules. However, manual efforts might not achieve desired code coverage within limited time constraints.
Manual Static Analysis - Binary or Bytecode
According to SOAR [REF-1479], the following detection techniques may be useful:
Cost effective for partial coverage:
Binary / Bytecode disassembler - then use manual analysis for vulnerabilities & anomalies
Effectiveness: SOAR Partial
Dynamic Analysis with Automated Results Interpretation
According to SOAR [REF-1479], the following detection techniques may be useful:
Cost effective for partial coverage:
Web Application Scanner
Web Services Scanner
Database Scanners
Effectiveness: SOAR Partial
Dynamic Analysis with Manual Results Interpretation
According to SOAR [REF-1479], the following detection techniques may be useful:
Cost effective for partial coverage:
Host Application Interface Scanner
Fuzz Tester
Framework-based Fuzzer
Effectiveness: SOAR Partial
Manual Static Analysis - Source Code
According to SOAR [REF-1479], the following detection techniques may be useful:
Cost effective for partial coverage:
Focused Manual Spotcheck - Focused manual analysis of source
Manual Source Code Review (not inspections)
Effectiveness: SOAR Partial
Automated Static Analysis - Source Code
According to SOAR [REF-1479], the following detection techniques may be useful:
Cost effective for partial coverage:
Source code Weakness Analyzer
Context-configured Source Code Weakness Analyzer
Effectiveness: SOAR Partial
Architecture or Design Review
According to SOAR [REF-1479], the following detection techniques may be useful:
Highly cost effective:
Inspection (IEEE 1028 standard) (can apply to requirements, design, source code, etc.)
Formal Methods / Correct-By-Construction
Effectiveness: High
Notes
Terminology
Assuming a user with a given identity, authorization is the process of determining whether that user can access a given resource, based on the user's privileges and any permissions or other access-control specifications that apply to the resource.
Content history
Suggested mappings to ISA/IEC 62443.
Provided diagram to improve CWE usability
updated Demonstrative_Examples, Related_Attack_Patterns, Relationships
updated Potential_Mitigations, References, Relationships
updated Demonstrative_Examples, Observed_Examples, References, Relationships
updated Potential_Mitigations
updated Relationships
updated Detection_Factors
updated Relationships
updated Applicable_Platforms, Modes_of_Introduction, References, Relationships
updated References
updated Relationships
updated Relationships
updated Relationships
updated Relationships
updated Alternate_Terms, Observed_Examples
updated Observed_Examples, Related_Attack_Patterns, Relationships
updated Relationships
updated Relationships
updated Observed_Examples
updated Description, Potential_Mitigations
updated References, Relationships, Taxonomy_Mappings
updated Mapping_Notes, Relationships, Taxonomy_Mappings
updated Common_Consequences, Description, Diagram, Relationships, Terminology_Notes
updated Applicable_Platforms, Detection_Factors, Observed_Examples, References
updated Applicable_Platforms, Relationships, Weakness_Ordinalities
updated Applicable_Platforms, Observed_Examples, Relationships
updated Applicable_Platforms, Dimensions, References, Relationships, Taxonomy_Mappings
19869 vulnerabilities reference this CWE, most recent first.
GHSA-94RC-H54C-MC7X
Vulnerability from github – Published: 2024-10-10 03:30 – Updated: 2026-04-08 21:32The Youzify – BuddyPress Community, User Profile, Social Network & Membership Plugin for WordPress plugin for WordPress is vulnerable to unauthorized modification of data due to a missing capability check on the 'delete_attachment' function in all versions up to, and including, 1.3.0. This makes it possible for authenticated attackers, with Subscriber-level access and above, to delete arbitrary attachments.
{
  "affected": [],
  "aliases": [
    "CVE-2024-9067"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-862"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2024-10-10T03:15:02Z",
    "severity": "MODERATE"
  },
  "details": "The Youzify \u2013 BuddyPress Community, User Profile, Social Network \u0026 Membership Plugin for WordPress plugin for WordPress is vulnerable to unauthorized modification of data due to a missing capability check on the \u0027delete_attachment\u0027 function in all versions up to, and including, 1.3.0. This makes it possible for authenticated attackers, with Subscriber-level access and above, to delete arbitrary attachments.",
  "id": "GHSA-94rc-h54c-mc7x",
  "modified": "2026-04-08T21:32:54Z",
  "published": "2024-10-10T03:30:46Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2024-9067"
    },
    {
      "type": "WEB",
      "url": "https://plugins.trac.wordpress.org/browser/youzify/tags/1.3.0/includes/public/core/class-youzify-attachments.php#L1183"
    },
    {
      "type": "WEB",
      "url": "https://plugins.trac.wordpress.org/browser/youzify/trunk/includes/public/core/class-youzify-attachments.php#L1183"
    },
    {
      "type": "WEB",
      "url": "https://plugins.trac.wordpress.org/changeset?sfp_email=\u0026sfph_mail=\u0026reponame=\u0026old=3166404%40youzify\u0026new=3166404%40youzify\u0026sfp_email=\u0026sfph_mail=#file885"
    },
    {
      "type": "WEB",
      "url": "https://www.wordfence.com/threat-intel/vulnerabilities/id/e099d8e2-6305-43fc-8807-a37791deb2ff?source=cve"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:N/I:L/A:N",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-94RC-XHF4-73HJ
Vulnerability from github – Published: 2025-01-27 15:30 – Updated: 2026-04-01 18:33Missing Authorization vulnerability in Rometheme RomethemeKit For Elementor. This issue affects RomethemeKit For Elementor: from n/a through 1.5.2.
{
  "affected": [],
  "aliases": [
    "CVE-2025-24743"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-862"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2025-01-27T15:15:16Z",
    "severity": "MODERATE"
  },
  "details": "Missing Authorization vulnerability in Rometheme RomethemeKit For Elementor. This issue affects RomethemeKit For Elementor: from n/a through 1.5.2.",
  "id": "GHSA-94rc-xhf4-73hj",
  "modified": "2026-04-01T18:33:30Z",
  "published": "2025-01-27T15:30:58Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2025-24743"
    },
    {
      "type": "WEB",
      "url": "https://patchstack.com/database/wordpress/plugin/rometheme-for-elementor/vulnerability/wordpress-romethemekit-for-elementor-plugin-1-5-2-broken-access-control-vulnerability?_s_id=cve"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:N/I:L/A:N",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-94VP-RMQV-5875
Vulnerability from github – Published: 2020-11-23 19:48 – Updated: 2021-11-19 13:42Impact
An authenticated backend user with the cms.manage_pages, cms.manage_layouts, or cms.manage_partials permissions who would normally not be permitted to provide PHP code to be executed by the CMS due to cms.enableSafeMode being enabled is able to write specific Twig code to escape the Twig sandbox and execute arbitrary PHP.
This is not a problem for anyone that trusts their users with those permissions to normally write & manage PHP within the CMS by not having cms.enableSafeMode enabled, but would be a problem for anyone relying on cms.enableSafeMode to ensure that users with those permissions in production do not have access to write & execute arbitrary PHP.
Patches
Issue has been patched in Build 469 (v1.0.469) and v1.1.0.
Workarounds
Apply https://github.com/octobercms/october/compare/106daa2930de4cebb18732732d47d4056f01dd5b...7cb148c1677373ac30ccfd3069d18098e403e1ca to your installation manually if unable to upgrade to Build 469.
References
Reported by ka1n4t
For more information
If you have any questions or comments about this advisory: * Email us at hello@octobercms.com
Threat assessment:
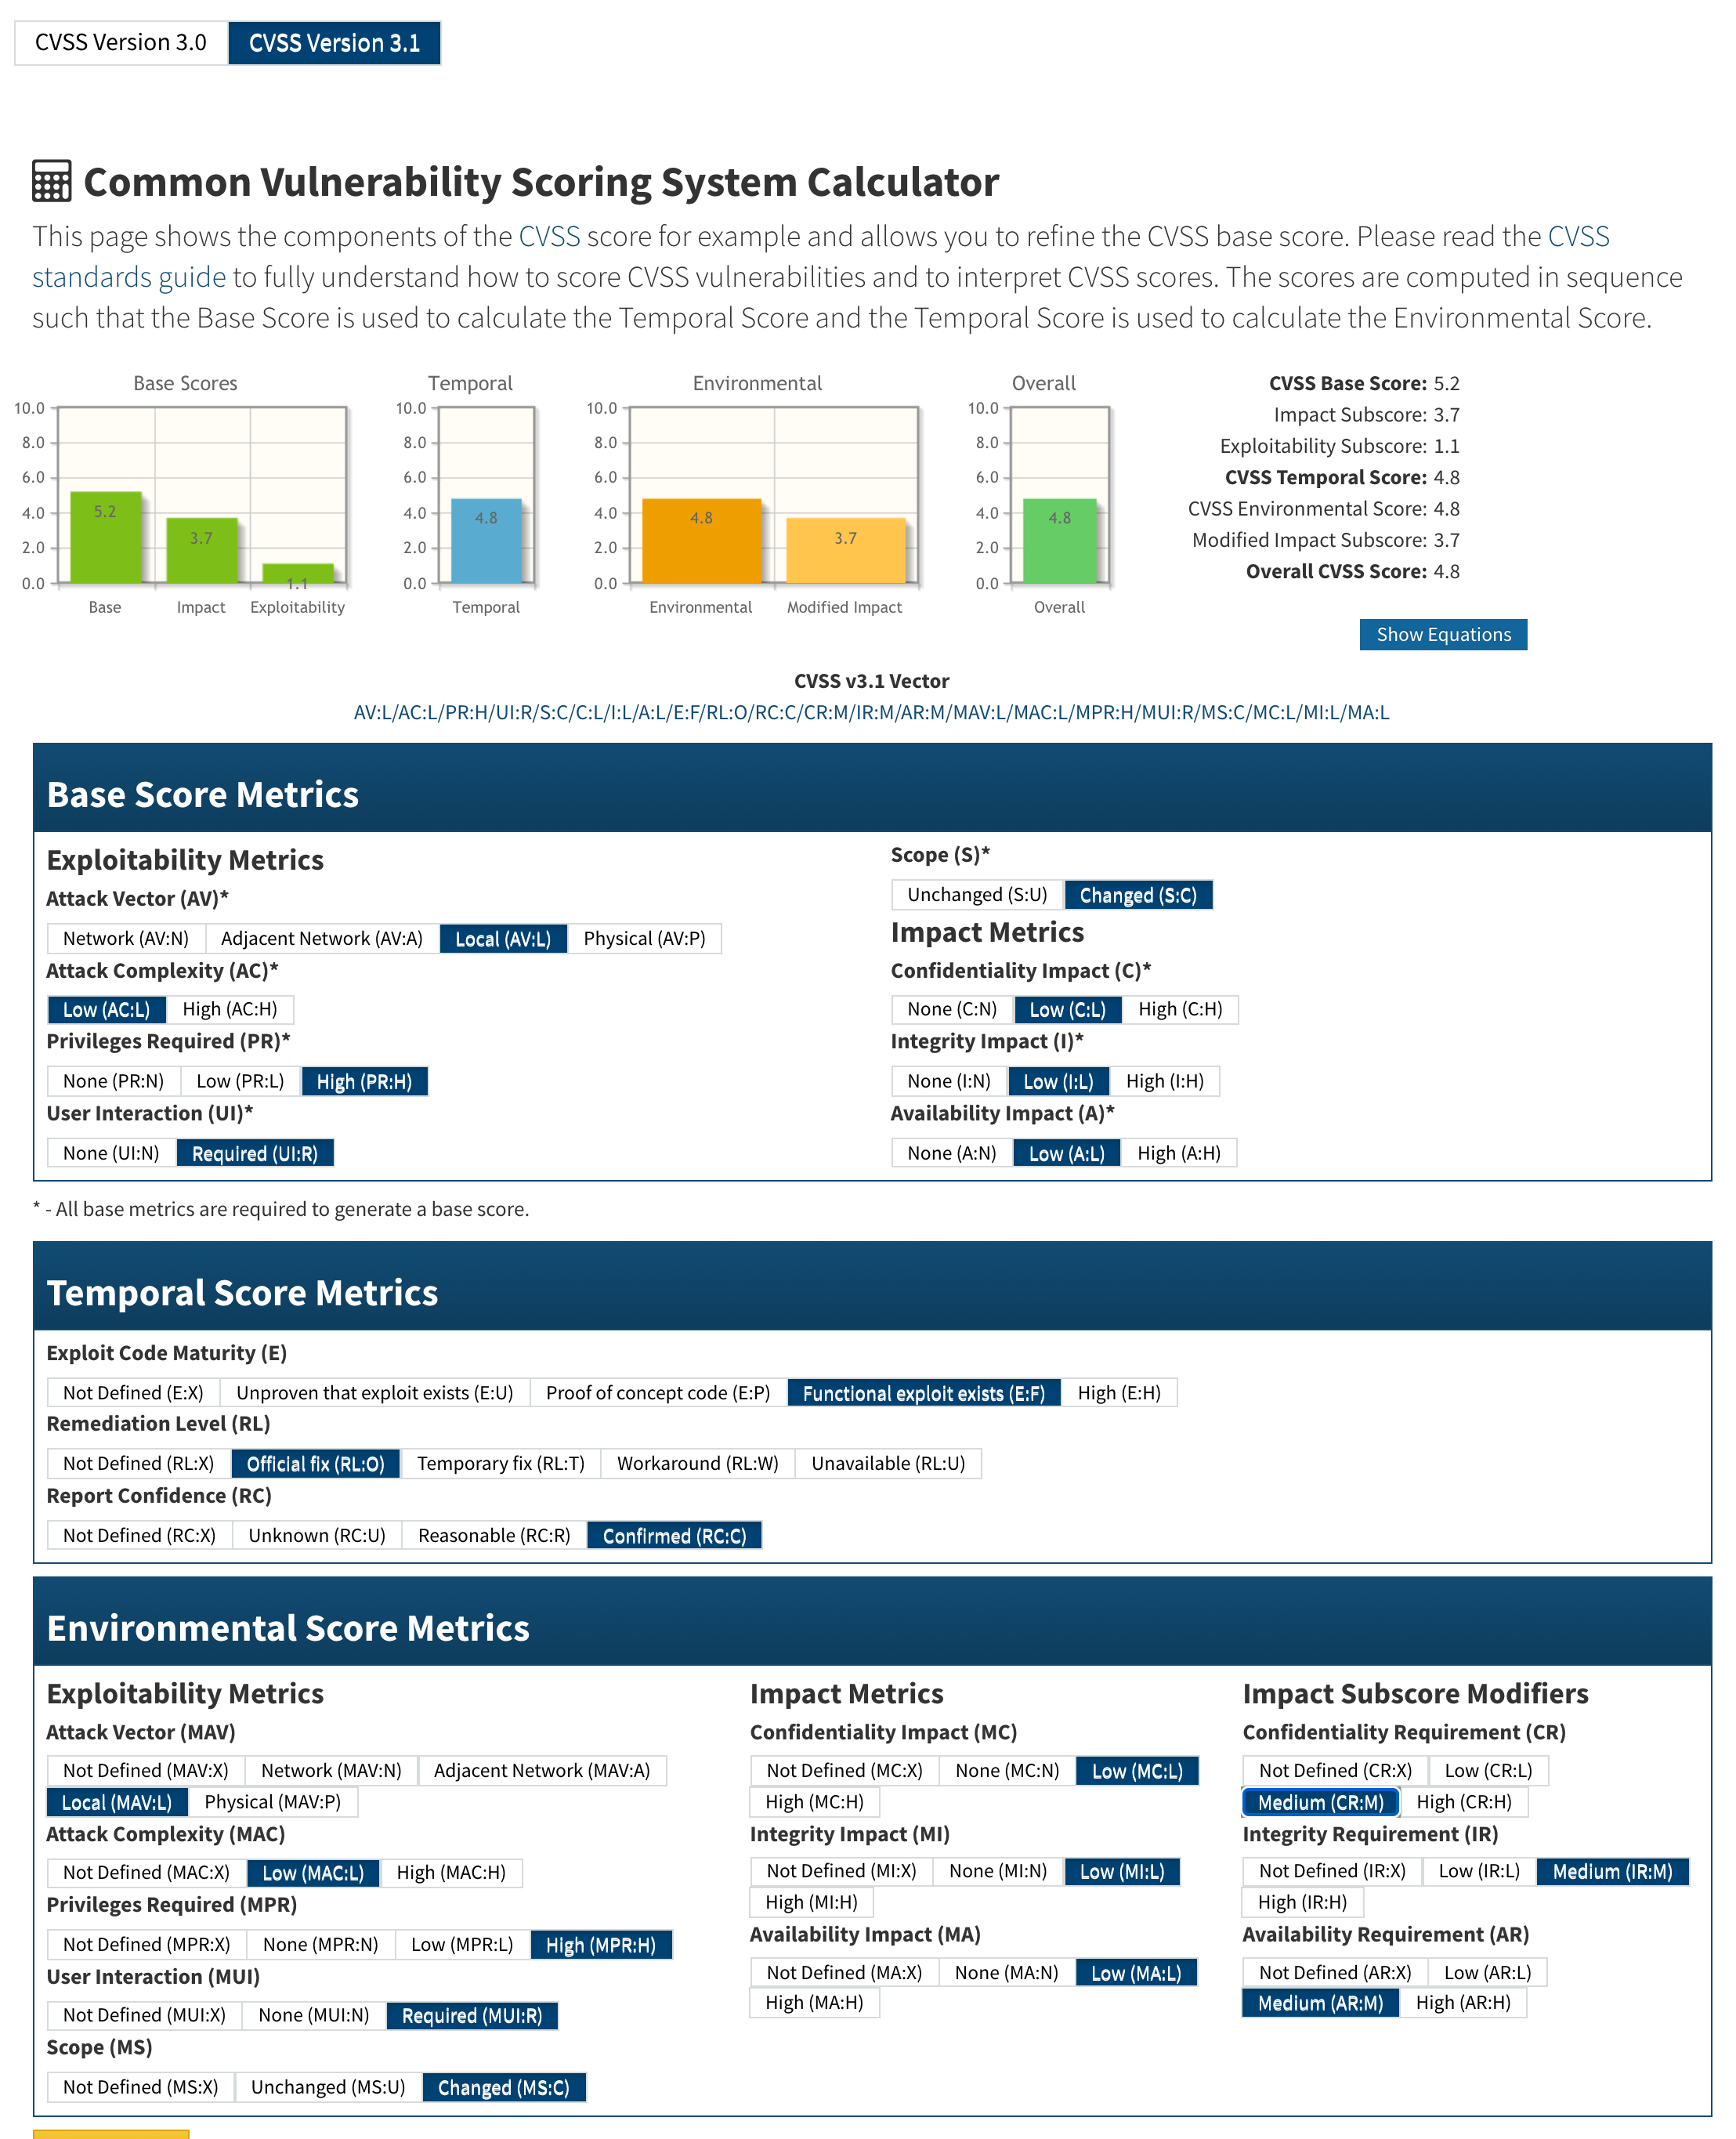
{
  "affected": [
    {
      "package": {
        "ecosystem": "Packagist",
        "name": "october/cms"
      },
      "ranges": [
        {
          "events": [
            {
              "introduced": "1.0.319"
            },
            {
              "fixed": "1.0.469"
            }
          ],
          "type": "ECOSYSTEM"
        }
      ]
    }
  ],
  "aliases": [
    "CVE-2020-15247"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-862"
    ],
    "github_reviewed": true,
    "github_reviewed_at": "2020-11-23T19:33:21Z",
    "nvd_published_at": "2020-11-23T20:15:00Z",
    "severity": "MODERATE"
  },
  "details": "### Impact\nAn authenticated backend user with the `cms.manage_pages`, `cms.manage_layouts`, or `cms.manage_partials` permissions who would **normally** not be permitted to provide PHP code to be executed by the CMS due to `cms.enableSafeMode` being enabled is able to write specific Twig code to escape the Twig sandbox and execute arbitrary PHP.\n\nThis is not a problem for anyone that trusts their users with those permissions to normally write \u0026 manage PHP within the CMS by not having `cms.enableSafeMode` enabled, but would be a problem for anyone relying on `cms.enableSafeMode` to ensure that users with those permissions in production do not have access to write \u0026 execute arbitrary PHP.\n\n### Patches\nIssue has been patched in Build 469 (v1.0.469) and v1.1.0.\n\n### Workarounds\nApply https://github.com/octobercms/october/compare/106daa2930de4cebb18732732d47d4056f01dd5b...7cb148c1677373ac30ccfd3069d18098e403e1ca to your installation manually if unable to upgrade to Build 469.\n\n### References\nReported by [ka1n4t](https://github.com/ka1n4t)\n\n### For more information\nIf you have any questions or comments about this advisory:\n* Email us at [hello@octobercms.com](mailto:hello@octobercms.com)\n\n### Threat assessment:\n\u003cimg width=\"1108\" alt=\"Screen Shot 2020-10-10 at 1 21 13 PM\" src=\"https://user-images.githubusercontent.com/7253840/95663316-7de28b80-0afb-11eb-999d-a6526cf78709.png\"\u003e",
  "id": "GHSA-94vp-rmqv-5875",
  "modified": "2021-11-19T13:42:37Z",
  "published": "2020-11-23T19:48:27Z",
  "references": [
    {
      "type": "WEB",
      "url": "https://github.com/octobercms/october/security/advisories/GHSA-94vp-rmqv-5875"
    },
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2020-15247"
    },
    {
      "type": "WEB",
      "url": "https://github.com/octobercms/october/commit/4c650bb775ab849e48202a4923bac93bd74f9982"
    },
    {
      "type": "PACKAGE",
      "url": "https://github.com/octobercms/october"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:L/AC:L/PR:H/UI:R/S:C/C:L/I:L/A:L",
      "type": "CVSS_V3"
    }
  ],
  "summary": "Twig Sandbox Escape by authenticated users with access to editing CMS templates when safemode is enabled."
}
GHSA-94W8-WHR9-9MV3
Vulnerability from github – Published: 2026-09-23 21:30 – Updated: 2026-09-23 21:30Unauthenticated Broken Access Control in WP User Manager <= 2.9.19 versions.
{
  "affected": [],
  "aliases": [
    "CVE-2026-94079"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-862"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2026-09-23T19:19:47Z",
    "severity": "MODERATE"
  },
  "details": "Unauthenticated Broken Access Control in WP User Manager \u003c= 2.9.19 versions.",
  "id": "GHSA-94w8-whr9-9mv3",
  "modified": "2026-09-23T21:30:45Z",
  "published": "2026-09-23T21:30:45Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2026-94079"
    },
    {
      "type": "WEB",
      "url": "https://patchstack.com/database/wordpress/plugin/wp-user-manager/vulnerability/wordpress-wp-user-manager-plugin-2-9-19-broken-access-control-vulnerability?_s_id=cve"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:L/A:N",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-94X4-66R8-CQX9
Vulnerability from github – Published: 2026-06-27 06:30 – Updated: 2026-06-27 06:30The NEX-Forms – Ultimate Forms Plugin for WordPress plugin for WordPress is vulnerable to authorization bypass in all versions up to, and including, 9.2.2. This is due to the plugin not properly verifying that a user is authorized to perform an action. This makes it possible for unauthenticated attackers to enumerate sequential report IDs and download complete form submission data — including names, email addresses, phone numbers, postal addresses, payment details, and uploaded file paths — for any saved report on the site.
{
  "affected": [],
  "aliases": [
    "CVE-2026-12404"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-862"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2026-06-27T06:16:31Z",
    "severity": "MODERATE"
  },
  "details": "The NEX-Forms \u2013 Ultimate Forms Plugin for WordPress plugin for WordPress is vulnerable to authorization bypass in all versions up to, and including, 9.2.2. This is due to the plugin not properly verifying that a user is authorized to perform an action. This makes it possible for unauthenticated attackers to enumerate sequential report IDs and download complete form submission data \u2014 including names, email addresses, phone numbers, postal addresses, payment details, and uploaded file paths \u2014 for any saved report on the site.",
  "id": "GHSA-94x4-66r8-cqx9",
  "modified": "2026-06-27T06:30:27Z",
  "published": "2026-06-27T06:30:27Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2026-12404"
    },
    {
      "type": "WEB",
      "url": "https://plugins.trac.wordpress.org/browser/nex-forms-express-wp-form-builder/tags/9.1.12/main.php#L3648"
    },
    {
      "type": "WEB",
      "url": "https://plugins.trac.wordpress.org/browser/nex-forms-express-wp-form-builder/tags/9.1.12/main.php#L3654"
    },
    {
      "type": "WEB",
      "url": "https://plugins.trac.wordpress.org/browser/nex-forms-express-wp-form-builder/tags/9.1.12/main.php#L3792"
    },
    {
      "type": "WEB",
      "url": "https://plugins.trac.wordpress.org/browser/nex-forms-express-wp-form-builder/tags/9.2.2/main.php#L3648"
    },
    {
      "type": "WEB",
      "url": "https://plugins.trac.wordpress.org/browser/nex-forms-express-wp-form-builder/tags/9.2.2/main.php#L3654"
    },
    {
      "type": "WEB",
      "url": "https://plugins.trac.wordpress.org/browser/nex-forms-express-wp-form-builder/tags/9.2.2/main.php#L3792"
    },
    {
      "type": "WEB",
      "url": "https://plugins.trac.wordpress.org/changeset?sfp_email=\u0026sfph_mail=\u0026reponame=\u0026old=3584399%40nex-forms-express-wp-form-builder\u0026new=3584399%40nex-forms-express-wp-form-builder\u0026sfp_email=\u0026sfph_mail="
    },
    {
      "type": "WEB",
      "url": "https://www.wordfence.com/threat-intel/vulnerabilities/id/ecf39f38-a476-47a8-a632-986b851895a6?source=cve"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:N/A:N",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-953R-R7WF-54G9
Vulnerability from github – Published: 2026-08-02 06:30 – Updated: 2026-08-03 18:30The Product Attachment for WooCommerce WordPress plugin before 2.3.3 does not perform any authorization check before streaming media library files, allowing unauthenticated users to download any attachment — including private or unlinked uploads — by enumerating its numeric ID.
{
  "affected": [],
  "aliases": [
    "CVE-2026-16285"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-862"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2026-08-02T06:16:40Z",
    "severity": "HIGH"
  },
  "details": "The Product Attachment for WooCommerce WordPress plugin before 2.3.3 does not perform any authorization check before streaming media library files, allowing unauthenticated users to download any attachment \u2014 including private or unlinked uploads \u2014 by enumerating its numeric ID.",
  "id": "GHSA-953r-r7wf-54g9",
  "modified": "2026-08-03T18:30:41Z",
  "published": "2026-08-02T06:30:22Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2026-16285"
    },
    {
      "type": "WEB",
      "url": "https://wpscan.com/vulnerability/99a3a0a4-0e82-4388-88b2-72bd822904b5"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:N",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-9557-2MPW-2VH8
Vulnerability from github – Published: 2026-09-09 03:30 – Updated: 2026-09-09 15:35Missing authorization in Contacts in Google Chrome prior to 153.0.8010.36 allowed a remote attacker who had compromised the renderer process and leveraged social engineering to potentially obtain sensitive information via a crafted HTML page. (Chromium security severity: Low)
{
  "affected": [],
  "aliases": [
    "CVE-2026-87605"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-862"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2026-09-09T01:17:18Z",
    "severity": "MODERATE"
  },
  "details": "Missing authorization in Contacts in Google Chrome prior to 153.0.8010.36 allowed a remote attacker who had compromised the renderer process and leveraged social engineering to potentially obtain sensitive information via a crafted HTML page. (Chromium security severity: Low)",
  "id": "GHSA-9557-2mpw-2vh8",
  "modified": "2026-09-09T15:35:02Z",
  "published": "2026-09-09T03:30:44Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2026-87605"
    },
    {
      "type": "WEB",
      "url": "https://chromereleases.googleblog.com/2026/09/stable-channel-update-for-desktop_0808145027.html"
    },
    {
      "type": "WEB",
      "url": "https://issues.chromium.org/issues/533084499"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:H/PR:N/UI:R/S:U/C:H/I:N/A:N",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-9559-P8WG-Q54V
Vulnerability from github – Published: 2026-01-07 12:31 – Updated: 2026-01-07 12:31The Moosend Landing Pages plugin for WordPress is vulnerable to unauthorized modification of data due to a missing capability check on the moosend_landings_auth_get function in all versions up to, and including, 1.1.6. This makes it possible for authenticated attackers, with Subscriber-level access and above, to delete the 'moosend_landing_api_key' option value.
{
  "affected": [],
  "aliases": [
    "CVE-2025-13496"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-862"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2026-01-07T12:16:48Z",
    "severity": "MODERATE"
  },
  "details": "The Moosend Landing Pages plugin for WordPress is vulnerable to unauthorized modification of data due to a missing capability check on the moosend_landings_auth_get function in all versions up to, and including, 1.1.6. This makes it possible for authenticated attackers, with Subscriber-level access and above, to delete the \u0027moosend_landing_api_key\u0027 option value.",
  "id": "GHSA-9559-p8wg-q54v",
  "modified": "2026-01-07T12:31:20Z",
  "published": "2026-01-07T12:31:20Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2025-13496"
    },
    {
      "type": "WEB",
      "url": "https://plugins.trac.wordpress.org/browser/moosend-landing-pages/tags/1.1.6/forms/auth-request.php#L7"
    },
    {
      "type": "WEB",
      "url": "https://plugins.trac.wordpress.org/browser/moosend-landing-pages/trunk/forms/auth-request.php#L7"
    },
    {
      "type": "WEB",
      "url": "https://www.wordfence.com/threat-intel/vulnerabilities/id/eeb4b3b1-47ae-4314-a386-832949456f81?source=cve"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:L/A:N",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-955J-RV6C-VGF9
Vulnerability from github – Published: 2023-12-04 03:30 – Updated: 2023-12-07 15:30In firewall service, there is a possible way to write permission usage records of an app due to a missing permission check. This could lead to local information disclosure with no additional execution privileges needed
{
  "affected": [],
  "aliases": [
    "CVE-2023-42714"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-862"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2023-12-04T01:15:10Z",
    "severity": "MODERATE"
  },
  "details": "In firewall service, there is a possible way to write permission usage records of an app due to a missing permission check. This could lead to local information disclosure with no additional execution privileges needed",
  "id": "GHSA-955j-rv6c-vgf9",
  "modified": "2023-12-07T15:30:37Z",
  "published": "2023-12-04T03:30:26Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2023-42714"
    },
    {
      "type": "WEB",
      "url": "https://www.unisoc.com/en_us/secy/announcementDetail/https://www.unisoc.com/en_us/secy/announcementDetail/1731138365803266049"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:L/AC:L/PR:L/UI:N/S:U/C:H/I:N/A:N",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-9562-R8V7-4W2H
Vulnerability from github – Published: 2025-01-02 12:32 – Updated: 2026-04-01 18:33Missing Authorization vulnerability in AyeCode AyeCode Connect allows Exploiting Incorrectly Configured Access Control Security Levels.This issue affects AyeCode Connect: from n/a through 1.3.8.
{
  "affected": [],
  "aliases": [
    "CVE-2024-56255"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-862"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2025-01-02T12:15:27Z",
    "severity": "MODERATE"
  },
  "details": "Missing Authorization vulnerability in AyeCode AyeCode Connect allows Exploiting Incorrectly Configured Access Control Security Levels.This issue affects AyeCode Connect: from n/a through 1.3.8.",
  "id": "GHSA-9562-r8v7-4w2h",
  "modified": "2026-04-01T18:33:00Z",
  "published": "2025-01-02T12:32:16Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2024-56255"
    },
    {
      "type": "WEB",
      "url": "https://patchstack.com/database/wordpress/plugin/ayecode-connect/vulnerability/wordpress-ayecode-connect-plugin-1-3-8-broken-access-control-vulnerability?_s_id=cve"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:N/I:L/A:N",
      "type": "CVSS_V3"
    }
  ]
}
Mitigation
- Divide the product into anonymous, normal, privileged, and administrative areas. Reduce the attack surface by carefully mapping roles with data and functionality. Use role-based access control (RBAC) [REF-229] to enforce the roles at the appropriate boundaries.
- Note that this approach may not protect against horizontal authorization, i.e., it will not protect a user from attacking others with the same role.
Mitigation
Ensure that access control checks are performed related to the business logic. These checks may be different than the access control checks that are applied to more generic resources such as files, connections, processes, memory, and database records. For example, a database may restrict access for medical records to a specific database user, but each record might only be intended to be accessible to the patient and the patient's doctor [REF-7].
Mitigation MIT-4.4
Strategy: Libraries or Frameworks
- Use a vetted library or framework that does not allow this weakness to occur or provides constructs that make this weakness easier to avoid.
- For example, consider using authorization frameworks such as the JAAS Authorization Framework [REF-233] and the OWASP ESAPI Access Control feature [REF-45].
Mitigation
- For web applications, make sure that the access control mechanism is enforced correctly at the server side on every page. Users should not be able to access any unauthorized functionality or information by simply requesting direct access to that page.
- One way to do this is to ensure that all pages containing sensitive information are not cached, and that all such pages restrict access to requests that are accompanied by an active and authenticated session token associated with a user who has the required permissions to access that page.
Mitigation
Use the access control capabilities of your operating system and server environment and define your access control lists accordingly. Use a "default deny" policy when defining these ACLs.
CAPEC-665: Exploitation of Thunderbolt Protection Flaws
An adversary leverages a firmware weakness within the Thunderbolt protocol, on a computing device to manipulate Thunderbolt controller firmware in order to exploit vulnerabilities in the implementation of authorization and verification schemes within Thunderbolt protection mechanisms. Upon gaining physical access to a target device, the adversary conducts high-level firmware manipulation of the victim Thunderbolt controller SPI (Serial Peripheral Interface) flash, through the use of a SPI Programing device and an external Thunderbolt device, typically as the target device is booting up. If successful, this allows the adversary to modify memory, subvert authentication mechanisms, spoof identities and content, and extract data and memory from the target device. Currently 7 major vulnerabilities exist within Thunderbolt protocol with 9 attack vectors as noted in the Execution Flow.